Question
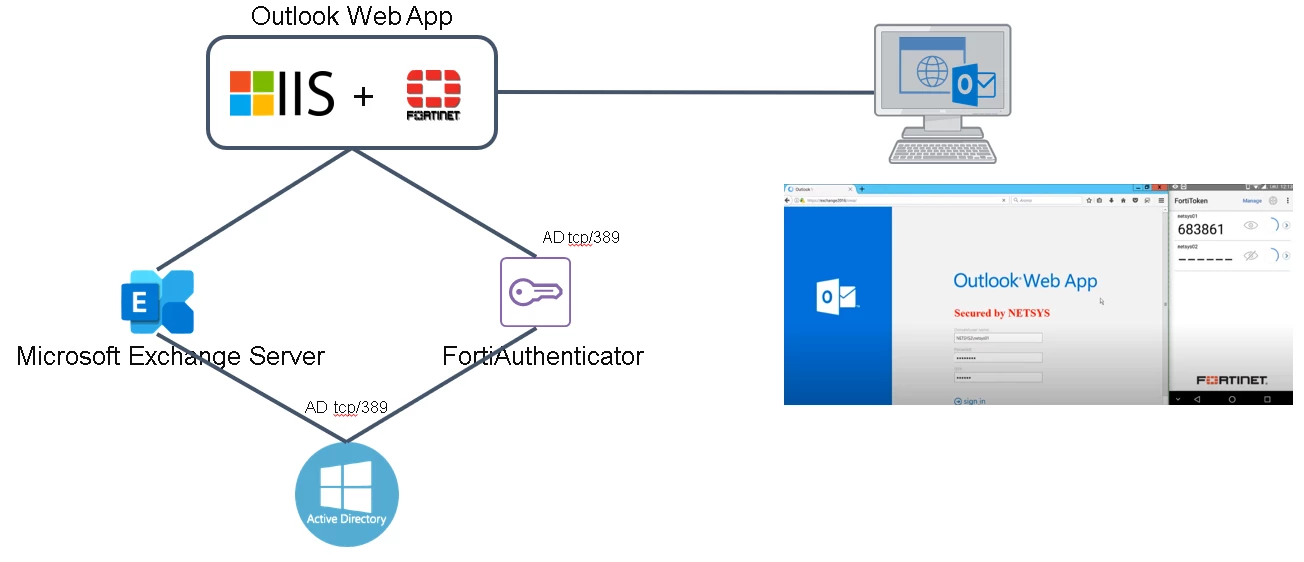
FortiAuthenticator OWA Authentication Process
I have two questions regarding the FortiAuthenticator OWA Agent:
When IIS is updated, is it necessary to reinstall the OWA Agent? (Assuming the latest version is being used)
Please refer to the diagram below. I would like to understand the entire process and sequence when users log in through a browser with the OWA Agent installed on IIS. Does the IIS+OWA Agent first authenticate the OTP with the Authenticator before proceeding with the account and password verification with AD? Or does the IIS+OWA Agent not perform account and password verification with AD? If so, does the Exchange Server still verify the account with AD in the end?