
Vassilis
Visitor III
February 12, 2023
Question

FortiAuthenticator on every sync resets the users to always have OTP

Hi,

We upgraded to v6.4.6, build1043 (GA) and we notice that on every sync from AD in order to retrieve the users it always resets on ALL users the option to have Token enable.


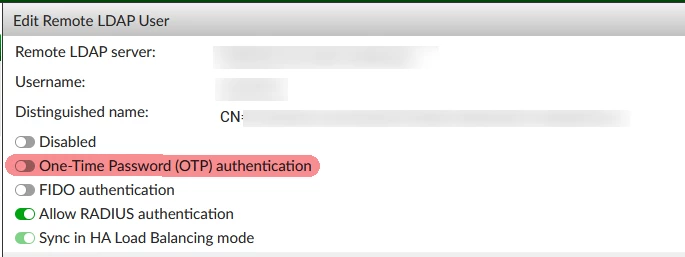
What i mean is we have many users were the OTP is disabled for some reason (we use SMS service), like below, one user the OTP is disabled
 

Vassilis_1-1676199167163.png


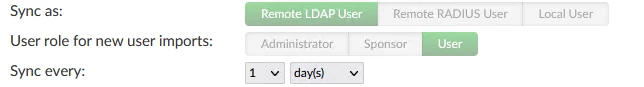
Now on every sync which we increased for one hour to one day in order to manage the issue (from Edit Remote LDAP User Synchronization Rule) 
Vassilis_2-1676199348759.png


what is happening is that for ALL users the option ONE Time Password (OTP) Authentication (from the first picture) gets enabled again.

That was not the issue on the previous version.


How can we stop this from happening ?


Thanks



3 replies

Vassilis
VassilisAuthor
Visitor III
February 13, 2023

Is there any update on this ?

It starts to be really annoying and time-consuming to return the settings on each user.


Please for your assist

Markus_M
Staff & Editor
Staff & Editor
February 13, 2023

Hi Vassilis,


could you post your remote user sync rule configuration? This is where the OTP would be set to enabled. When the user gets synchronized, then the user might get "corrected" again. If that was the case, we could maybe not import the users automatically, but manually, not update them. Usually the users do not really change membership or state, but of course, manual users need to be tracked as well. The user audit report can help on that (like a user hasn't been used since some days).


Best regards,


Markus

Best regards, Markus
Vassilis
VassilisAuthor
Visitor III
February 14, 2023

Hi Markus thanks for the reply. Here are the settings


Vassilis_0-1676361916100.png


Now if i understand the comment correct you are probably referring to the "SMS" setting. According to the yellow text box and what i understand from this is that the enabled setting means that it will sync the users from the group mention on the LDAP Filter ONLY for users who have the Mobile Number field


Vassilis_1-1676362014057.png

If i select None i have the impressions that it will sync ALL users on the security group mentioned in the LDAP Filter section regarding of mobile phone exists or not.


Cause i've seen it that it does not sync users that DO NOT have an mobile number.

I want to be very clear and i want to understand this.


Regards,

Vassilis


Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT

