

The_Nude_Deer
Explorer II
February 20, 2024
Solved

FortiAuthenticator LDAP groups used on Fortigate

  • February 20, 2024
  • 10 replies
  • 5500 views

I have recently set up some SSL VPN Portals on a Fortigate, that are mapped to specific groups, the Fortigate is a Radius client from the FAC, The FAC uses LDAP to look up the user in AD, then looks at RSA for a token to authenticate the users.


All of the above is working abolutely fine, except for groups being passed to the Firewall to be used in the Portal mappings and Policies. I have to create a user on the Gate as a remote radius user, using the same name exactly that the FAC uses. this works... but some of the portals have 30-40 users. I had to create 30-40 individial users with the same name as the FAC.


Groups dont work in the same way, The documentation say you just create a Firewall Group with the same name on the Firewall, and make sure the FAC is sending the group-name attribute, which in my case it is., but it doesnt work, I have to switch back to using username. is this a bug?
Best answer by ozkanaltas

Hello @The_Nude_Deer ,


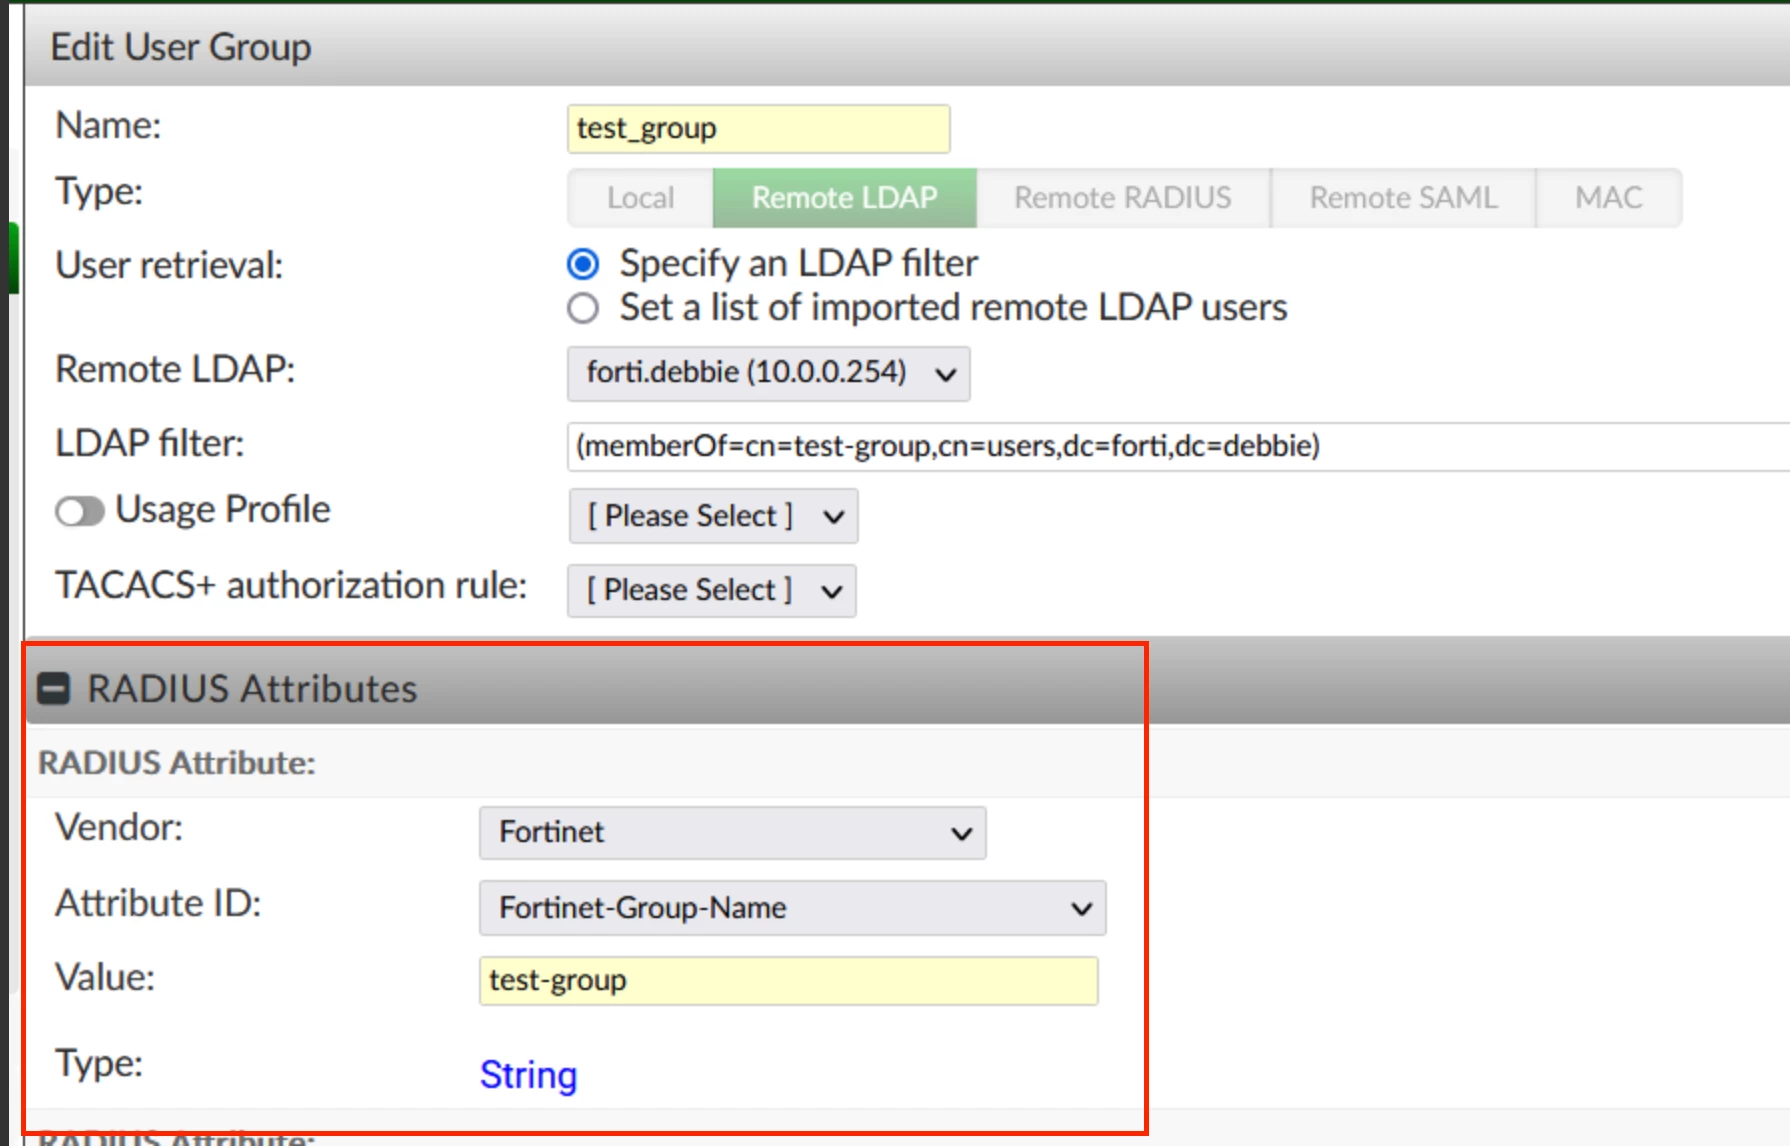
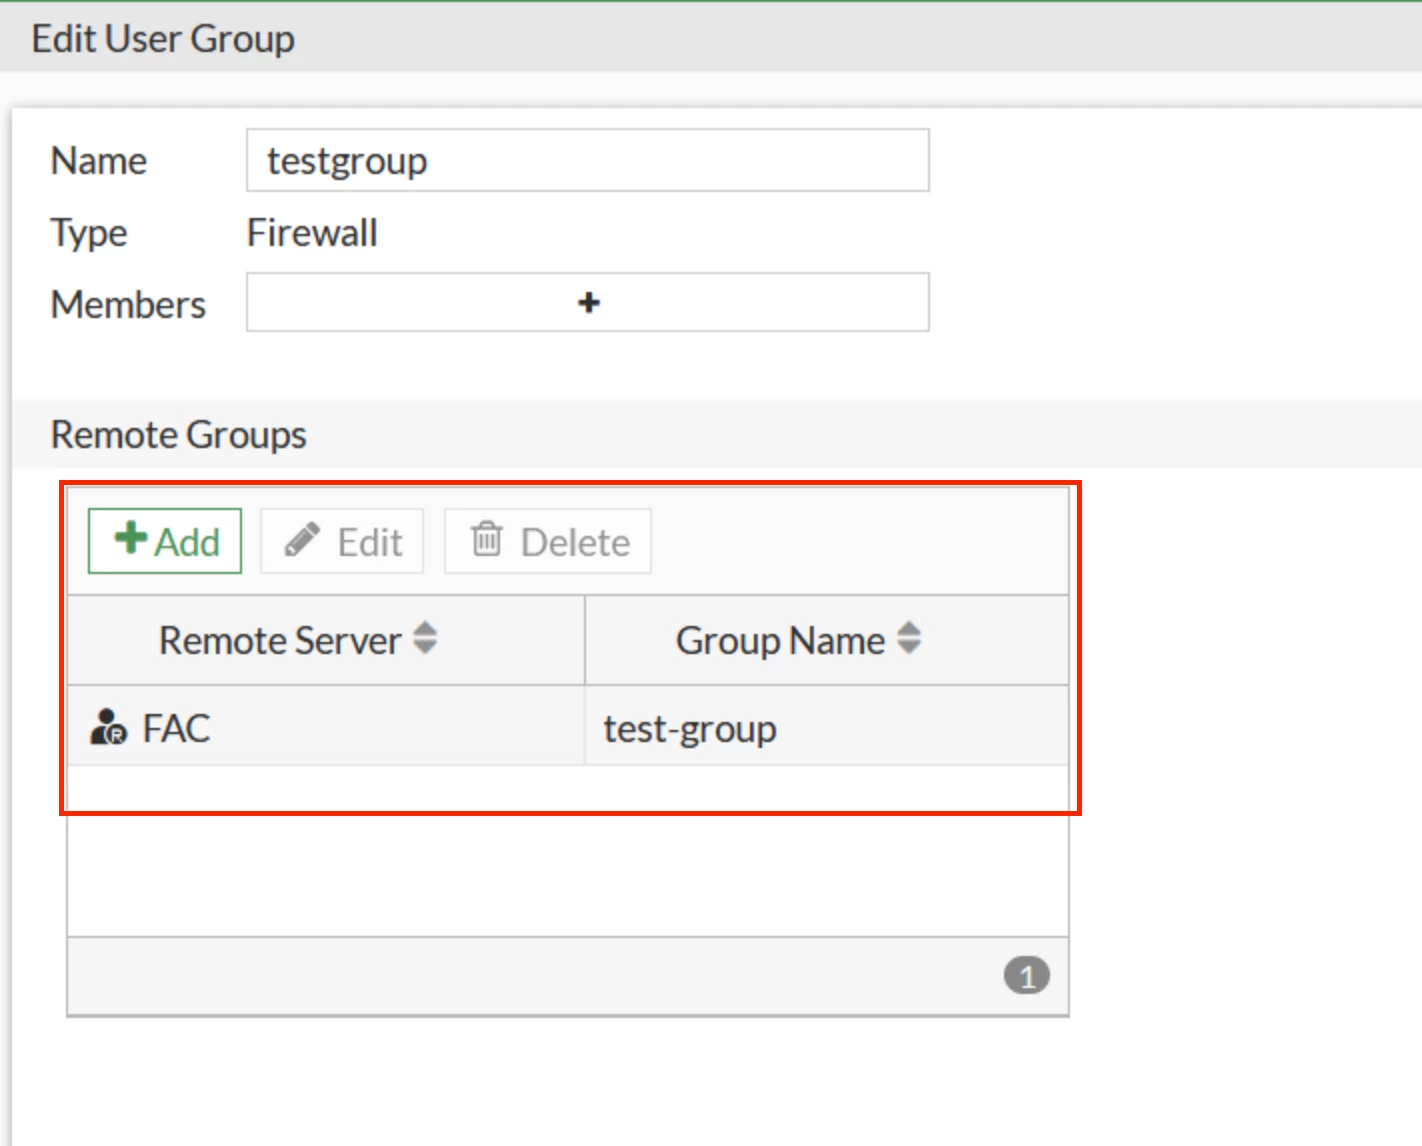
Group name is not important. The important thing is radius attributes and the Fortigate group name filter. The Radius Attribute and Fortigate group filter should be the same. Your configuration is like this right?


image.png


image.png

10 replies

ozkanaltas
Valued Contributor III
February 20, 2024

Hello @The_Nude_Deer ,


Actually, the group-name attribute should work. Can you share the Fortiauthenticator configuration as a screenshot with us? 


Also if you want to troubleshoot this issue, you can get a pcap file from a firewall for radius traffic. You can inspect the radius response FortiAuthenticator to FortiGate with this capture. If you can see the group attribute in the response packet Fortiauthenticator sends the group attribute but Fortigate can't process this attribute. 


Additionally, you can read this. It's the same thing you want. 


https://community.fortinet.com/t5/Support-Forum/How-to-filter-user-group-in-FortiAuthenticator/m-p/226021/highlight/true#M200864

The_Nude_Deer
Explorer II
February 20, 2024

Yes, I have done exactly what you have described in that thread, Create a Group on the FAC, added the remote users, gave it a name "phase1_test" , created a remote user group on the Gate with EXACTLY the same name and using remote radius server as the remote group, Fails every time, unless i add the exact username to the Firewall group as a remote user


I am unable to share, as its live production testing, but I have done exactly that


ozkanaltas
Valued Contributor III
February 20, 2024

Hello @The_Nude_Deer ,


Group name is not important. The important thing is radius attributes and the Fortigate group name filter. The Radius Attribute and Fortigate group filter should be the same. Your configuration is like this right?


image.png


image.png

The_Nude_Deer
Explorer II
February 20, 2024

Exactly like that...doubled checked it, it wont work, as soon as I add the user instead of the group it works

The_Nude_Deer
Explorer II
February 20, 2024

i just removed the underscore in the radius attr and it worked? is that possible?

ozkanaltas
Valued Contributor III
February 20, 2024

Hello @The_Nude_Deer ,


I think it's not normal. Maybe there is a bug in your version. Which version do you use? 

The_Nude_Deer
Explorer II
February 20, 2024

6.6.0 build 1617

ozkanaltas
Valued Contributor III
February 20, 2024

Hello @The_Nude_Deer ,


I didn't find anything (bug, known issue, etc.) about this. Maybe you can open a ticket to support services related to your problem. They can inspect the problem and respond to you.

The_Nude_Deer
Explorer II
February 23, 2024

It wasn't a bug, the group name had "-" but the Radius Attribute had "_" Layer 8 Issue by me! 

Thank you

ozkanaltas
Valued Contributor III
February 23, 2024

Hello @The_Nude_Deer ,


Thank you for your response.


I liked this saying, "Layer 8 Issue" :) 

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT


