kyle-hsuan
Explorer
August 13, 2026
Question

FortiAnalyzer third-party log parser

  • August 13, 2026
  • 2 replies
  • 109 views

Hi


I'm trying to collect Palo Alto logs into FAZ.

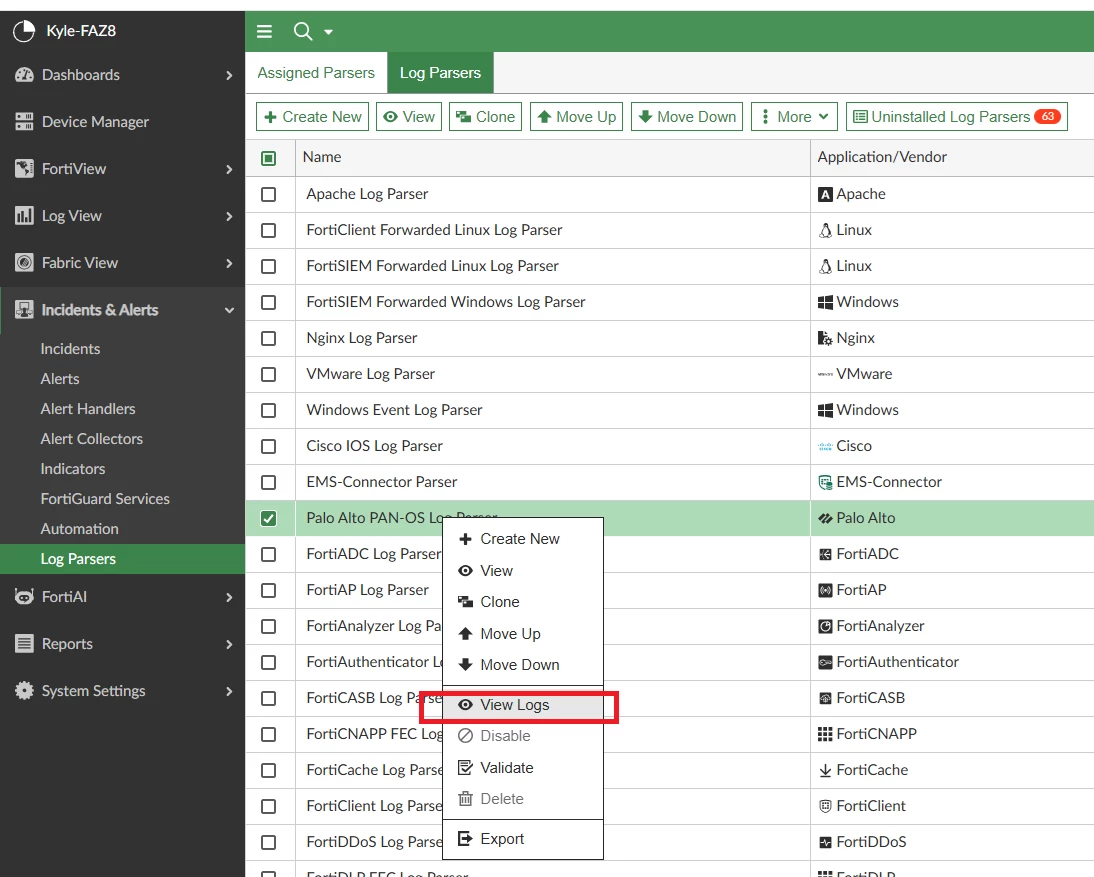
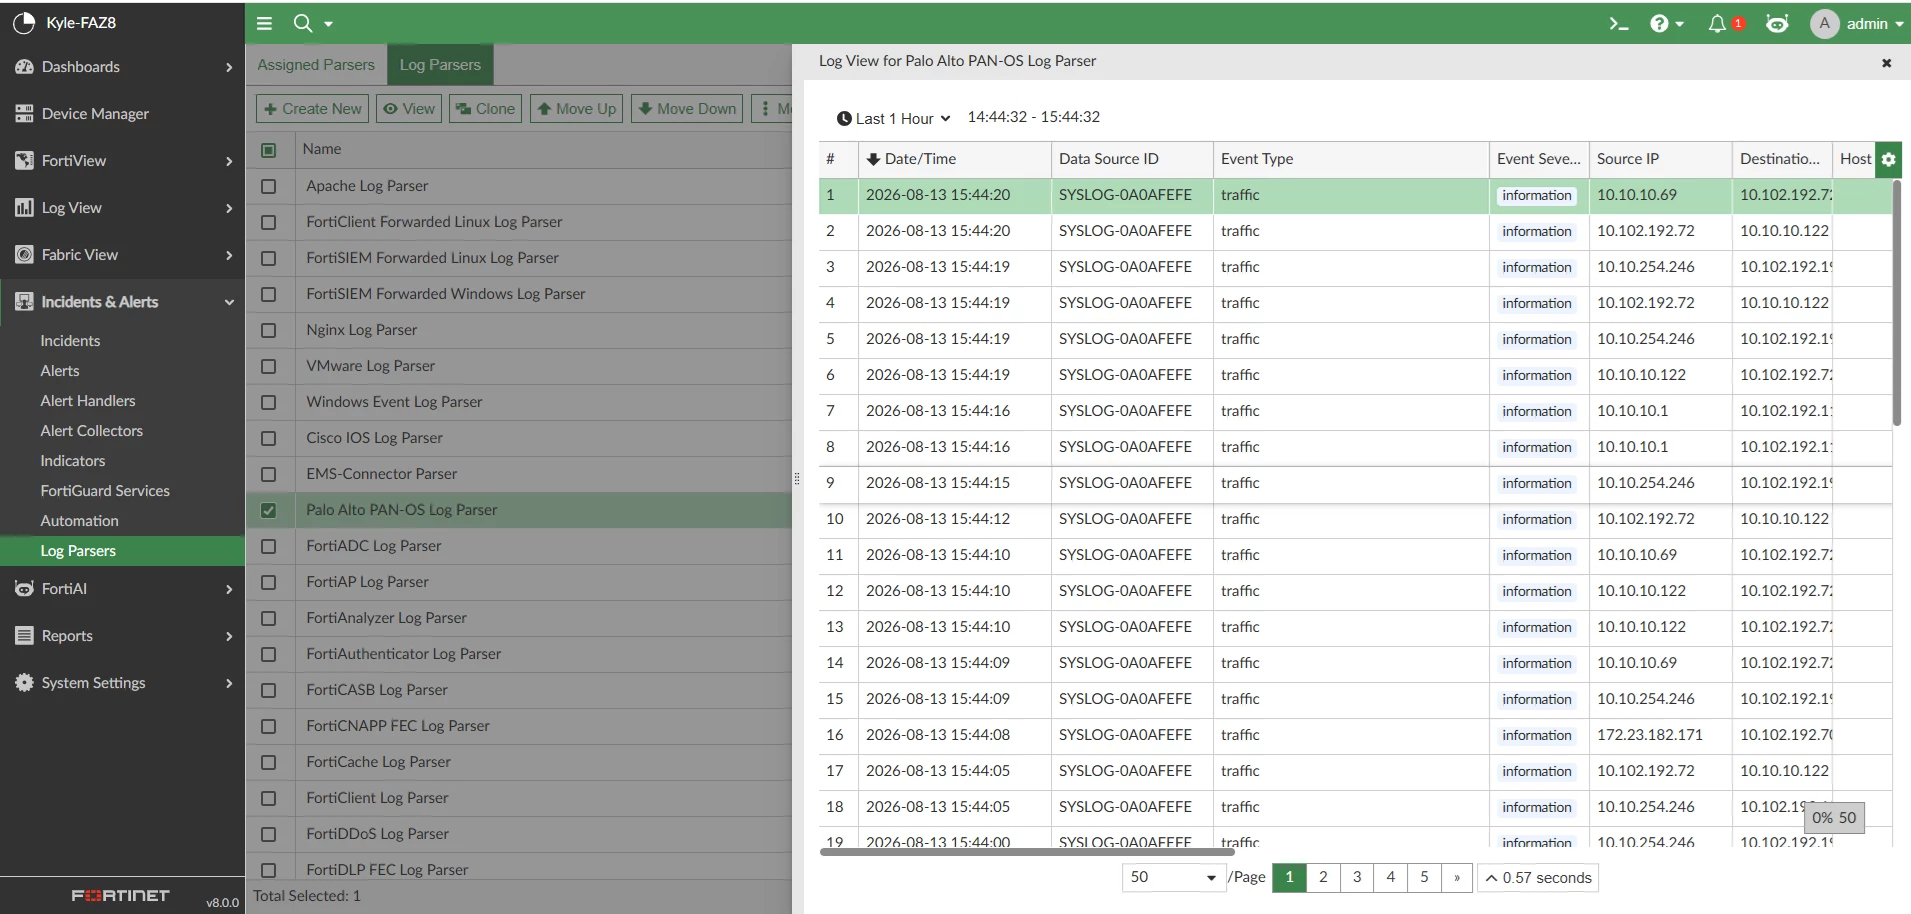
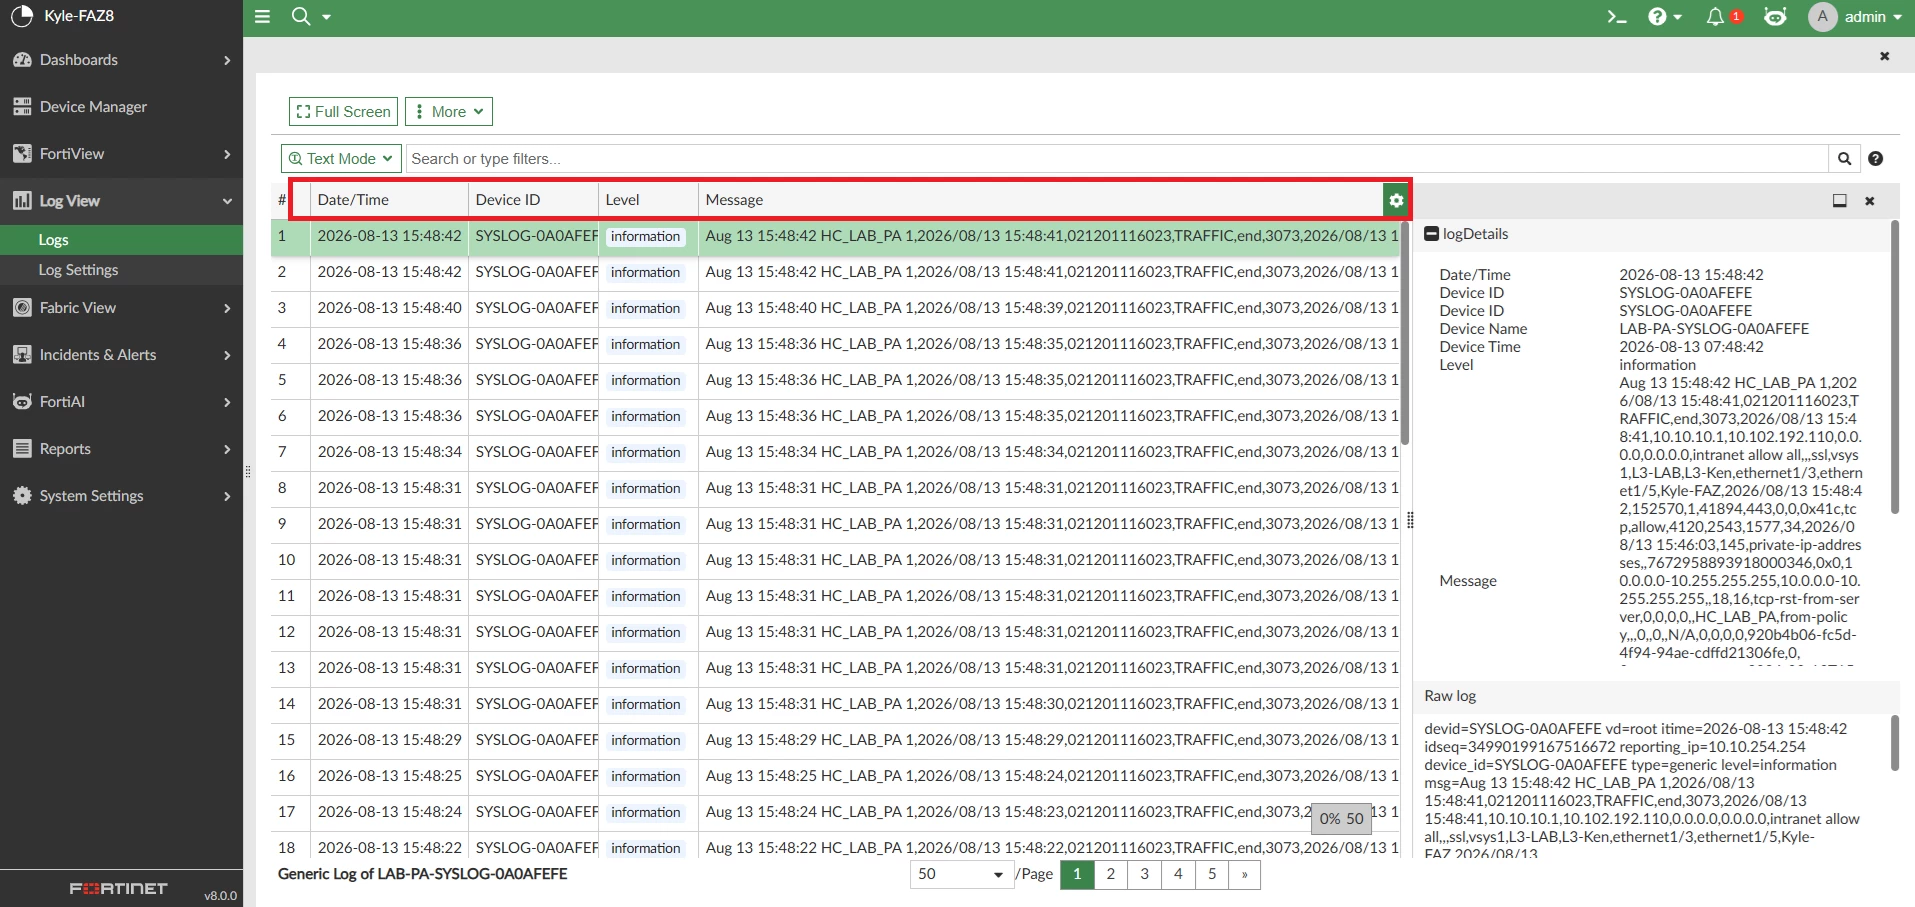
If I want to view the normalized logs, do I have to use the log parser?

cause I use Log View -->  Log Browse, it only showing raw log.


2 replies

kyle-hsuan
Explorer
August 17, 2026

another question

Can a playbook be triggered based on PA logs?

Muttahar_Rehman
Explorer II
August 17, 2026

Hi,

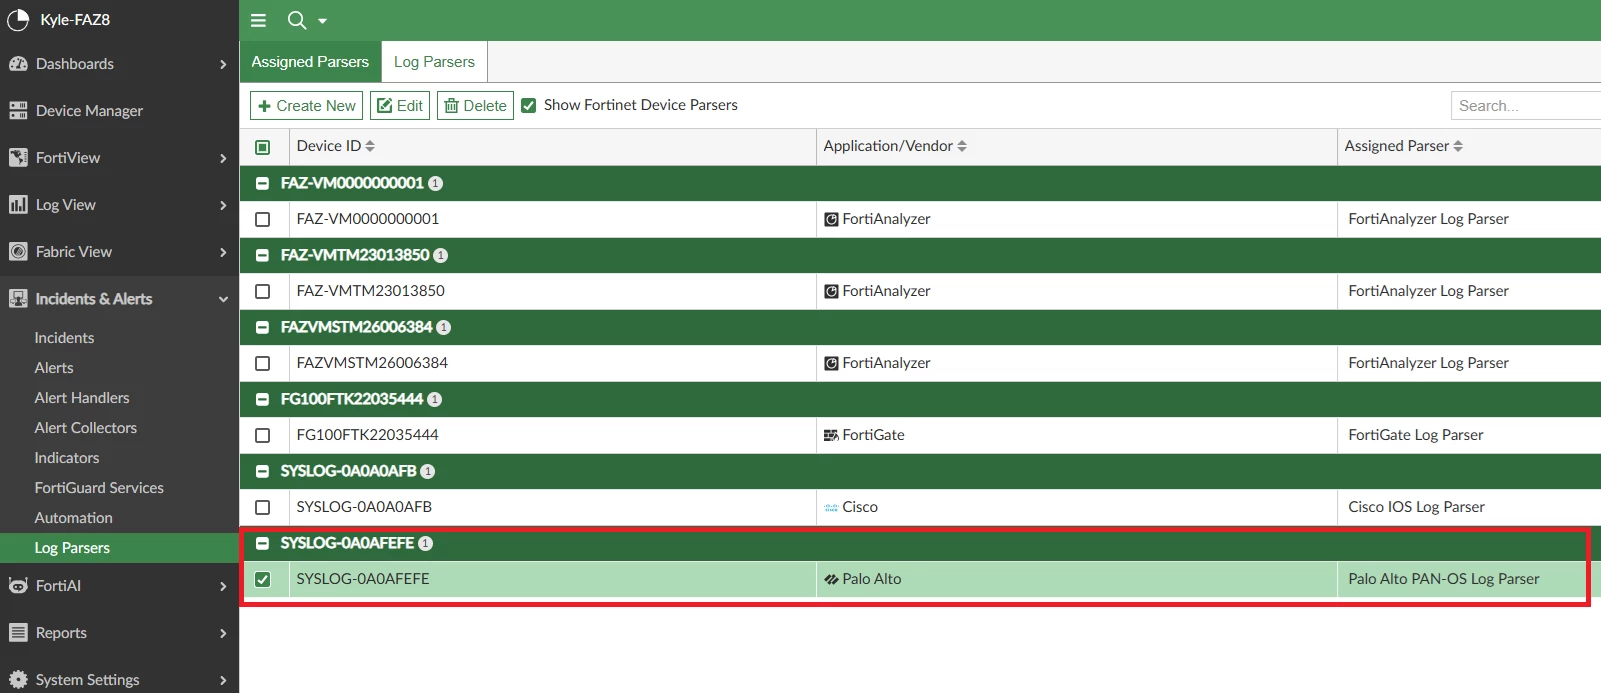
To get normalized fields, yes you need to configure the Log Parser:

  1. Go to System Settings → Advanced → Log Forwarding (or in some builds: Device Manager → Add Device → add as "Syslog" or "Generic" device, then configure a parser)
  2. In newer FAZ versions (7.x/8.x), the relevant section is usually:
    System Settings → Log Parser (or Device Log Settings → Custom Parser)
  3. You'll create a custom log parsing profile where you:
    • Define the field mapping (regex or delimiter-based) to extract Palo Alto's syslog fields
    • Map them to FortiAnalyzer's normalized field names (srcip, dstip, srcport, dstport, action, policyid, etc.)
  4. Apply that parser to the device entry representing your Palo Alto firewall in FAZ.
Thanks, R3hsec
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!