



Encryption Using an Obsolete Cipher Suite, After CA cert and strong-crypto enable
I have DPi setup and running on one Policy on our cluster (2 3700D v5.2.4,build688). The rule is only for my laptop. After following the Cookbook steps on importing the Fortigate CA onto my laptop everything appears to be working very well. Safe search is working and I haven't ran into any other major problems except Skype on 365, but I believe it might be tied into the current situation I'm trying to solve. On Chrome (again everything works well) I click on the SSL link in the URL and it shows me that Chrome verified the FortiGate CA..... Then it says:
"Your connection to www.netflix.com is encrypted using an obsolete cipher suite. The connection is encrypted using AEA_128_CBC, with HMAC-SHA1 for message authetnication and ECDHE_RSA as the key exchange mechanism.
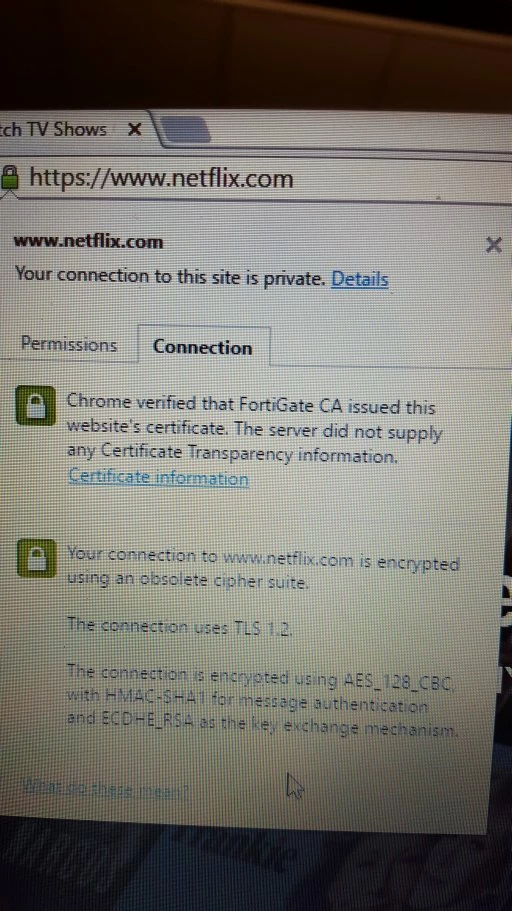
If I lookup the same thing on my desktop (which doesn't hit a Policy that uses DPI) I don't get the obsolete cipher error. I did connect to the CLI and ran the: "set strong-crypto enable" , but I still get the error. Do I need to configure the Fortigate more?
Any help would be appreciated!
Thanks in advance!
B

