



Question
DoS policy in FortiGate
Hi, friends.
Are the DoS policies created in fortigate necessary when having HTTPS and HTTP publishing?
I have a SIP publishing policy on the firewall but I'm not sure if I should create DoS policies or not.
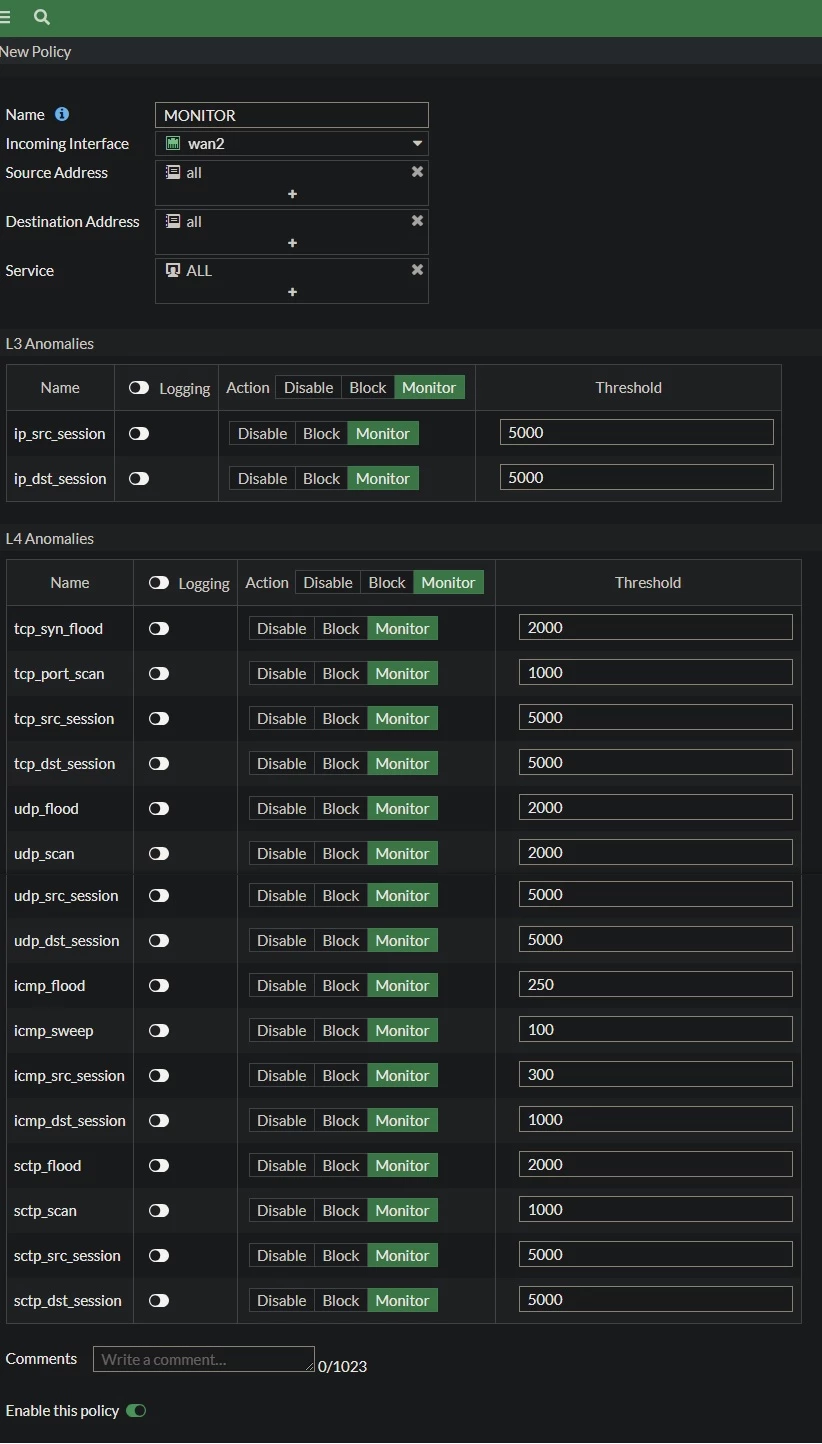
To avoid blocking problems due to false positives perhaps, I am configuring a DDos profile in MONITOR mode, but I have a question, what is the difference between "logging" and "monitor"?
I attach an image of my MONITOR profile.
Could you help me with this query please.

