



Question
dialup ipsec VPN + many interfaces/subnets
Hi ! I' m trying to setup access from notebook (FortiClient) to all my subnets on diferent interfaces (picture below). I set " interface mode" ipsec VPN with proper firewall polices (I think) but I can reach ONLY FIRST subnet definied in Forticlient. 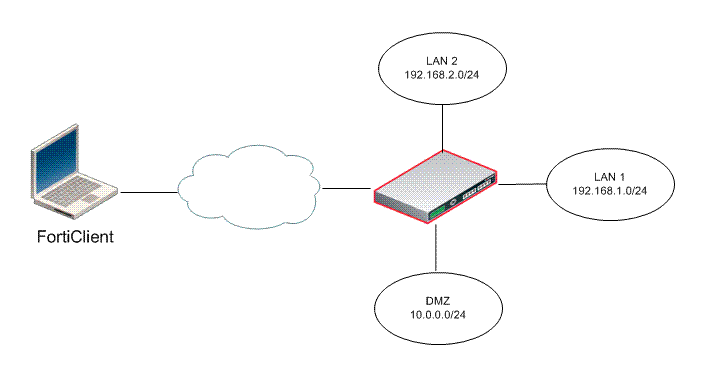 If I change sequence of subnets in client I can reach next one (alway only first one) so I think Fortigate config is OK. When I sniff traffic I can see that all packet (tested with icmp/ping) to all subnets are ok - I mean - echo request reach targets in every subnet AND echo replay is COME BACK through dialupVPN_interface !!! Do I need to setup 3 x Quick Mode Selectors (with proper subnets) in phase2 in this case ? Maybe I need to use agressive mode ? (but I think it doesn' t metter) Does anyone made config like this ? ... any working example ? ... Thanks in advance Dominik
