Reshans
Visitor III
May 12, 2025
Solved

dial up vpn hq to hub and hub to hq traffic working but branch to branch traffic not workingno advpn

  • May 12, 2025
  • 2 replies
  • 881 views

i setup this hub site with diaup ipsec option with igbp my issue spoke1 to spoke 2 not ping
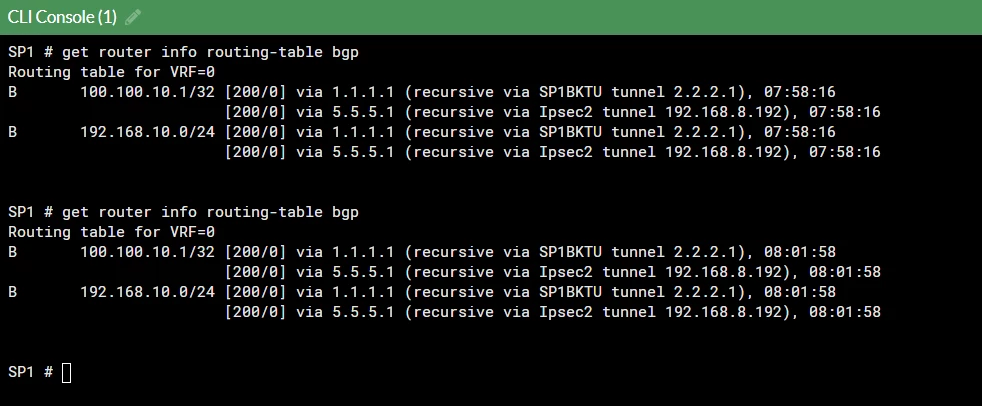
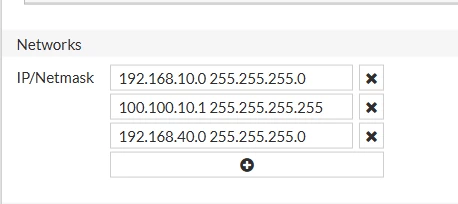
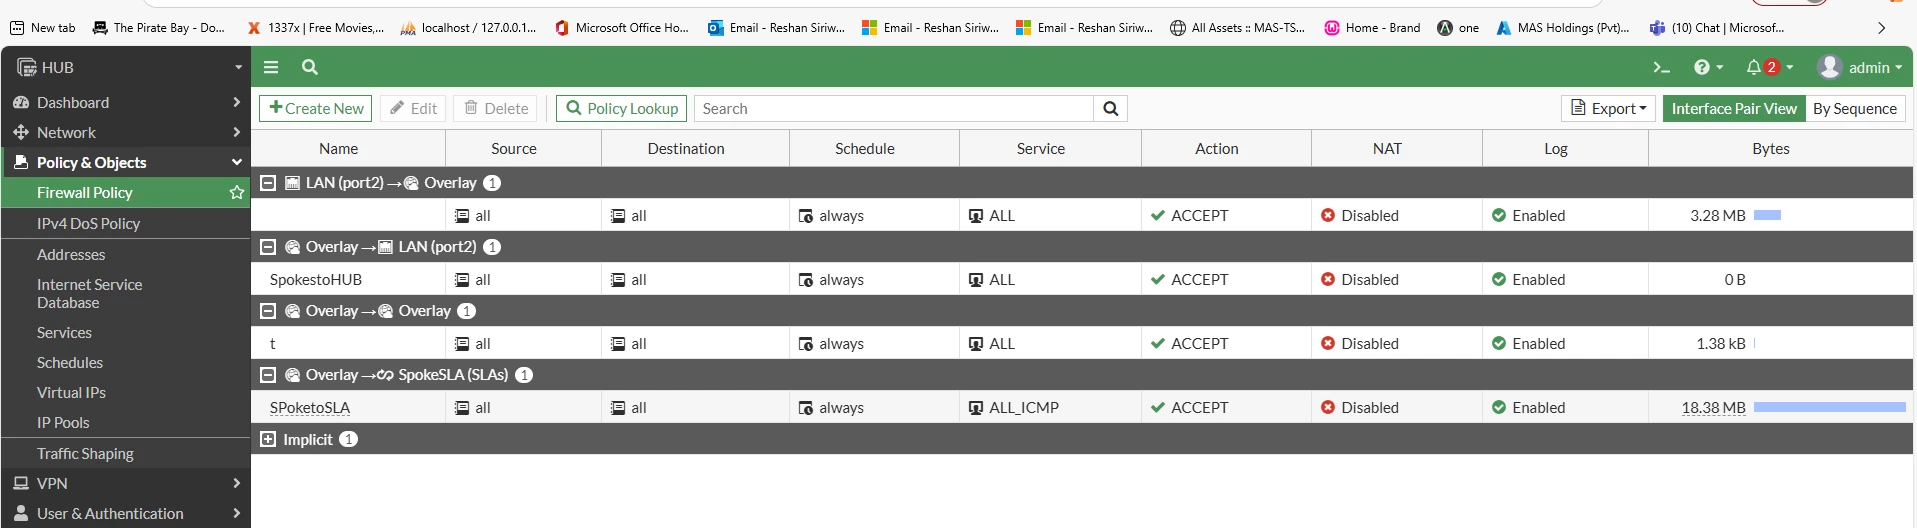
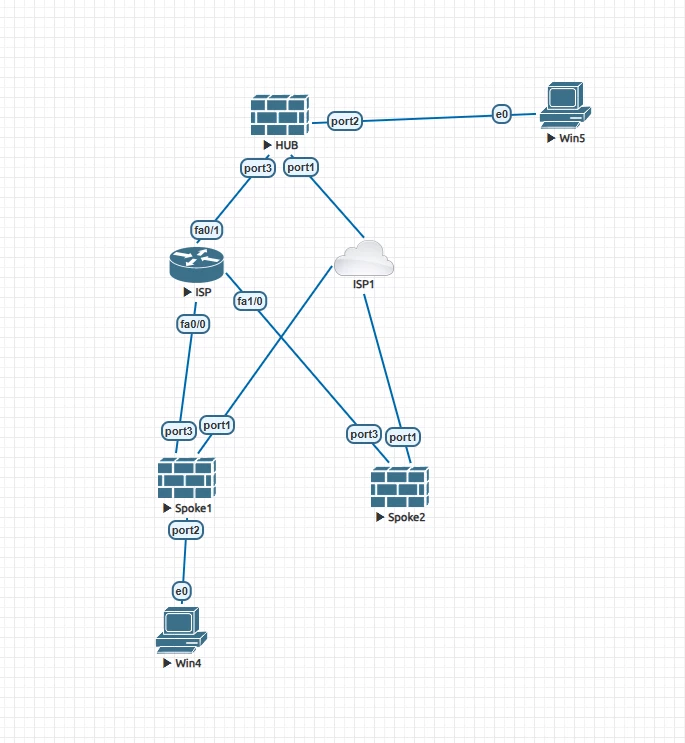
But Branch 1 not showing in routing table branch 2 subnet.pngHUB side bgp network advertise branch 2 network.pngHUB Side Policy.pngtopology.png

Best answer by syordanov

Dear Reshans,


The provided routing table in the first screenshot is from spoke 'SP1'?
Make sure the following :

HUB -> IPSec-> auto-discovery-sender is enabled
HUB -> BGP -> route-reflector-client is enabled

Spokes -> IPSec-> auto-discovery-receiver is enabled
Spokes -> BGP-> recursive-next-hop is enabled
Spokes -> BGP-> additional-path option is enabled

When the ICMP runns from SP1 to SP2, please run an IKE debug + sniffer to see if there is a traffic between SP1 and SP2 (IKE/ ESP or NAT-T 4500 UDP) :

IKE debug , run and check what happens on the HUB and spokes:


diagnose debug contime timestamp enable
diagnose debug application ike -1
diagnose debug enable


Once you have the debug, please check for ' send shortcut-query' / 'SHORTCUT_OFFER'

Sniffer:


diagnose sniffer packet any " host x.x.x.x and host y.y.y.y" 4 0 l

 Where x.x.x.x is the WAN IP of SP1 and y.y.y.y is the WAN IP of SP2. Make sure that there are no restrictions between SP1 and SP2 over port3 and port1(shortcut tunnel between SP1 with port3 and SP2 with port1).


Best regards,

Fortinet

2 replies

syordanov
Staff
syordanovAnswer
Staff
May 12, 2025

Dear Reshans,


The provided routing table in the first screenshot is from spoke 'SP1'?
Make sure the following :

HUB -> IPSec-> auto-discovery-sender is enabled
HUB -> BGP -> route-reflector-client is enabled

Spokes -> IPSec-> auto-discovery-receiver is enabled
Spokes -> BGP-> recursive-next-hop is enabled
Spokes -> BGP-> additional-path option is enabled

When the ICMP runns from SP1 to SP2, please run an IKE debug + sniffer to see if there is a traffic between SP1 and SP2 (IKE/ ESP or NAT-T 4500 UDP) :

IKE debug , run and check what happens on the HUB and spokes:


diagnose debug contime timestamp enable
diagnose debug application ike -1
diagnose debug enable


Once you have the debug, please check for ' send shortcut-query' / 'SHORTCUT_OFFER'

Sniffer:


diagnose sniffer packet any " host x.x.x.x and host y.y.y.y" 4 0 l

 Where x.x.x.x is the WAN IP of SP1 and y.y.y.y is the WAN IP of SP2. Make sure that there are no restrictions between SP1 and SP2 over port3 and port1(shortcut tunnel between SP1 with port3 and SP2 with port1).


Best regards,

Fortinet

Reshans
ReshansAuthor
Visitor III
May 12, 2025

Yes after enter above config my issue now sorted.


Spoke 1 to Spoke 2 ping successful.


Router received from hub .png

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT