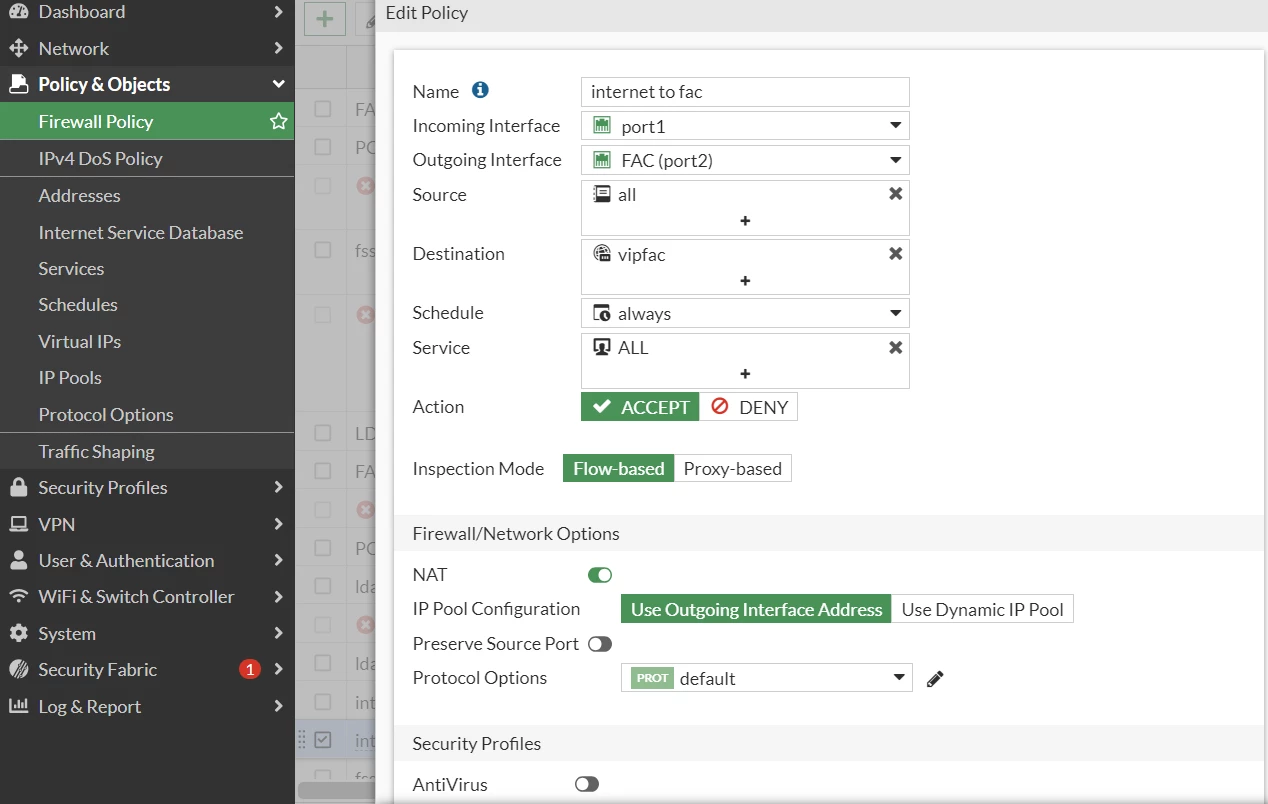
Custmized local in policy doesn't work
Hi guys, I'm trying to make a server accessible from WAN, I configured virtual ip and port for the server, and then I created a local in policy to test :
config firewall local-in-policy
edit 1
set intf "port1"
set srcaddr "all"
set dstaddr "all"
set action accept
set service "ALL"
set schedule "always"
next
end
but I cannot access the server and related traffic still matches policy 0 :
id=20085 trace_id=114 func=print_pkt_detail line=5822 msg="vd-root:0 received a packet(proto=6, [my ip]:2084->[FW IP]:50022) from port1. flag [S], seq 2666835964, ack 0, win 64240"
id=20085 trace_id=114 func=init_ip_session_common line=5993 msg="allocate a new session-01e45466"
id=20085 trace_id=114 func=vf_ip_route_input_common line=2615 msg="find a route: flag=80000000 gw-[FW IP] via root"
id=20085 trace_id=114 func=fw_local_in_handler line=447 msg="iprope_in_check() check failed on policy 0, drop"
Am I doing it wrong? Please help, thanks!