
efelledi
New Member
January 6, 2022
Solved

Couldn't get IP address

  • January 6, 2022
  • 9 replies
  • 21816 views

I have FG 100 E, and I have it setup
DHCP Server
Address range 192.168.2.2-192.168.2.254
Netmask 255.255.255.0
is there something missing so that some devices sometimes can't get the IP address
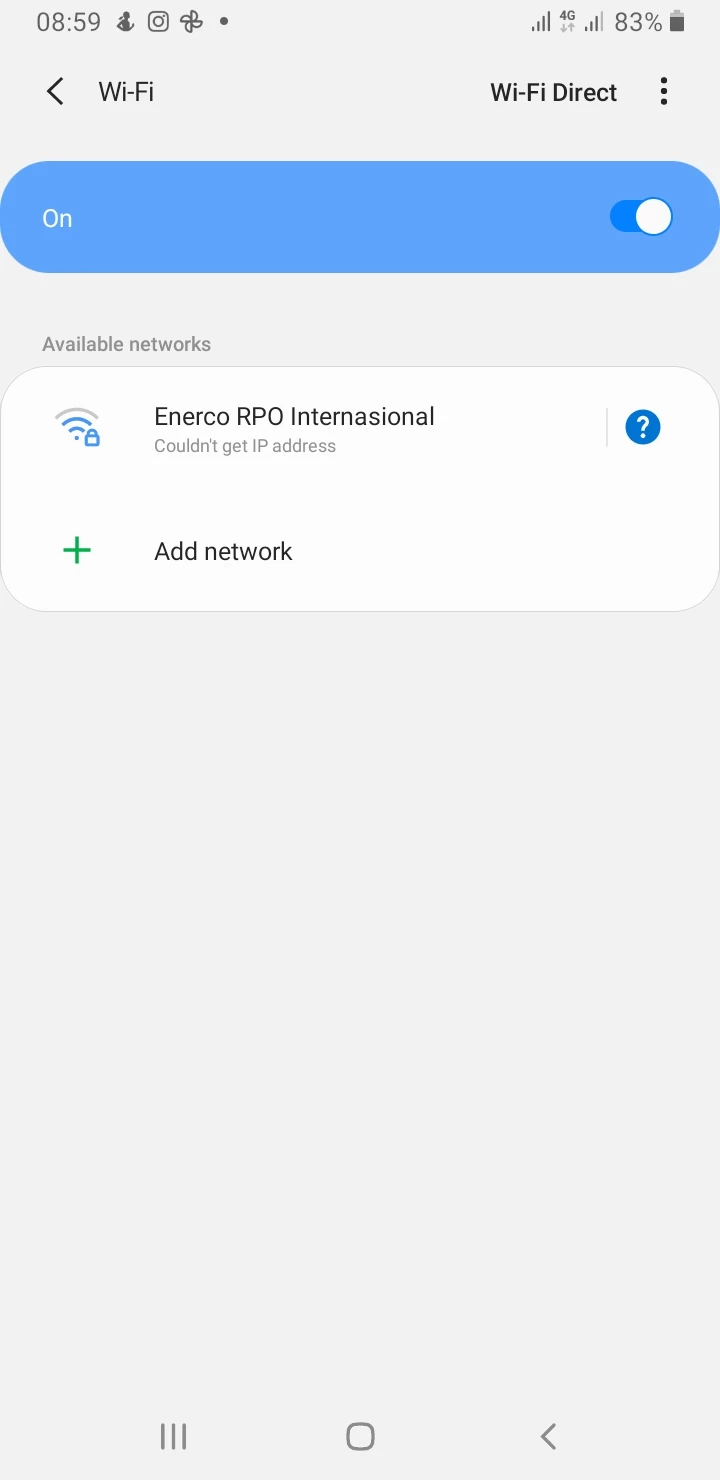
Screenshot_20220106-085938_Settings.jpg


Thanks.

Best answer by andrewbailey

Hi efelledi,


The key question is how many users and devices will access this interface over the course of 1 week?


At the moment you have set the “Lease Time” to 604800 seconds (7 days). That means that every device attaching to the interface will have an IP address reserved for the next 7 days.


So in your original config (subnet 255.255.255.0) you had 252 IP addresses available to be leased out.


If device number 253 tries connect to this interface over the course of a week (eg your phone) no addresses will be available to be leased out.


So Alex is right- you can make the subnet bigger if you need to allow for more devices.


Or if you only ever have a few guest devices that come and go each day with new devices the next make the lease time shorter to allow the IP addresses to be reused. 


I would typically use a 4 hour lease time (14400 seconds). That’s enough for devices coming and going and the DHCP protocol doesn’t generate a lot of traffic.


If you don’t have a clear idea how many devices will use this interface I would make the lease time shorter anyway. 7 days is unusually long I think.


Hope that helps you.


Kind Regards,


Andy.

9 replies

AlexC-FTNT
Staff
Staff
January 6, 2022

"Couldn't get IP address" in most cases it means that the pool of IPs is exhausted. The clients are probably not releasing the IPs, so this can happen even if you don't see 253 active users at the same time.

You can start by increasing the range of IPs that FortiGate can hand out to clients (starting with a /23), or lower the time these IPs are assigned.

If you want to troubleshoot the DHCP message exchange on the fortigate, you can run a packet capture filtered to ports 67 and 68 and/or a debug:
diag debug app dhcpd -1

diag debug enable

efelledi
efellediAuthor
New Member
January 6, 2022

Hi AlexC
Thanks, please notice this IP what should i add.

Address range.jpg

AlexC-FTNT
Staff
Staff
January 6, 2022

Hi Efel, 

Right now, your Address range in DHCP server has 253 IPs (.2 > .254)

If you change the IP mask to 255.255.254.0 you will double the number of available IPs in the DHCP range: 192.168.2.2 - 192.168.3.254 
Make sure that this network doesn't overlap any other networks you may have on the FortiGate.

efelledi
efellediAuthor
New Member
January 6, 2022

Dear AlexC

Is the change like this?
Address range Rubah.jpg

AlexC-FTNT
Staff
Staff
January 6, 2022

The answer is yes, but you should get the confidence to make these changes without asking on a public forum for such basic changes ;) In the worst case, you break something, then you will have to fix it and learn a lesson in the process.

vak0
Explorer
March 6, 2025

Hi Guys,


I recently enrolled in this course but i am have a problem with my DHCP i think its full and how do i manage my firewall remotely?


Regards

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!


