

bettioool
New Member
May 13, 2024
Question

Connection from VLAN to VIP does not work

  • May 13, 2024
  • 10 replies
  • 3271 views

Hello everyone,
I am in the following configuration. I have 3 VLANs (which will grow in the future) which host servers offering services (1 per VLAN).

These Servers have configured a VIP One to One, and on the policy an IP Pool with the same IP as the VIP.

If I try to connect from the various servers in these VLANs to the servers' VIP, it does not work.
For example from Server 11 I try to connect to the VIP of Server 21 or 31, the connection does not work

How can I solve this? I attach for simplicity a diagram showing the current configuration.
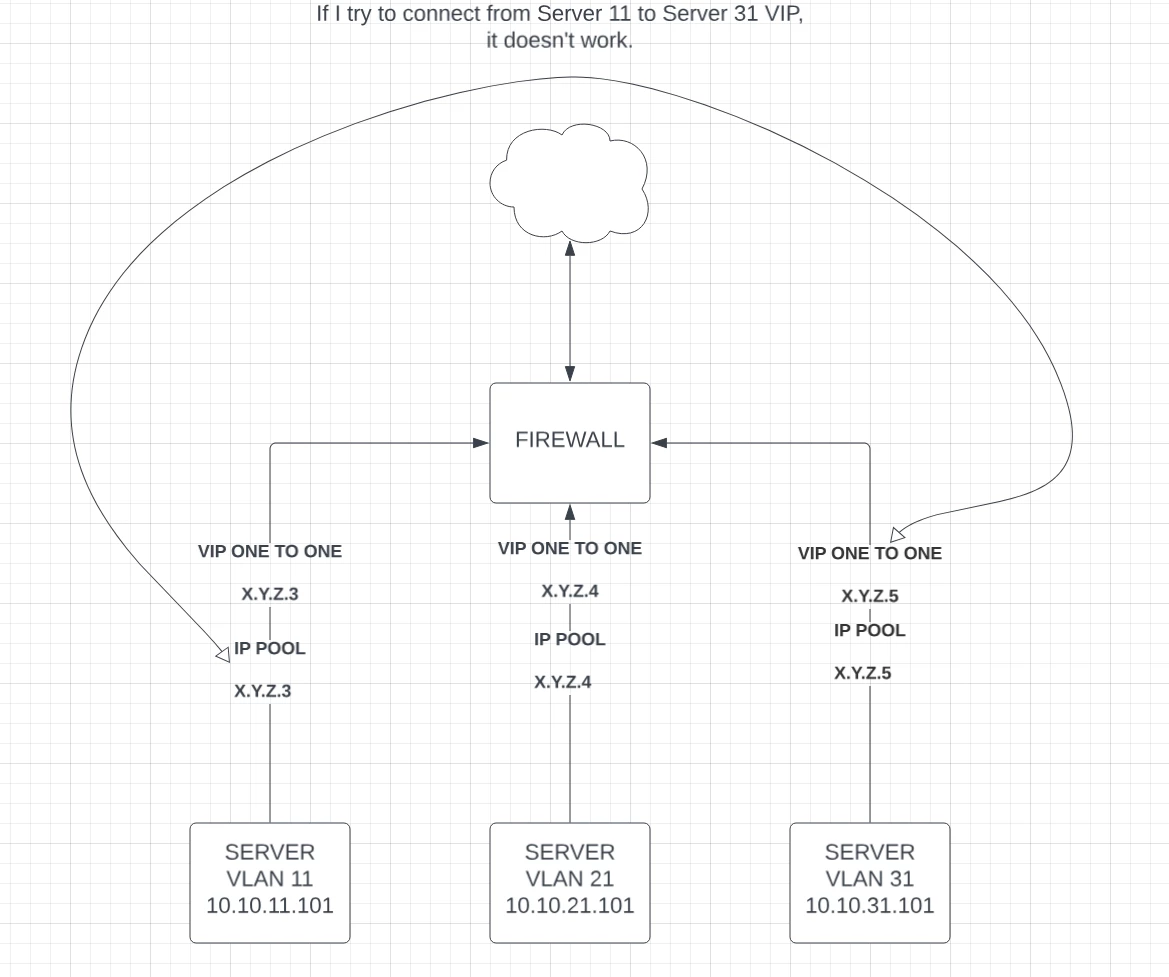
 

Immagine 2024-05-13 121901.png

These the policy configured for VLAN


config firewall vip     edit "VIP Libraesva XXXX"         set uuid b4f0161e-ea9b-51ee-e7ea-5c6c30663786         set extip X.X.X.103         set mappedip "10.X.21.X"         set extintf "any"         set color 8     next end  config firewall ippool     edit "IP Pool Libraesva XXX"         set startip X.X.X.103         set endip X.X.X.103     next end  config firewall policy     edit 44         set name "Internet to VIP XXXX Esva HTTPS"         set uuid 4e622af2-ecfa-51ee-d4d2-7074d2965dca         set srcintf "virtual-wan-link"         set dstintf "VLAN-54"         set action accept         set srcaddr "all"         set dstaddr "VIP Libraesva XXXX"         set schedule "always"         set service "HTTPS"         set utm-status enable         set ssl-ssh-profile "certificate-inspection"         set av-profile "g-default"         set webfilter-profile "g-default"         set ips-sensor "g-default"         set application-list "g-default"         set logtraffic all     next end  config firewall policy     edit 35         set name "XXXX Esva to Internet"         set uuid 306ab010-ea9c-51ee-db4f-01ba73aaf031         set srcintf "VLAN-54"         set dstintf "virtual-wan-link"         set action accept         set srcaddr "VLAN 54 - XXXX Libraesva"         set dstaddr "all"         set schedule "always"         set service "ALL"         set utm-status enable         set ssl-ssh-profile "certificate-inspection"         set av-profile "g-default"         set webfilter-profile "g-default"         set ips-sensor "g-default"         set application-list "g-default"         set logtraffic all         set nat enable         set ippool enable         set poolname "IP Pool Libraesva XXXX"     next end


 Thanks

Regards

10 replies

ozkanaltas
Valued Contributor III
May 13, 2024

Hello @bettioool ,


Are you sure that you did enough configuration on the firewall policy? 


Can you share these command's output with us? After running these commands, can yo try to access your server? 


diagnose debug disable diagnose debug flow trace stop diagnose debug flow filter clear diagnose debug reset  diagnose debug flow filter saddr  <SRC_IP> diagnose debug flow filter daddr <DST_IP> diagnose debug flow show console enable diagnose debug console timestamp enable diagnose debug flow trace start 100 diagnose debug enable


bettioool
bettiooolAuthor
New Member
May 13, 2024

Hi @ozkanaltas ,

here the output of the commands:


id=20085 trace_id=1 func=print_pkt_detail line=5955 msg="vd-h-services:0 received a packet(proto=1, 10.127.22.101:5->209.227.211.X:2048) tun_id=0.0.0.0 from VLAN-22. type=8, code=0, id=5, seq=85." id=20085 trace_id=1 func=init_ip_session_common line=6135 msg="allocate a new session-00144d20, tun_id=0.0.0.0" id=20085 trace_id=1 func=get_new_addr line=1227 msg="find DNAT: IP-10.127.54.101, port-0(fixed port)" id=20085 trace_id=1 func=fw_pre_route_handler line=182 msg="VIP-10.127.54.101:5, outdev-unknown" id=20085 trace_id=1 func=__ip_session_run_tuple line=3560 msg="DNAT 209.227.211.X:8->10.127.54.101:5" id=20085 trace_id=1 func=__vf_ip_route_input_rcu line=1999 msg="find a route: flag=00000000 gw-0.0.0.0 via VLAN-54" id=20085 trace_id=1 func=fw_forward_handler line=726 msg="Denied by forward policy check (policy 0)" id=20085 trace_id=2 func=print_pkt_detail line=5955 msg="vd-h-services:0 received a packet(proto=1, 10.127.22.101:5->209.227.211.X:2048) tun_id=0.0.0.0 from VLAN-22. type=8, code=0, id=5, seq=86." id=20085 trace_id=2 func=init_ip_session_common line=6135 msg="allocate a new session-00144d37, tun_id=0.0.0.0" id=20085 trace_id=2 func=get_new_addr line=1227 msg="find DNAT: IP-10.127.54.101, port-0(fixed port)" id=20085 trace_id=2 func=fw_pre_route_handler line=182 msg="VIP-10.127.54.101:5, outdev-unknown" id=20085 trace_id=2 func=__ip_session_run_tuple line=3560 msg="DNAT 209.227.211.X:8->10.127.54.101:5" id=20085 trace_id=2 func=__vf_ip_route_input_rcu line=1999 msg="find a route: flag=00000000 gw-0.0.0.0 via VLAN-54" id=20085 trace_id=2 func=fw_forward_handler line=726 msg="Denied by forward policy check (policy 0)" id=20085 trace_id=3 func=print_pkt_detail line=5955 msg="vd-h-services:0 received a packet(proto=1, 10.127.22.101:5->209.227.211.X:2048) tun_id=0.0.0.0 from VLAN-22. type=8, code=0, id=5, seq=87."

It seems that Fortinet passes traffic through the VLAN and not through the SD-WAN zone.

In view of upcoming activities, it is inconvenient for me to make N policies for all possible connection combinations between VLANs. And with each addition of VLAN add all N possible combinations.

I would like outgoing traffic from VLAN 22 (which will have to go to VLAN 54) for example to exit and re-enter from the SD-WAN interface and not from the VLAN interface

I hope I have explained myself

Thanks
Regards

AEK
SuperUser
SuperUser
May 13, 2024

Hello

I see only firewall policy allowing from WAN to the VIP and from the server to WAN. Did you add a firewall policy to allow the traffic from VLAN 11 to the VIP?

AEK
bettioool
bettiooolAuthor
New Member
May 13, 2024

Hi @AEK ,
no I did not, as it would be inconvenient with the increasing number of VLANs to make the N rules to allow all other VLANs.

Is there any way to make it work without doing these N rules?


Thanks


Regards

ozkanaltas
Valued Contributor III
May 13, 2024

Hello @bettioool ,


In normal time you need to create rule for every communication. But if can enable multiple interface policies on feature select menu. You can select multiple interface on one rule. You can solve your problem with one rule. 

AEK
SuperUser
SuperUser
May 14, 2024
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
