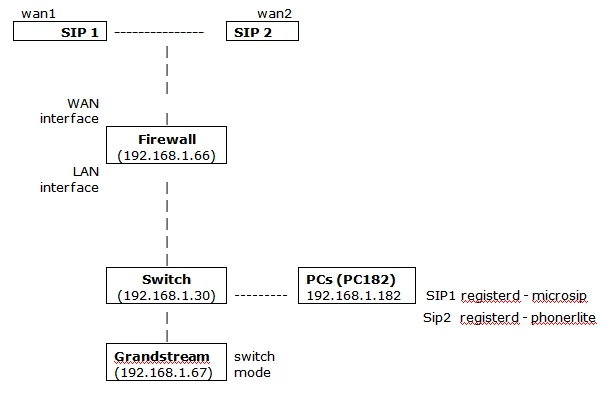
Connecting Two SIP Trunks with Different VoIP Providers in Grandstream UCM Using FortiGate Firewall
Hello everyone,
I’m encountering an issue while attempting to connect two SIP trunks with different VoIP providers in my Grandstream UCM 6301 using FortiGate firewall 80F. I’ve configured the SIP trunks individually, and each works fine when connected individually to the WAN port of Firewall too ( Added a Policy route to forward all traffic on this WAN port to LAN port ) . However, I was not able to make calling work when connecting both SIP trunks simultaneously.
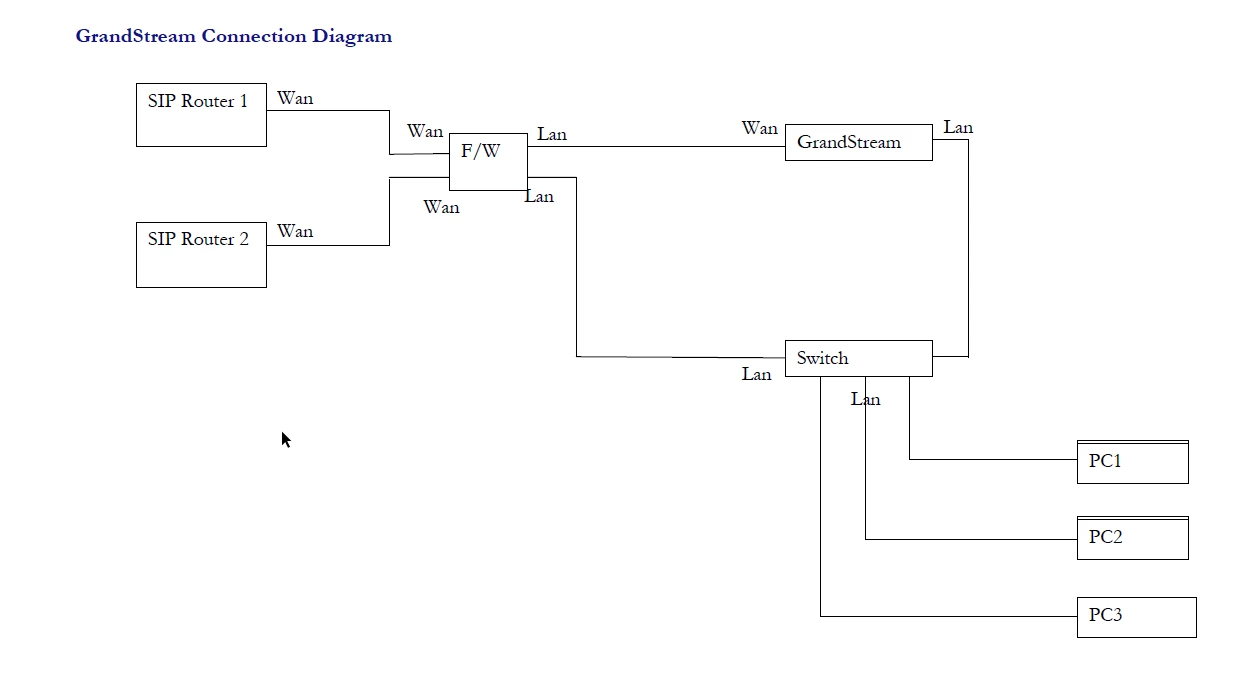
I have attached the Connection diagram of Firewall and Grandstream for 2 SIP case.
Here’s what I’ve tried so far:
On the Firewall , I have added a policy to allow both SIP inbound and outbound
I have enabled NAT on both Grandstream and Firewall
On the Grandstream device I have added a Static route to reach Firewall device.
I am not able to ping the SBC/Proxy IP provided by the SIP providers from the Grandstream device, unless I Add a Policy Route rule for WAN
I am not having ideas on how to configure the Firewall to allow SIP calls from 2 SIP’s connected to its WAN port. Any advice or guidance would be greatly appreciated.
Update :
"I have done some changes in the configuration as mentioned below. After the changes
I am able to place outbound calls but no voice / audio can be heard when I Connect the Grandstream device to the Fortigate Firewall in Switch mode.
If I remove the grandstream device then I can place calls and also hear audio / voice.
What changes do i Have to make to be able to solve the Audio Issue ?"
"Based on the recommendations from this post -
- https://community.fortinet.com/t5/Support-Forum/solved-How-to-configure-Fortigate-with-SIP-for-an-Asterisk/td-p/168273/page/2
- One-Way audio Issue Inbound call ucm6102 Freephoneline Trunk"
I have changed firewall configuration as below :
Configuartions :
Firewall Configuration
Network > Interfaces
Name : SIP1 (Wan1)
Type : Physical Interface
Role : WAM
Addressing mode : Manual
IP/Netmask : 100.X.X.X/255.255.255.248
Name : SI2P (wan2)
Type : Physical Interface
Role : WAM
Addressing mode : Manual
IP/Netmask : 10.X.X.X/255.255.252.0
Network > Static Routes
Destination : Subnet
100.0.0.0/255.0.0.0
Gateway Address : 100.64.86.179
Interface : SIP1 (WAN1)
Destination : Subnet
10.0.0.0/255.0.0.0
Gateway Address : 10.242.1.197
Interface : SIP1 (WAN2)
UTM > VoIP > Profile
Name : VoIP_Profile
SIP
Limit REGISTER request : 500
Limit INVITE request : 500
Enable Logging : yes
Enable Logging of Violations : No
SCCP
Limit Call Setup : 0
Enable Logging : yes
Virtual IP Configuration
Firewall > VIP
Name : SIP1 UDP
External interface : SIP1 (wan1)
Type : static NAT
External IP address : 0.0.0.0
Mapped IP addres : 192.168.1.67 (This is your Asterisk NATed private IP address)
Port fowarding : external service port UDP 5060 map to internal port UDP 5060
Protocol : UDP
Port Mapping Type : Many to Many
External service port : 5000 - 30000
Map to IPv4 port : : 5000 - 30000
Name : SIP2 UDP
External interface : SIP2 (wan2)
Type : static NAT
External IP address : 0.0.0.0
Mapped IP addres : 192.168.1.67 (This is your Asterisk NATed private IP address)
Port fowarding : external service port UDP 5060 map to internal port UDP 5060
Protocol : UDP
Port Mapping Type : Many to Many
External service port : 5000 - 30000
Map to IPv4 port : : 5000 - 30000
Name : SIP1 TCP
External interface : JIO_SIP (internal6)
Type : static NAT
External IP address : 0.0.0.0
Mapped IP addres : 192.168.1.67 (This is your Asterisk NATed private IP address)
Port fowarding : external service port UDP 5060 map to internal port UDP 5060
Protocol : TCP
Port Mapping Type : Many to Many
External service port : 5000 - 30000
Map to IPv4 port : : 5000 - 30000
Name : SIP2 TCP
External interface : SIP2 (wan2)
Type : static NAT
External IP address : 0.0.0.0
Mapped IP addres : 192.168.1.67 (This is your Asterisk NATed private IP address)
Port fowarding : external service port UDP 5060 map to internal port UDP 5060
Protocol : TCP
Port Mapping Type : Many to Many
External service port : 5000 - 30000
Map to IPv4 port : : 5000 - 30000
Firewall Policy objects Configuration
Firewall > inbound Policy
Name : SIP1 inbound Policy
Incoming interface : SIP1 (wan1)
Outgoing interface : internal
Source address : All
Destination address : SIP1 TCP ; SIP1 UDP
Schedule : always
Service : All
Action : Accept
Inspection Mode : Flow based
NAT : Disabled
UTM / Security Profiles : enabled
VoIP : enabled ; List = VoIP_Profile
SSL Inspection : certificate-inspection
Name : SIP1 outbound Policy
Incoming interface : internal
Outgoing interface : SIP1 (wan1)
Source address : All
Destination address : All
Schedule : always
Service : ALL_ICMP ; ALL_ICMP6 ; PING ; SIP
Action : Accept
Inspection Mode : Flow based
NAT : Enabled
UTM / Security Profiles : enabled
VoIP : enabled ; List = VoIP_Profile
SSL Inspection : certificate-inspection
Name : SIP2 inbound Policy
Incoming interface : SIP2 (wan2)
Outgoing interface : internal
Source address : All
Destination address : Airtel SIP TCP ; Airtel SIP UDP
Schedule : always
Service : All
Action : Accept
Inspection Mode : Flow based
NAT : Disabled
UTM / Security Profiles : enabled
VoIP : enabled ; List = VoIP_Profile
SSL Inspection : certificate-inspection
Name : SIP2 outbound Policy
Incoming interface : internal
Outgoing interface : SIP2 (wan2)
Source address : All
Destination address : All
Schedule : always
Service : ALL_ICMP ; ALL_ICMP6 ; PING ; SIP
Action : Accept
Inspection Mode : Flow based
NAT : Enabled
UTM / Security Profiles : enabled
VoIP : enabled ; List = VoIP_Profile
SSL Inspection : certificate-inspection
Grandstream Configuration
SIP Trunk Basic Setting:
Provider Name : SIP1 (peer mode)
Host Name: 100.X.X.X (provided by SIP)
Keep Original CID : unchecked
Keep trunk CID : unchecked
NAT: unchecked
Tel URI : Disabled
Need registration : checked
Allow outgoing calls if registration failure: unchecked
CallerID Name : Number provoided by SIP
From Domain : 100.X.X.X (provided by SIP)
From User : blank
Provider Name : SIP2 (Register Mode)
Host Name: ka.ims.airtel.in
Keep Original CID : unchecked
Keep trunk CID : unchecked
NAT: unchecked
Tel URI : Disabled
Need registration : checked
Allow outgoing calls if registration failure: unchecked
CallerID Name : Number provoided by SIP
From Domain : Domain name provided by SIP
From User : Number provoided by SIP
Auth ID : Number provoided by SIP
Trunk reg number : Number provoided by SIP
PBX seetings > SIP settings > NAT
External Host : 192.168.1.66 (was supposed to use WAN External IP , but since I have 2 SIPs , I used IP of firewall)
USE IP address in SDP : Checked
Add Local Network Address : 192.168.0.0/22 (internal network address)