


Lyyiheang
Visitor III
August 30, 2024
Question

Cisco Switch not accept CoA from FortiNAC

  • August 30, 2024
  • 4 replies
  • 2837 views

Dear team,


I noticed that Cisco Switch are not accept Radius CoA/Disconnect Message from FortiNAC-F 7.4. I'm not sure if we need to have any customer RADIUS Attribute to pass to the Cisco Switch. I would like to share debug of pcap and Switch here.
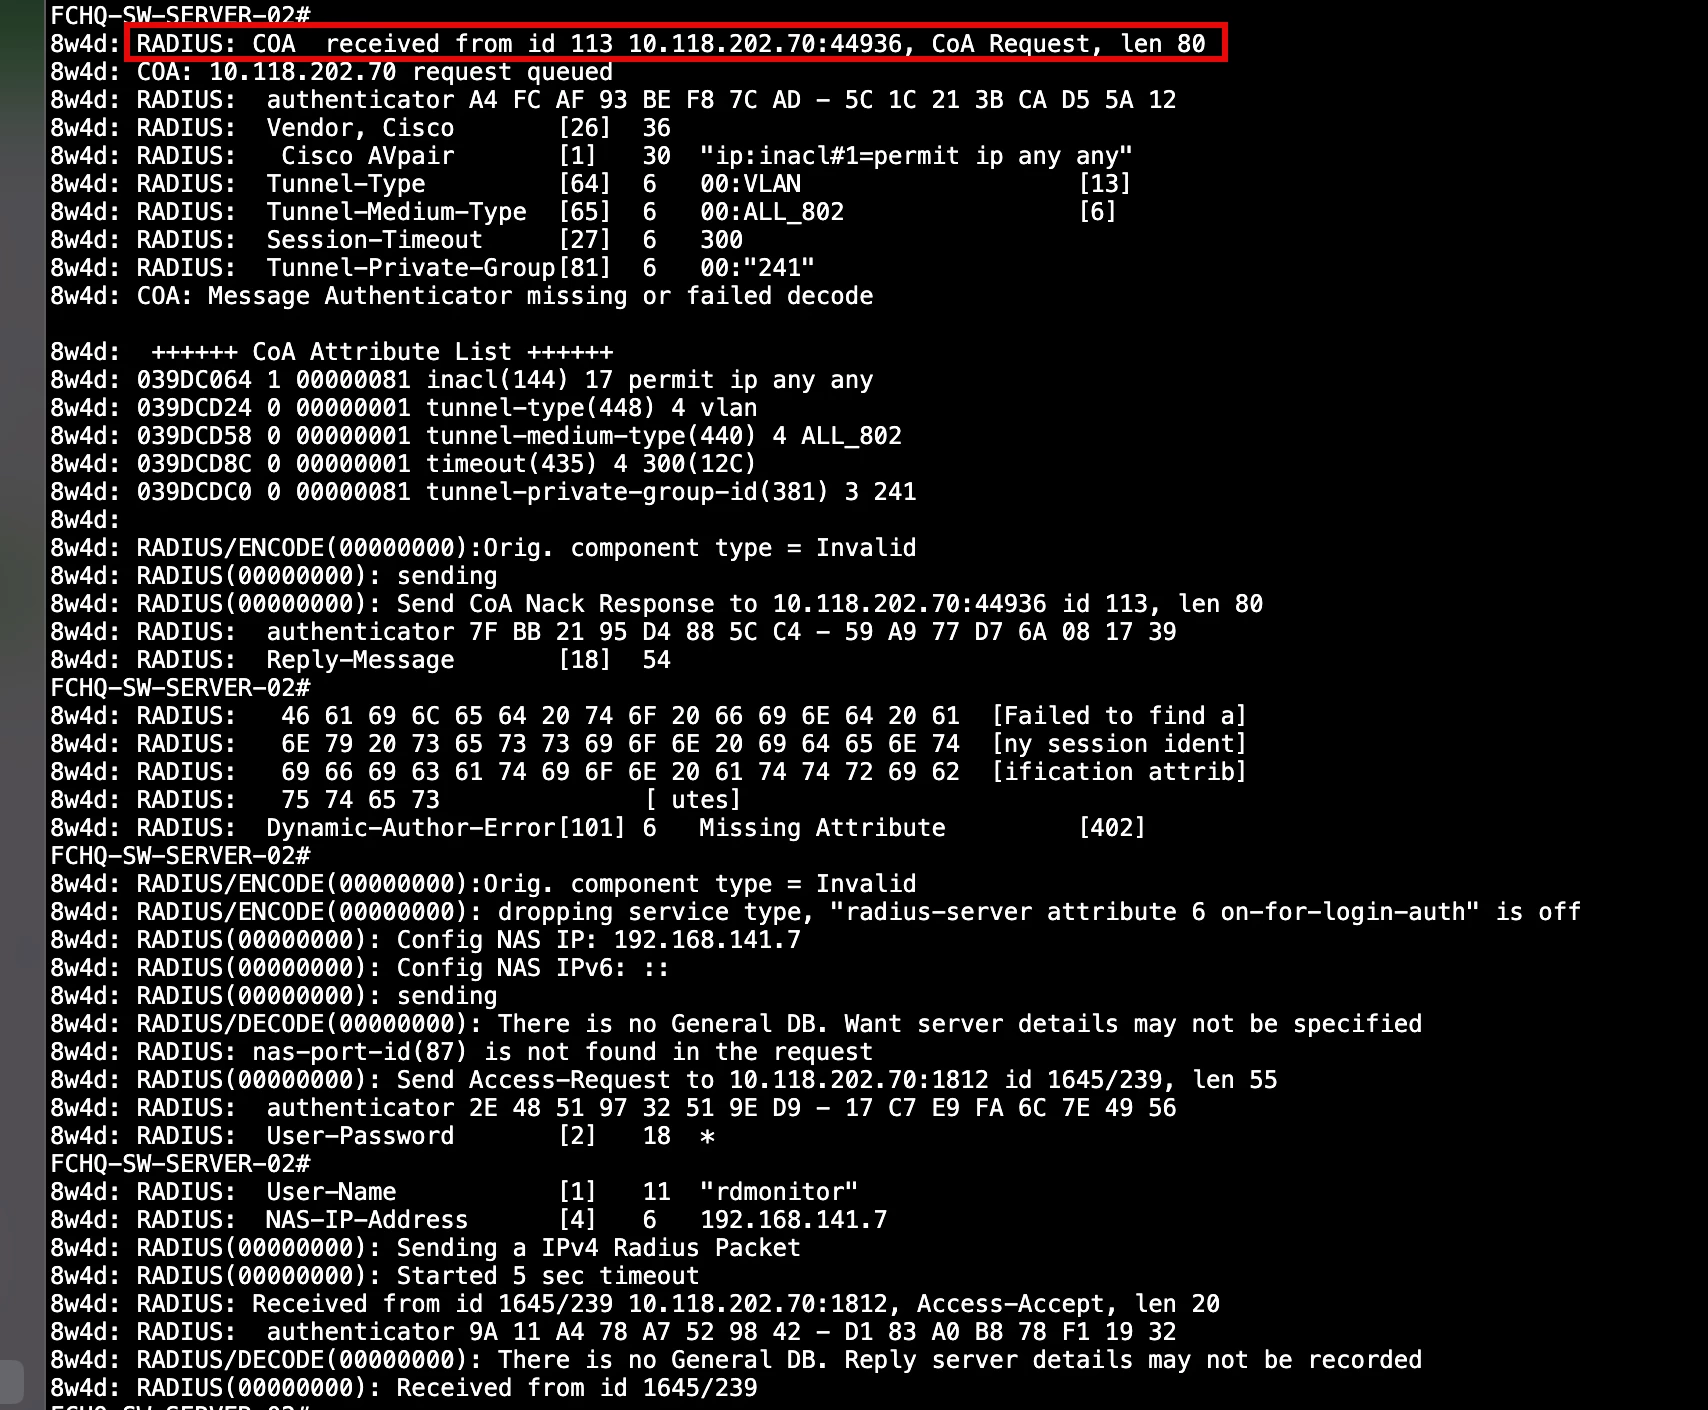
2024-08-30_21-03-23.png
Anyone who has experience this issue, Please kindly share


Note: RFC5176 Mode: system defined and Switch is configured CoA Port 3799


Thank You

4 replies

Jean-Philippe_P
Staff & Editor
Staff & Editor
September 2, 2024

Hello Lyyiheang, 


Thank you for using the Community Forum. I will seek to get you an answer or help. We will reply to this thread with an update as soon as possible. 


Thanks, 

Jean-Philippe - Fortinet Community Team
Lyyiheang
LyyiheangAuthor
Visitor III
September 2, 2024

It is now working when i add command aaa nas port extended.


Thank Everyone for help

burtoyo2
New Member
September 2, 2024

Mac auth is not going to continue being viable much longer, if it could be said to be even viable at all now. All mobile devices sold within the last few years have the ability to use virtual mac addresses at the flip of a switch and I expect desktop operating systems will begin offering this as a standard feature as well. It's possible to do on basically any OS currently but not built in https://mobdro.bio/ .

Hatibi
Staff & Editor
Staff & Editor
September 2, 2024

Hello  @Lyyiheang,


checking the CoA NAK response it complains about the session identifier.

For this you can use either "User Name" or the "Calling-station-ID".


Additionally i see you are adding in the CoA message itself the Access list attributes. This is not correct. In the CoA message you need to add an action such as bouncing the port or re-authentication. Then you add the Access lists in the Radius response (Accept-Accept) once the host re-authenticates.


This article provides you with the example when FortiSwitch is acting as NAS:

https://community.fortinet.com/t5/FortiNAC-F/Technical-Tip-CoA-Support-in-FortiNAC-7-4-and-applying-DACLs-in/ta-p/322638


For FortiSwitch we use the Fortinet proprietary arrtibute 

Fortinet-Host-Port-AVPair

action=reauth-port


In your case of Cisco you can try any the following:

https://www.cisco.com/c/en/us/td/docs/ios-xml/ios/sec_usr_aaa/configuration/15-s/sec-usr-aaa-15-s-book/sec-rad-coa.html

Table 3 CoA Request Commands Supported on the Device

Command

Cisco VSA

Bounce host port

Cisco:Avpair=“subscriber:command=bounce-host-port”

Disable host port

Cisco:Avpair=“subscriber:command=disable-host-port”

Reauthenticate host

Cisco:Avpair=“subscriber:command=reauthenticate”

Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
