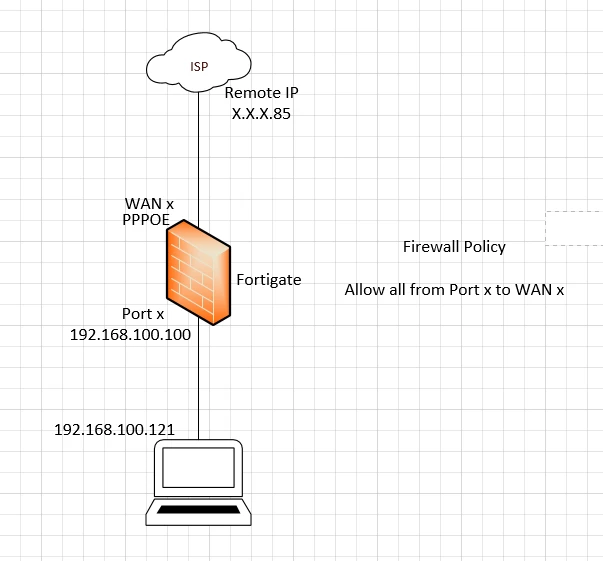
@Codedx Try to initiate a ping from WANx interface
# exe ping-options interface wanx
# exe ping 8.8.8.8
If that doesn't work it means that connection with ISP is not properly configured. If that works, it means that Firewall Policy or NAT is not properly configured in FortiGate.
1) Try to ping the gateway first from the Wan interface.
#execute ping-options source <wanx IP>
#execute ping <gateway IP>
If it doesn't work then there is a problem in the PPPOE config. But if it works then try to initiate the ping from 192.168.100.121 to 8.8.8.8 and run the sniffer on the fortigate to check if the traffic is leaving the fortigate or not.
#di sniffer packet any "host 8.8.8.8 and icmp" 4 0 l
the above command will show you the output if it shows you just the IN packets that means you might be missing a policy or static route then you further have to run the debugs in order to check the root cause.