Eugene_Alaska
New Member
July 24, 2023
Question

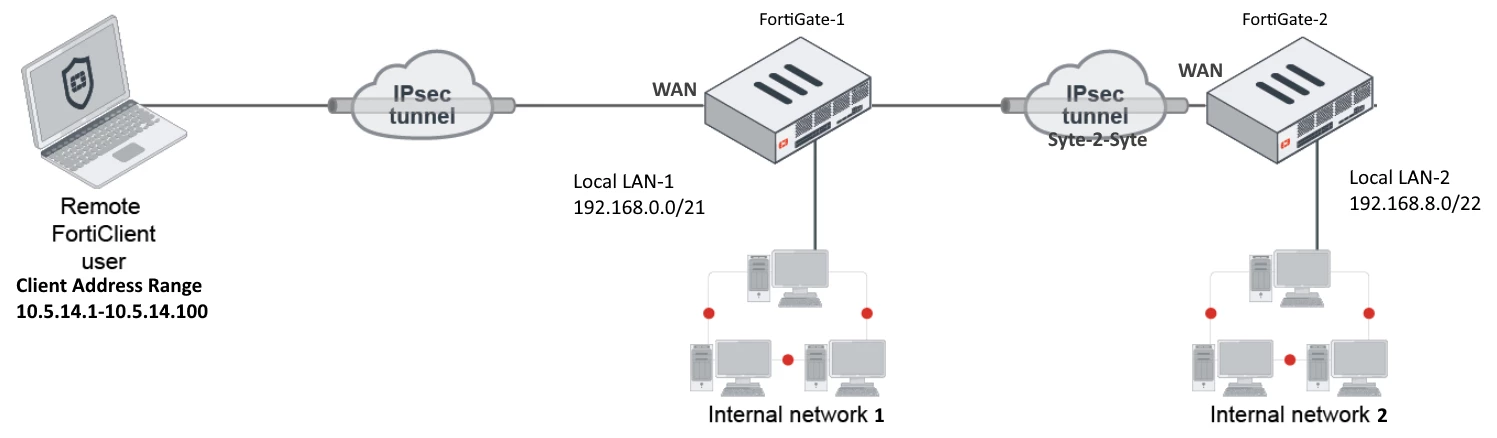
Can remote FortiClient user get access to local lan connected over syte-2-syte tunnel?

  • July 24, 2023
  • 4 replies
  • 2250 views

Hello.

1234.png

See picture, please. 
Users from LAN-1 access LAN-2 without any problem over syte-2-syte ipsec tunnel.

Also Users from LAN-2 access LAN-1 over syte-2-syte ipsec tunnel.

Question.
Can the remote FortiClient user access internal network 2?
If so, how?

Now access only to network 1.


Thanks.


P.S.

Fortigate1 is FortiGate-61E model.
Fortigate2 is FortiGate-61E model also.

4 replies

kjohri
Staff
Staff
July 24, 2023

Hello,

Yes, SSL VPN users will be able to access the resources across Site to Site tunnel. Please refer to the below article-
https://docs.fortinet.com/document/fortigate/7.2.5/administration-guide/45836

Eugene_Alaska
New Member
July 24, 2023

@kjohri wrote:

Hello,
Yes, SSL VPN users will be able to access the resources across Site to Site tunnel.

But remote users use ipsec vpn to connect.
Or does it not matter?


nithincs
Staff & Editor
Staff & Editor
July 24, 2023

yes, you could achieve it. Make sure to add dailup tunnel subnet in phase2 selector of the site-site tunnel.

in FGT1 source :10.5.41.0/24 dest :192.168.8.0/24
in FGT2 source 192.168.8.0 dest :10.5.41.0/24

In FGT2, add a routeto 10.5.41.0 via tunnel interface.

Make sure to have the policies in place at both the firewall.

With this it should work

Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!