config router prefix-list edit "Blocked Default Route" set comments "Bloquea aprendizaje de rutas por BGP de la MPLS" config rule edit 1 set prefix 192.168.0.0 255.255.0.0 next end
Then a Route Map:
config router route-map edit "ROUTE_MAP_DEFAULT" config rule edit 1 set action deny set match-ip-address "Blocked Default Route" next end
And last, apply Route Map in your neighbour:
config router bgp set as 64XXX config neighbor edit "XXX.XXX.XXX.XXX" set remote-as 64XXX set route-map-in "ROUTE_MAP_DEFAULT" end
Maybe exist a better solution, but this one worked for me when i dont want to learn some routes.
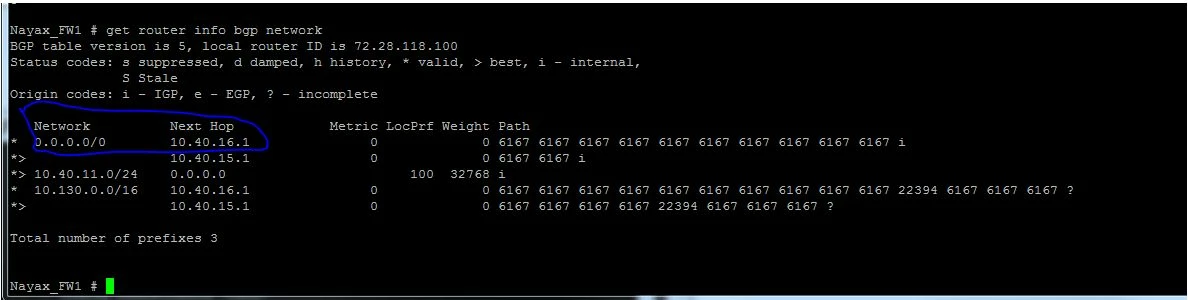
This was an ACCESS-LIST but there's a small "twist" sort of speak which is not mentioned in the Forti documents as usual.
config router access-list edit "Block_Def_Route" config rule edit 1 set action deny set exact-match enable next edit 2 set exact-match disable next end next end
config neighbor edit "10.40.15.1" set distribute-list-in "Block_Def_Route" set remote-as 6167 set route-map-out "Verizon_Prepend1" next edit "10.40.16.1" set distribute-list-in "Block_Def_Route" set remote-as 6167 set route-map-out "Verizon_Prepend" next end
Without adding the bolded text this would have never worked.
what it means is to allow everything else BUT what is being actioned as "denied"