

jlb_
Explorer II
May 8, 2024
Question

Block FortiSASE Access on corporate connection.

  • May 8, 2024
  • 1 reply
  • 1109 views

Hi,


We want to block the connection of FortiClient on FortiSASE by blocking it on our corporate firewalls. 

We already use the IP addresses of provisioned Security POPs on the FortiSASE instance, but still did not work. So we try to use Wireshark to check the connection and got the IP address of 154.52.16.101. We check the equivalent IPs and got the IP ranges, just to make sure, we want to ask if is there an equivalent IPs to this and if it has specific hostname on this IPs. 
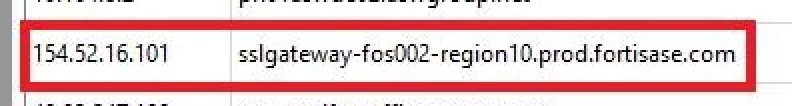
 

Screenshot 2024-05-08 at 11.12.08 AM.png


Thank you.


1 reply

smaruvala
Staff
Staff
May 8, 2024

Hi,


- Are you using a dedicated public IP for your FortiSASE instance? 

- We can usually block the communication using threat feed. 
https://docs.fortinet.com/document/fortisase/latest/administration-guide/751044/appendix-a-fortisase-data-centers
- However I don't see the mentioned IP in the threat feed. 

- Another way is to configure the profile in the SASE portal using "Bypass SASE" option. If your public IP of the clients behind the firewall is a specific one then it can be bypassed to connect to SASE.

https://docs.fortinet.com/document/fortisase/latest/administration-guide/921669/connection


Regards,

Shiva

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

