

Question
BGP peering betwenn Fortigate and Azure Virtual WAN (vWAN)
Hello
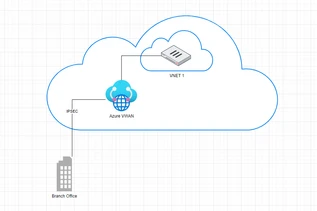
We have a Fortigate on a VNET on Azure and we need to exchange routes with an Azure Virtual WAN (VWAN). I'd like to know if is it possible and if it's done just by configuring the BGP on both sides or we need to configure an IPSec tunnel between them.
Is there anyone here on community that deployed it?
Thanks in advanced.

