

ByteHaven
Explorer III
May 5, 2026
Solved

Auto-registration of new devices

  • May 5, 2026
  • 6 replies
  • 144 views

Hello everyone,


From what I understand, the recommended method to register company assets is to integrate LDAP and enable the option where endpoints with the Persistent Agent get automatically registered once users authenticate with their AD credentials.
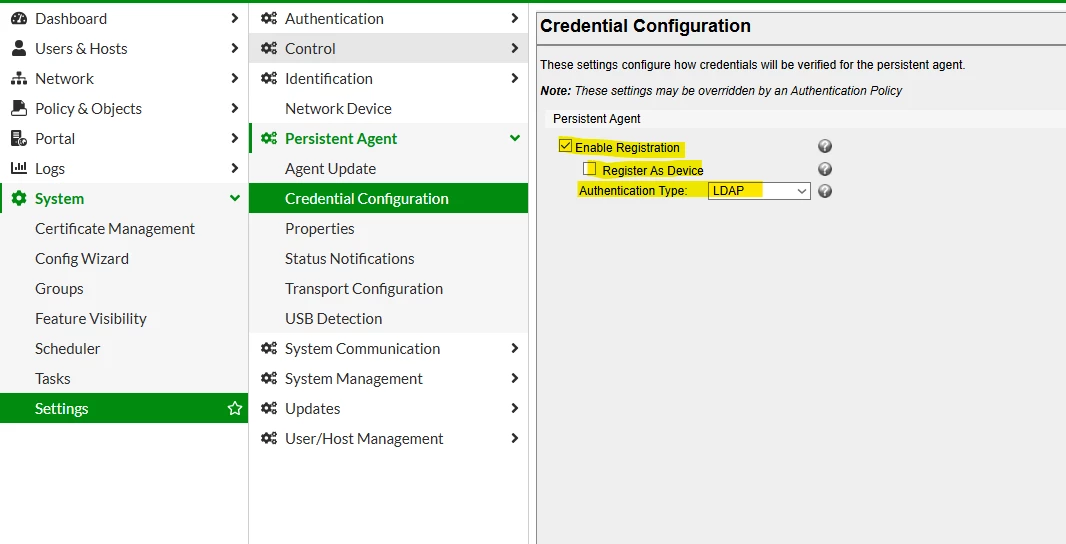
So basically, if a user has the agent installed on their laptop and logs in using AD, the device gets automatically registered, please correct me if I’m wrong here.

However, I came across information suggesting this method should mainly be used during the initial onboarding phase and be disabled after.


My question is:
How are new company users/devices automatically registered after that initial onboarding?
Is there a best practice to handle ongoing automatic registration for new assets?


Thanks in advance.

BR,

Best answer by ebilcari

For the host to be automatically registered, the endpoint must be joined to the domain, and the currently logged‑in user that is identified by the Agent, must be found in the directory configured in FNAC. This configuration can be kept permanently enabled, there is no need to disable it afterward. Having a registered host on the network does not necessarily mean it will be automatically placed in production. Network Access Policies can be used to further control VLAN assignment based on additional conditions.

There are different methods to register hosts in FNAC, but using the Agent is always recommended, as it provides the best visibility. You can refer to this guide: https://docs.fortinet.com/document/fortinac-f/7.6.0/corporate-user-device/66397/configure-fortinac-to-automatically-register-the-endpoint-device

or the registration through Passive Agent (SSO): 


6 replies

AEK
SuperUser
SuperUser
May 5, 2026

Hi BH

In my opinion this auto register of PA clients should be enabled in the initial deployment so you auto-register the hundreds of your Corp clients, then “should” be disabled after, so the following registrations of PA clients will be manual by some NAC admin (e.g.: you can grant this right to domain admin or helpdesk, depending on your company policy).

This is to have control on the registration process, otherwise I guess someone unauthorized can register a new client without intervention of any NAC admin.

But is you still need auto-registration of PA clients and you are confident that no unauthorized registration will happen then just leave the feature enabled.

AEK
ByteHaven
ByteHavenAuthor
Explorer III
May 5, 2026

Okay noted, thank you for the explanation.


The next point you mentioned is that for new registration it should be done manually ? Like actually the admins should go to user & hosts > hosts > look for the device and “register as a device” ? 
Is there another way ? Or maybe I misunderstood.

AEK
SuperUser
SuperUser
May 5, 2026

Yes that’s what I mean, but register as host, right?

If I remember well there should also be another method to auto-register, it is by profile rule, but this one I never had the need to use it, because in medium companies where there is less than 2000 hosts/devices and few asset changes we usually don’t need for auto-registration.

AEK
ebilcari
Staff
ebilcariAnswer
Staff
May 6, 2026

For the host to be automatically registered, the endpoint must be joined to the domain, and the currently logged‑in user that is identified by the Agent, must be found in the directory configured in FNAC. This configuration can be kept permanently enabled, there is no need to disable it afterward. Having a registered host on the network does not necessarily mean it will be automatically placed in production. Network Access Policies can be used to further control VLAN assignment based on additional conditions.

There are different methods to register hosts in FNAC, but using the Agent is always recommended, as it provides the best visibility. You can refer to this guide: https://docs.fortinet.com/document/fortinac-f/7.6.0/corporate-user-device/66397/configure-fortinac-to-automatically-register-the-endpoint-device

or the registration through Passive Agent (SSO): 


Emirjon
ByteHaven
ByteHavenAuthor
Explorer III
May 6, 2026

Thank you for this explanation, Emirjon. I will have a look at the articles you sent and use them.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
