


Question
Assistance w/ VDOM implementation outline
Howdy Folks!
I am new to the Network Engineering side of things, as I was a Sales Engineer/Solution Architect for the last 15 years. That being said, I have a laymen's understanding of the FortiGates, but very little hands-on configuration experience.
I reviewed the VDOM overview (https://docs.fortinet.com/document/fortigate/7.6.1/administration-guide/), and think I have a general understanding of what needs to be done, but need to understand the "why", order of operation, and dependencies so I can put all the different piece of the puzzle together.
The above document doesnt go into VDOM and VLANs, so there is a big area of question.
I have been tasked to create an outline as to how to implement VDOMs in the following scenarios...
Scenario#1 - Single WAN connection being broken out into (2) separate VLANs that require a separate VDOM for Management/control. Thought is to use VDOM1/Root to for the WAN-side FW instance and VDOMs 2&3 for the LAN-side VLAN specific FW instances. Is what I described possible. Do I have to create policy routes to map the VDOM1 WAN connection(s) to the VLAN-specific VDOMs? If so, how.
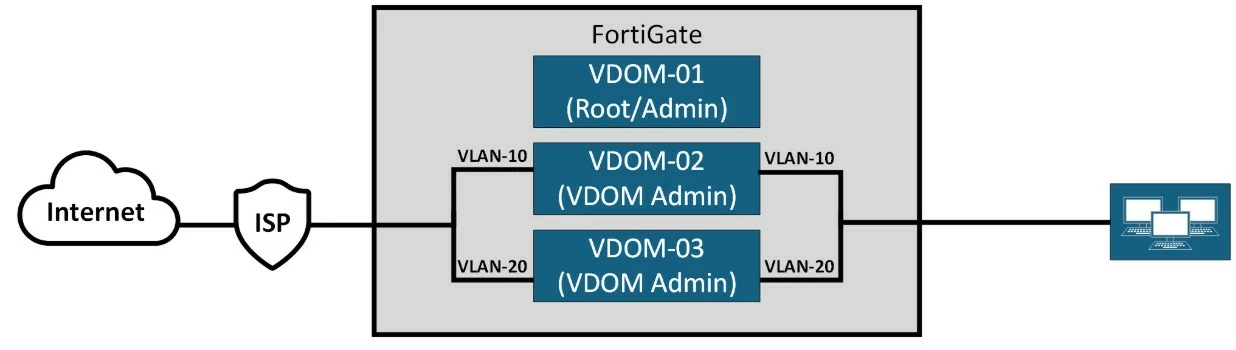 Scenario#1
Scenario#2 - create a design with a primary and secondary WAN provider terminating into a single VDOM (VDOM1) and then feeding separate child VDOMs to allow each program to control/manage their specific child/VLAN VDOM instance. How do you create a WAN connection priority (WAN1 (primary) and WAN2 (Failover) on a single VDOM. What sort of routing policies do you have to create so that VDOM1/Root feeds the VLAN10 into VDOM2 and VLAN20 into VDOM3?
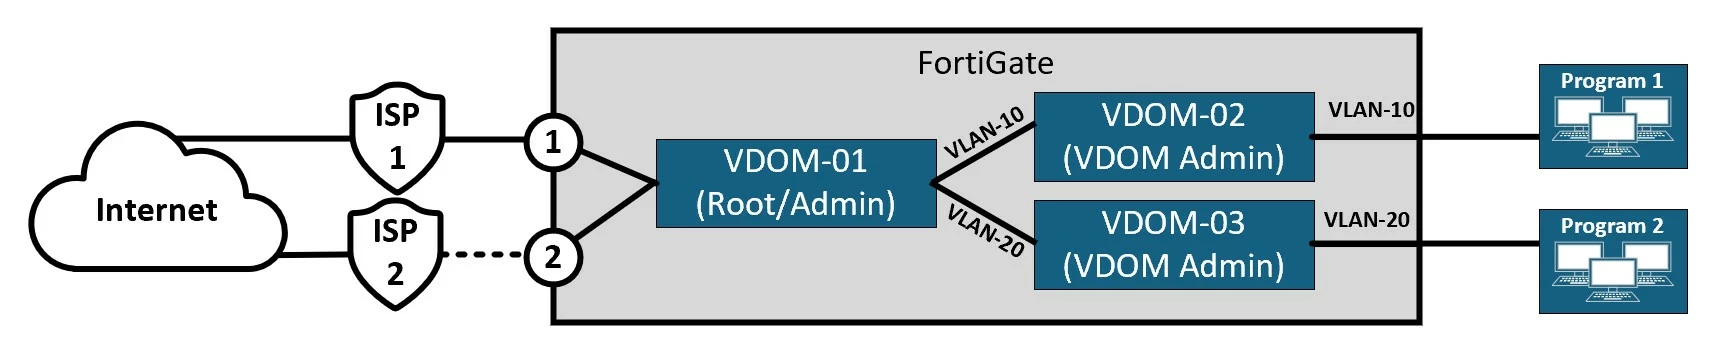 Scenario#2
Thanks all for the review and assistance!
Gwillikers

