Question
App ctrl - Block applications detected on non-default ports
Hi,
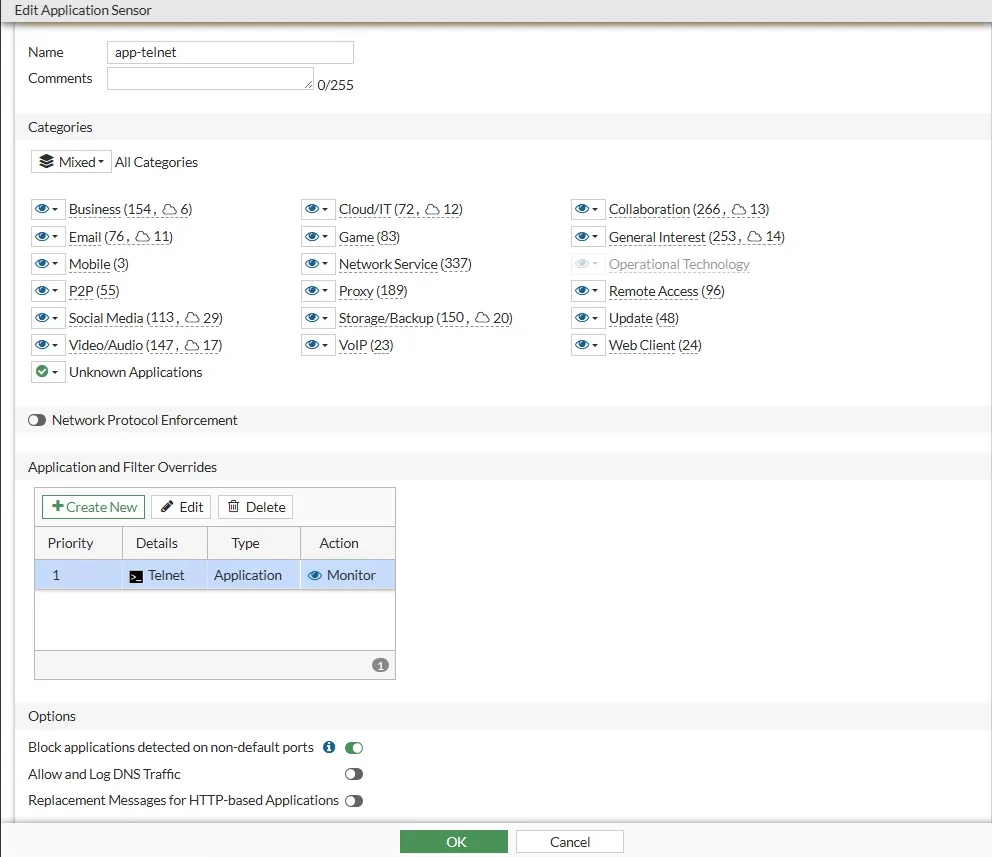
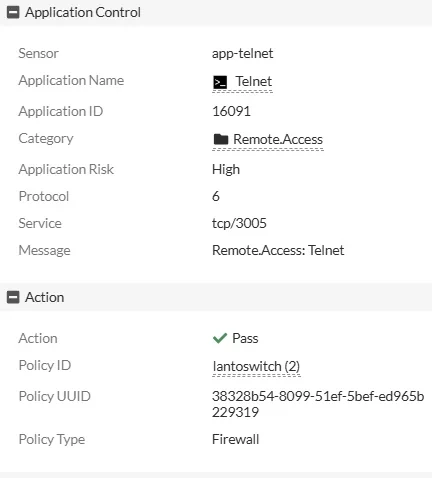
I have configured an Application Control profile and applied on a firewall policy. The application control profile have "block applications detected on non-default ports" enabled. However, when I run Telnet on other ports than 23 the traffic is allowed and it's also detected as application Telnet according to the logs on FortiGate.
I have verified that the traffic is hitting the correct firewall policy.
I am running FortiOS 7.4.5.
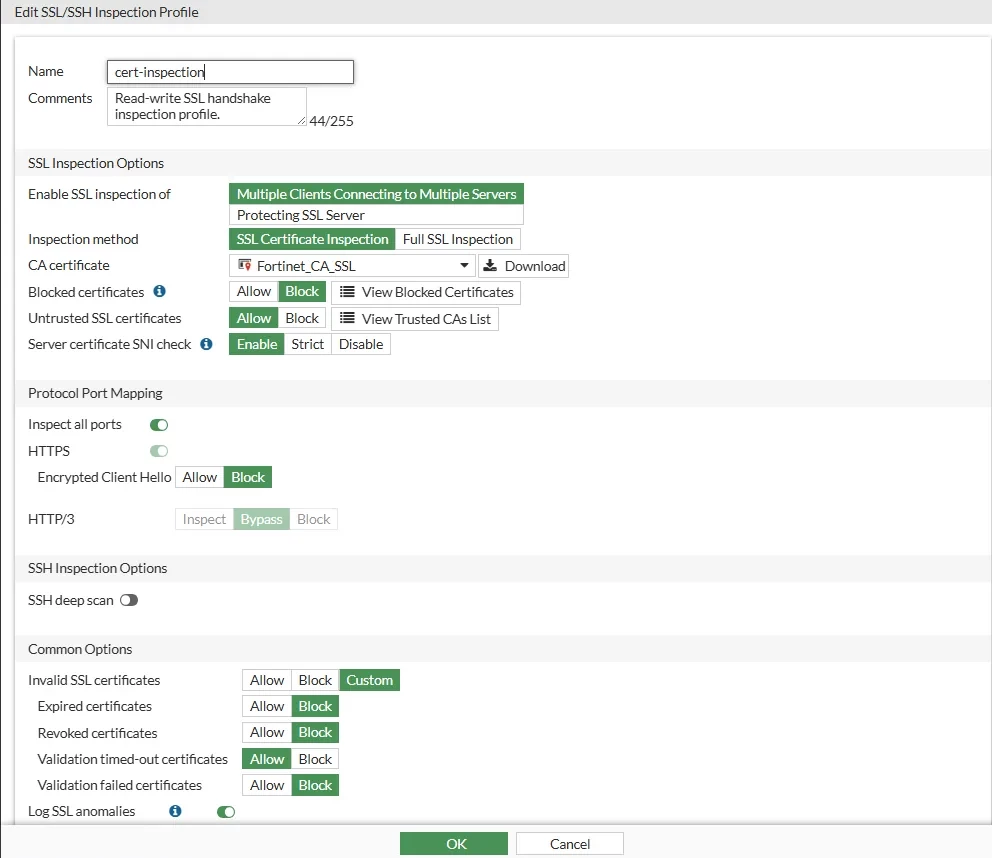
Please see my configuration on attached pictures.
What am I doing wrong? Shouldn't this traffic be blocked?