

damianhlozano
Explorer II
September 24, 2024
Solved

Access to Fortigates, to mgmt IP addresses, from another VLAN

  • September 24, 2024
  • 19 replies
  • 6825 views

Hello team!!!


We have 2 FGT100F in HA and configured interfaces called "mgmt" as "in band"

Now we need to access from a computer in any other interface and get:
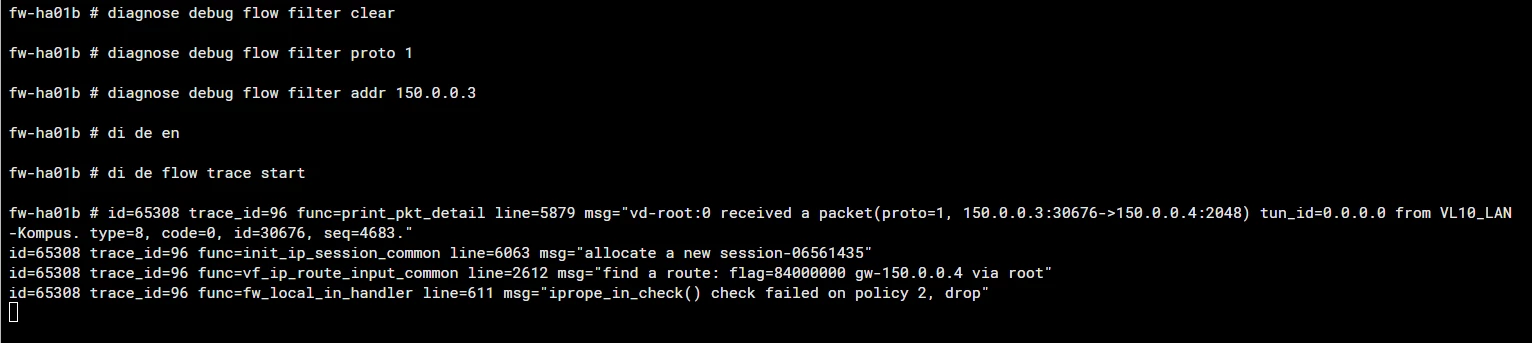
Debug.png

150.0.0.4 is the IP of Fortigate HA in a specific VLAN and 150.0.0.3 is another device in the same VLAN.

I know this is a public IP, but this is complicated to change the IP in all the devices in this VLAN.

From 150.0.0.3 I can ping 150.0.0.4, but not the HA IP on mgmt interface

From another device in mgmt interface, I can ping the HA IP on mgmt interface, and each Fortigate as well

Previously, we had disabled src-check in mgmt interface

I tried to add a local-in policy to allow this (config firewall local-in-policy), but still the same behavior

We need to access to Fortigate from any VLAN, using the IP on the mgmt interface.  Is this possible?


Thanks in advance.

Regards,

Damián

Best answer by Toshi_Esumi

If you're using 150.0.0.4 to access the FGT, yes, you don't need the policy. That gives you access only to the primary. But if you use 192.168.29.8 while you're coming from VL10_LAN-Kompus interface, you need a policy. You can test this by just pining it. You shouldn't be able to ping the mgmt IP from VL10_LAN-Kompus without the policy.

Toshi

19 replies

johnathan
Staff
Staff
September 24, 2024

'iprope_in_check() check failed on policy 2' indicates a local-in policy is actually blocking this traffic. Are you able to post what you had configured?

Never trust a computer you can't throw out a window.
damianhlozano
Explorer II
September 24, 2024

Hello Johnathan, thanks for your response.


Yes, these are my current local-in policies:

--------------------------------------------

config firewall local-in-policy
   edit 1
      set uuid 81d13aa0-7a98-51ef-5343-05b37f0d0f86
      set intf "VL10_LAN-Kompus" "mgmt"
      set srcaddr "all"
      set dstaddr "all"
      set action accept
      set service "ALL"
      set schedule "always"
   next
   edit 4
      set uuid 1fa07e74-7064-51ef-75cb-bb5d6eb89bf2
      set intf "port7" "port8" "port9" "port10" "port11"
      set srcaddr "IPs_Argentina"
      set srcaddr-negate enable
      set dstaddr "all"
      set service "ALL"
      set schedule "always"
   next
end

--------------------------------------------


The rule ID 1 is which I just created, trying to allow ping from VL10_LAN-Kompus to IPs in "mgmt" ports

The rule ID 4 is a rule that I had created to allow connections to Fortigate, only from IPs from my country (Argentina).  port7, port8, port9, port10 and port11, are WAN ports


Regards,

Damián

damianhlozano
Explorer II
September 25, 2024

Any idea?


Thanks, regards!

damianhlozano
Explorer II
September 27, 2024

Sorry, another question related to this.

Now, after add the IPv4 policy to allow access from VLAN10 to mgmt.

From VLAN10:

I can ping the cluster IP in the mgmt interface (192.168.29.5)

I can ping the active FGT management-ip in the mgmt interface (192.168.29.8)

I cannot ping the pasive FGT management-ip in the mgmt interface (192.168.29.9)


I did a debug in passive FGT and nothing was showed

I did a debug in active FGT and I get this:


id=65308 trace_id=101 func=print_pkt_detail line=5879 msg="vd-root:0 received a packet(proto=1, 150.0.0.241:1->192.168.29.9:2048) tun_id=0.0.0.0 from VL10_LAN-Kompus. type=8, code=0, id=1, seq=791."
id=65308 trace_id=101 func=init_ip_session_common line=6063 msg="allocate a new session-0728f54f"
id=65308 trace_id=101 func=vf_ip_route_input_common line=2612 msg="find a route: flag=04000000 gw-192.168.29.9 via mgmt"
id=65308 trace_id=101 func=__iprope_tree_check line=528 msg="gnum-100004, use int hash, slot=78, len=3"
id=65308 trace_id=101 func=get_new_addr line=1265 msg="find SNAT: IP-192.168.29.5(from IPPOOL), port-60418"
id=65308 trace_id=101 func=fw_forward_handler line=987 msg="Allowed by Policy-24: SNAT"
id=65308 trace_id=101 func=__ip_session_run_tuple line=3429 msg="SNAT 150.0.0.241->192.168.29.5:60418"


From another computer in the same segment of mgmt interface, I can ping all this 3 IPs.


Any idea?

Thanks in advance.

Regards,

Damián


Toshi_Esumi
SuperUser
SuperUser
September 28, 2024

I'm now not so sure if accessing the "management-ip" on the secondary from a VLAN interface would work.
As in the "management-ip" KB I referrd above, it seems to be designed to be accessible from outside coming directly to the physical interface (of course both sides are on the same broadcast domain via a switch) as depicted in the diagram. So if you access the secodary's management-ip, it never hits or comes through the primary. That's why it works.


On the other hand, if you're coming from another interface configured on both units, your access to the secondary's management-ip always arrives at the primary on the VLAN interface. But based on my simple test: pinging from the primary to the secondary's management-ip doesn't get any reply. While pinging from the secondary to the primary's management-ip gets replies. So unless my test setup is erroneous, if it's coming from another interface arriving at the primary it wouldn't work.

However, I'm still not 100% sure about the design so I could be wrong as well as my test environment. You likely need to open a ticket at TAC to get it tested by TAC person in a remote session.

Toshi

damianhlozano
Explorer II
September 28, 2024

Ok, anyway, thanks for everything.

Regards,

Damián

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!
