

100e to sonicwall
FortiGate 100E firmware 5.6.6
I am new to Fortigates and am trying to establish an IPSEC tunnel to a sonicwall. I have come across some tutorials on attempting this but they show for older firmware versions and things look different and the menus are not the same. I did try to also use the CLI and i have absolutely no luck with that either.
As far as I have been able to see I have configured the various settings on both ends to be the same but they are not connecting. Looking at the vpn tunnel in both the Sonicwall and Fortigate, it shows it as being up but when I get to the logs, for the fortigate it is showing as being down.
Within the logs for the Fortigate, and also in the CLI debug info I pasted below, it is showing as wanting to use IKEv2 when I have IKEv1 configured.
Some things I have tried is selecting various proposals, DPD on/off, standing on my head, sacrificing a coworker, the expected things, even reading the manual for the different versions of 5.6.5, .6, and also 6.0.2, which are also firmware I tried. Moved it back to 5.6 but I am stumped as to what I am missing, any help would be appreciated.
Screenshot of where it says IKEv2 in GUI log:
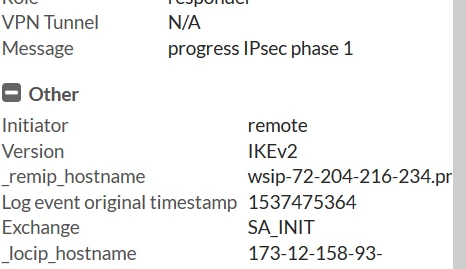
Doing a debug from the FortiGate I am getting:
ike Negotiate SA Error: ike ike [9748]
ike 0: comes <xxx.xxx.xxx.xxx>:500-><yyy.yyy.yyy.yyy>:500,ifindex=8....
ike 0: IKEv2 exchange=SA_INIT id=a3be868a6138d7cb/0000000000000000 len=380
ike 0: in A3BE868A6138D7CB000000000000000021202208000000000000017C220000300000002C010100040300000C0100000C800E0100030000080300000C03000008020000050000000804000005280000C800050000A5080E44701E201AB22D83191F468A40D16A33D5C35419B828787C8DF2EE1579193DAF76A0FDE55A3415DB2B1C3CC65D6FF07F03507D28506A01B2639AC66DDE466180848C499451356E7CCBB5394B1DF75D48320DC2C52CB03FB624716DC94B0A26126662C4B43D311E7E5EB32C7292E75E69256BB87EEE8C941805B28EB79A1A5CF85E1692267C7B5F314767ACC67EEA06DD87F1F251A77995B21B4DDCD975F3B7A5E2DE1071B9F2AA45653F4303FA7A34299FA8EA91E0146A689C3A7B9A3929000018BD871C2ED2C7CE66DB478D7F9B0A4665A1D151EC2900001C00004004E6A505A616AE249692DF8EC4833511D2131953DC2B00001C000040056309B88C1E537D73EBB7908E864D88B6714436F1000000182A6775D0AD2AA7887C33FE1D68BAF308966F0001
ike 0:a3be868a6138d7cb/0000000000000000:297: responder received SA_INIT msg
ike 0:a3be868a6138d7cb/0000000000000000:297: received notify type NAT_DETECTION_SOURCE_IP
ike 0:a3be868a6138d7cb/0000000000000000:297: received notify type NAT_DETECTION_DESTINATION_IP
ike 0:a3be868a6138d7cb/0000000000000000:297: incoming proposal:
ike 0:a3be868a6138d7cb/0000000000000000:297: proposal id = 1:
ike 0:a3be868a6138d7cb/0000000000000000:297: protocol = IKEv2:
ike 0:a3be868a6138d7cb/0000000000000000:297: encapsulation = IKEv2/none
ike 0:a3be868a6138d7cb/0000000000000000:297: type=ENCR, val=AES_CBC (key_len = 256)
ike 0:a3be868a6138d7cb/0000000000000000:297: type=INTEGR, val=AUTH_HMAC_SHA2_256_128
ike 0:a3be868a6138d7cb/0000000000000000:297: type=PRF, val=PRF_HMAC_SHA2_256
ike 0:a3be868a6138d7cb/0000000000000000:297: type=DH_GROUP, val=MODP1536.
ike 0:a3be868a6138d7cb/0000000000000000:297: no proposal chosen
ike Negotiate SA Error: ike ike [9748]


