Ahmed_Galal
Staff
Staff
December 31, 2024

Troubleshooting Tip: OCSP stapling is not working

  • December 31, 2024
  • 0 replies
  • 408 views

Description

This article describes how to troubleshoot OCSP Stapling in FortiWeb.

Scope

FortiWeb.

Solution

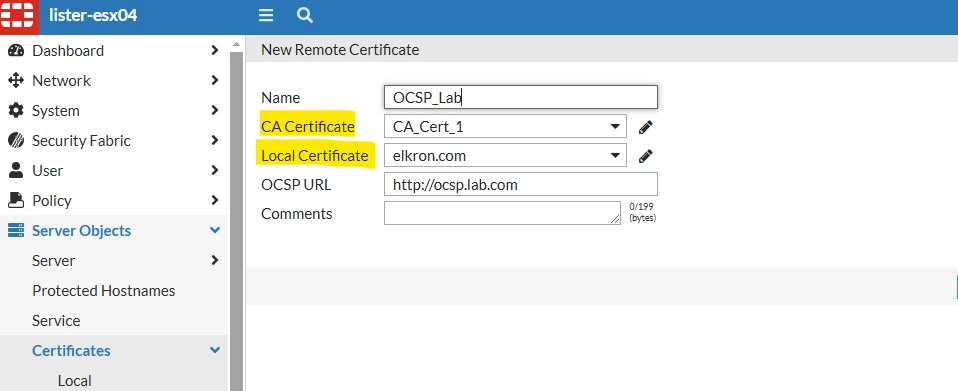
  1. Make sure to select the right local certificate and CA certificate of OCSP server/responder at Server Objects -> Certificates -> OCSP Stapling:

    Screenshot 2024-12-31 093356.png


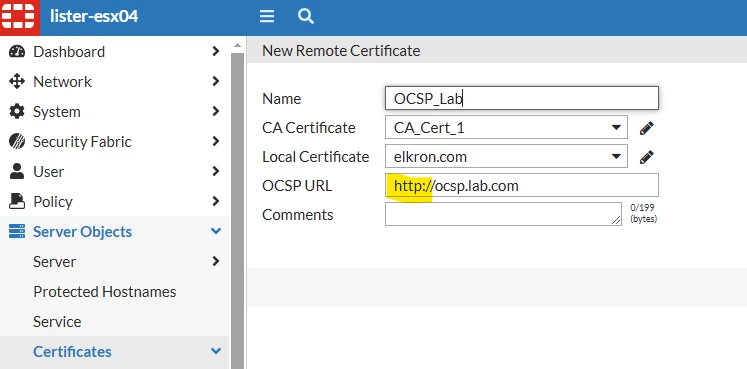
  2. The OCSP URL must contain either [http:// OR https://] at Server Objects -> Certificates -> OCSP Stapling:

    Screenshot 2024-12-31 093617.png


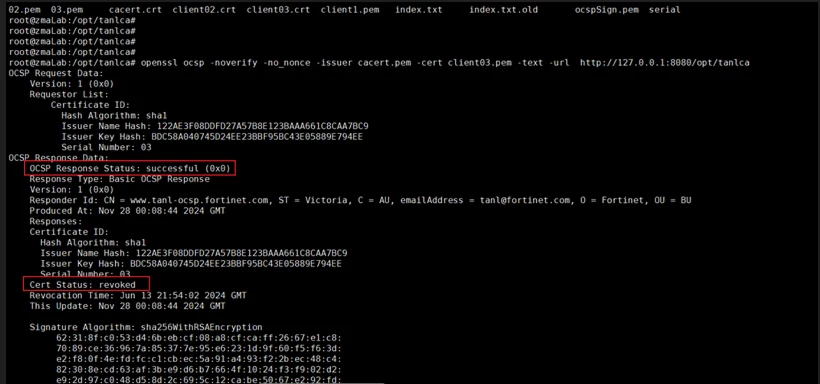
  1. Use the openssl command to verify if the OCSP server working properly:


openssl ocsp -noverify -no_nonce -issuer cacert.pem -cert client03.pem -text -url  http://127.0.0.1:8080/opt/tanlca

Picture1.png


Note 1: 

cacert.pem is the ocsp CA certificate.

Note 2:

client03.pem is the test certificate. to check if it has been revoked.

Note 3:

The above sample uses 3 parameters that match FortiWeb configuration, and FortiWeb actually uses this command on the backend to call openssl to verify/test OCSP stapling, then return the result to the frontend.


Related articles:

OCSP-Based certificate revocation check

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!