Troubleshooting Tip: FortiWeb blocks allowed file uploads with 'Illegal file type' errors
| Description | This article describes how to troubleshoot FortiWeb file upload blocks when a File Security Policy is configured to allow specific file types, but uploads are still denied with the error messages 'File name [N/A]: Illegal file type' or 'File name [blob]: Illegal file type'. |
| Scope | FortiWeb. |
| Solution | This scenario typically occurs when FortiWeb is correctly enforcing file security rules, but the application framework handling the upload does not expose the filename or file content in a predictable manner. For standard configuration steps to create File Security Rules and File Security Policies, refer to Technical Tip: Configuring File Security Policy to limit file uploads by file type/size and block viruses.
This article focuses only on troubleshooting the specific error conditions below.
Observed symptoms:
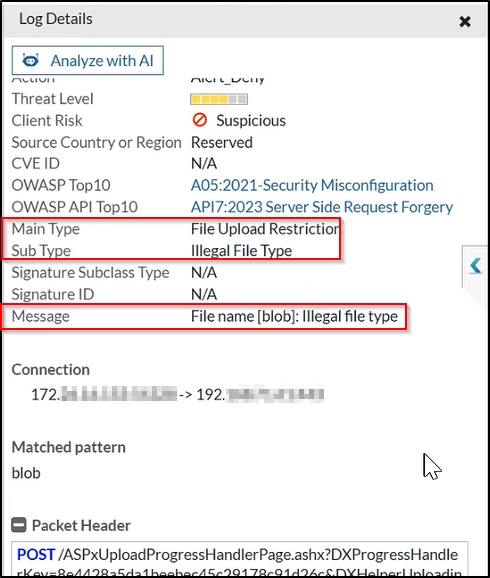
Attack logs show one or more of the following messages:
The uploads may involve legitimate file types such as PDF, JPG, or PNG.
Why this occurs:
File name [N/A]: Illegal file type
Recent FortiWeb versions enforce stricter handling of uploads with empty metadata. If a multipart upload contains:
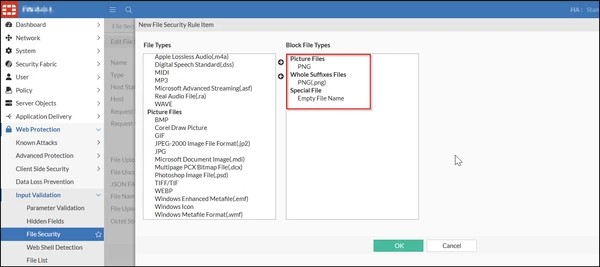
FortiWeb cannot classify the file and blocks the upload by default. This behavior is commonly observed when application frameworks abstract or omit the filename during upload processing. Allowing the Empty File Name special file type enables FortiWeb to continue evaluation instead of immediately rejecting the request.
File name [blob]: Illegal file type
This occurs when the application sends the uploaded file as a generic object (for example, 'blob') rather than a traditional filename with an extension. FortiWeb validates files using the following logic:
If the filename is not reliably exposed by the application, suffix-only validation fails, and the upload is blocked. This behavior may be observed with ASP.NET applications and other frameworks that similarly manage uploads.
Resolution: When configuring allowed file types:
After applying these changes, legitimate uploads for the allowed file types should succeed, while non-matching file types remain blocked. |