Troubleshooting Tip: File upload restriction blocking application traffic 'msg File name Illegal file type' due empty name
| Description | This article describes when a FortiWeb administrator finds events in the attack logs about traffic that was either alerted or blocked by the file upload restriction due to an empty name. |
| Scope | FortiWeb v7.4.x. |
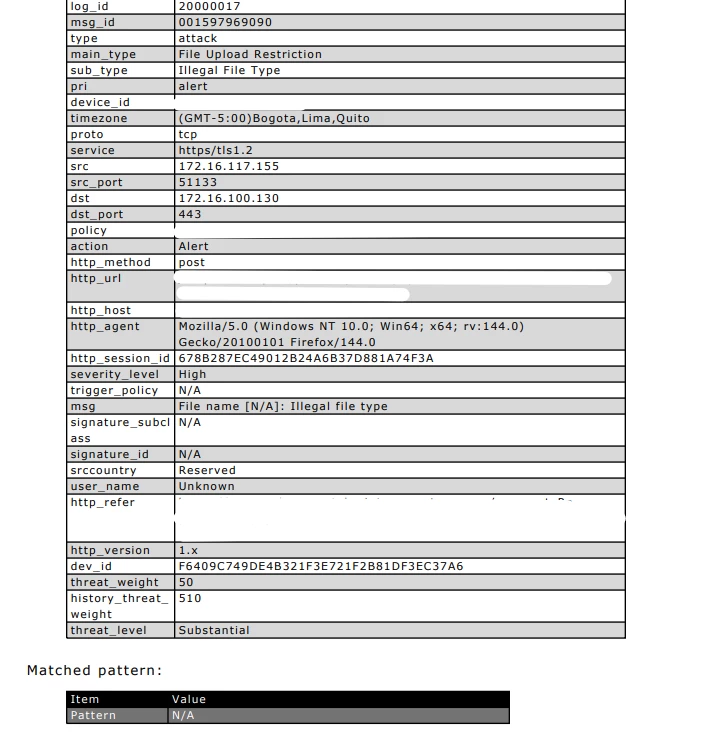
| Solution | In the attack log section, the administrator finds logs with 'File name [N/A]: Illegal file type'.
For more in-depth troubleshooting, the administrator can run debugging commands related to file uploads.
diagnose debug flow filter module-detail file-mime 7
The administrator will identify patterns about empty file names associated with blocked traffic.
Content-Disposition: form-data; name="archs[]"; filename=""
To fix the issue, upgrade FortiWeb to version 7.4.6 and above.
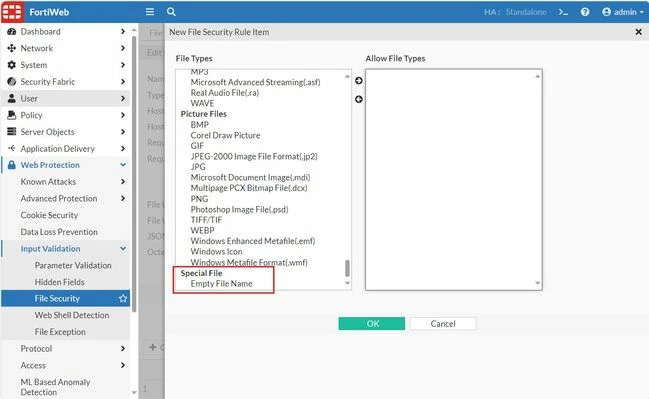
Go to Web Protection -> Input Validation -> Web Security. In the File Security Rule, move 'Empty File Name' from the 'Special File' category to 'Allowed File Types'.
CLI commands:
config waf file-upload-restriction-rule
Note:
Related documents: |