bkashava
Staff
Staff
February 17, 2026

Technical Tip: Preventing false positives during Nextcloud file uploads in FortiWeb

  • February 17, 2026
  • 0 replies
  • 357 views
Description

This article explains how to prevent false-positive attack detections when uploading files (such as PDF or image files) to a Nextcloud application protected by FortiWeb.

Scope FortiWeb.
Solution

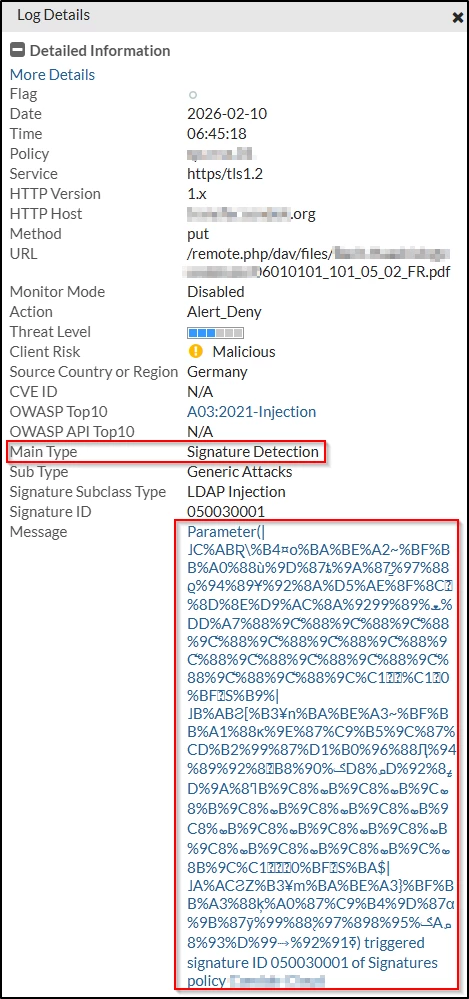
When protecting applications like Nextcloud, FortiWeb may inspect HTTP request bodies using attack signatures even when the payload is binary content (for example, PDF or image uploads via /remote.php/webdav/).

1.png


Because binary payloads are not text-based, this inspection can result in false positives and blocked uploads.


To avoid this behavior, enable payload-based content type detection on the affected server policy. This allows FortiWeb to determine the real payload type and skip body attack signature inspection for non-text content.

Configure via the CLI:

config server-policy

    edit <server_policy_name>

        set payload-based-content-type enable

    next

end

After enabling this option:

  • FortiWeb evaluates the actual payload content type.
  • Attack signature inspection of the request body is skipped for binary content such as PDFs and images.
  • Text-based payloads (HTML, XML, JSON, form data, etc.) continue to be inspected normally.

This setting affects only body inspection behavior and does not disable other FortiWeb security checks.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!