faical
Staff
Staff
April 29, 2025

Technical Tip: How to use TACACS+ attribute for admin authorization when accessing FortiWeb

Description

The article explains how to configure FortiWeb to use TACACS+ attribute for authorization (FortiAuthenticator as TACACS+ server).

Scope

FortiWeb.

Solution
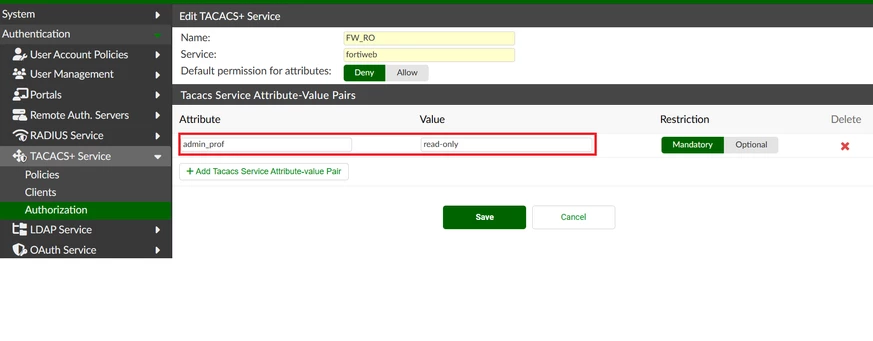
  1. FortiAuthenticator should already be configured as a TACACS+ server with a local user and the authorization rule. Then, a service to be added to the rule using the attribute value pair: admin_prof=read-only (FortiWeb only supports the attribute admin_prof):


FAC.png


The rest of the configuration should be as follows (TACACS is the local username on FortiAuthenticator):
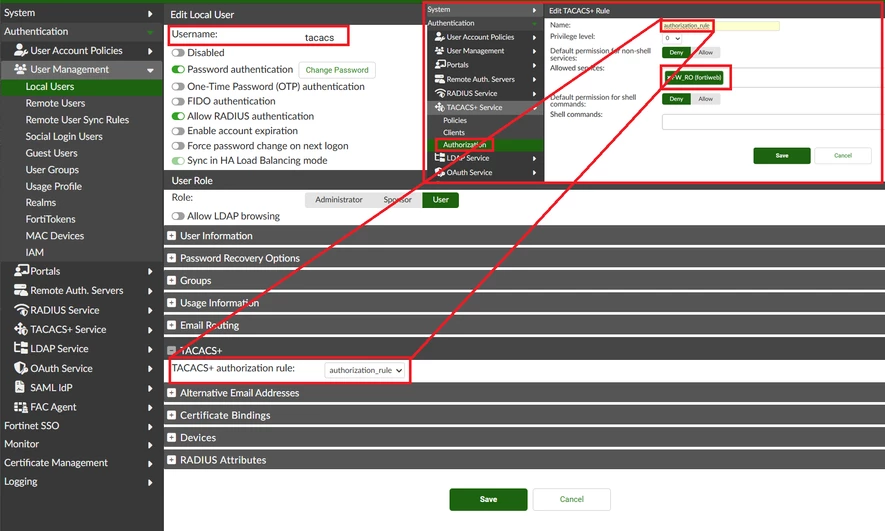
 

autho.png


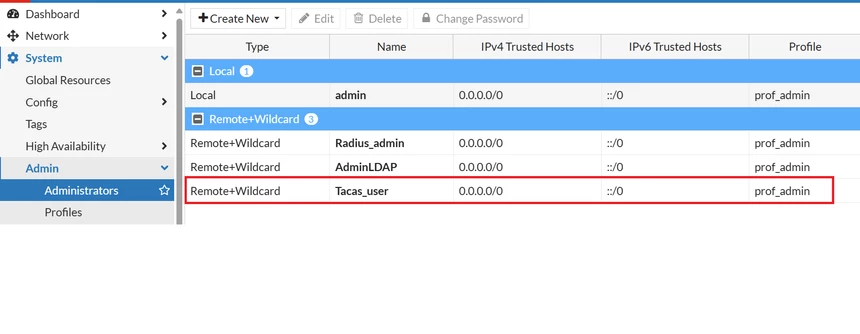
  1. An Administrator 'Tacacs_user' (as an example) to be added on FortiWeb, pointing to FortiAuthenticator IP:


    Administrators.png


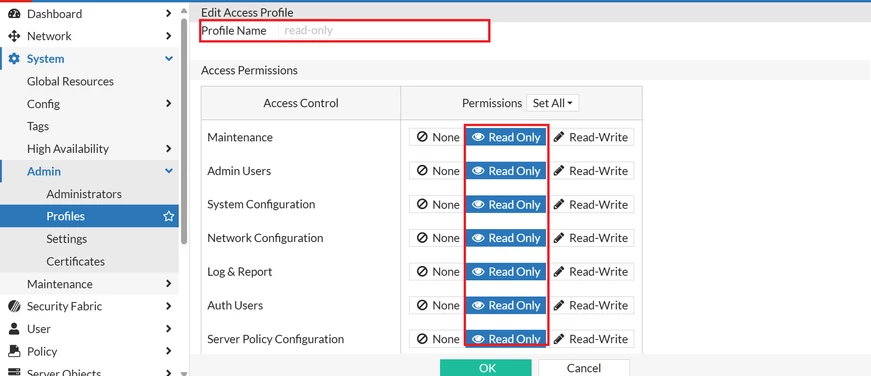
  2. A profile name to be created on FortiWeb, 'read-only' matching exactly the attribute value created on FortiAuthenticator above. This profile can be customized as per need :


    Admin_profile.png


  3. Access profile override to be enabled on CLI:


FortiWeb# config system admin

FortiWeb (admin) # edit Tacas_user

FortiWeb (Tacas_user) # set accprofile-override enable

FortiWeb  (Tacas_user) # end


After the authentication of TACACS+ user (for example via FortiWeb CLI), no configuration is allowed as it is set read-only:


FortiWeb $ config

<Enter>


Related document:

Offloading HTTP authentication and authorization


Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT