Technical Tip: How to enable and require client certificates for specific URLs only
| Description | This article describes how to enable and require client certificates for specific URLs only. |
| Scope | FortiWeb and FortiWeb-VM. |
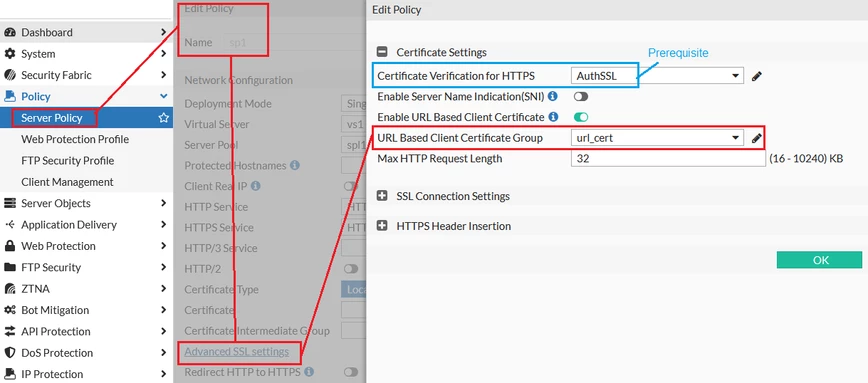
| Solution | Prerequisite: Enable the Client Certificate Verification in FortiWeb Server Policy by following the guide at the end of this article.
There is a requirement to require a client certificate from a client access for only a specific URL instead of the full website URL.
For example:
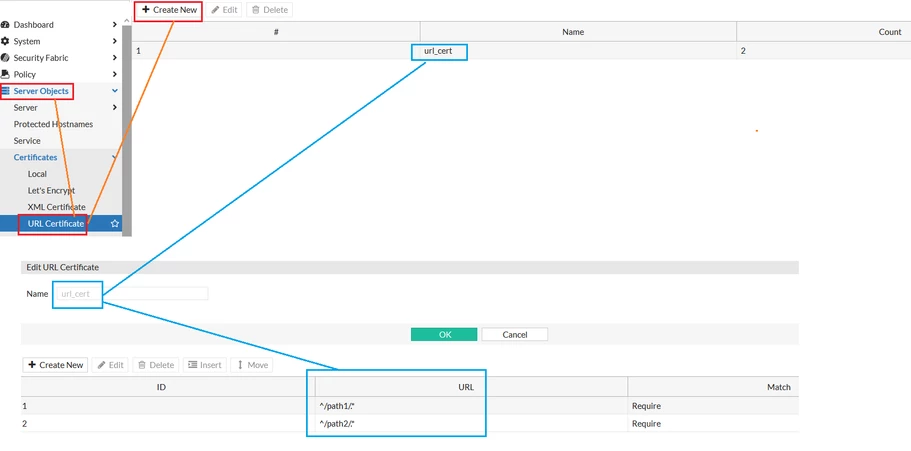
FortiWeb provides the option to achieve this requirement using the URL Certificate feature. The feature supports multiple URLs.
Step 1: Create a new URL Certificate rule and specify the respective URLs:
Step 2: Select and apply the URL Certificate rule created in Step1 for the respective Server Policy:
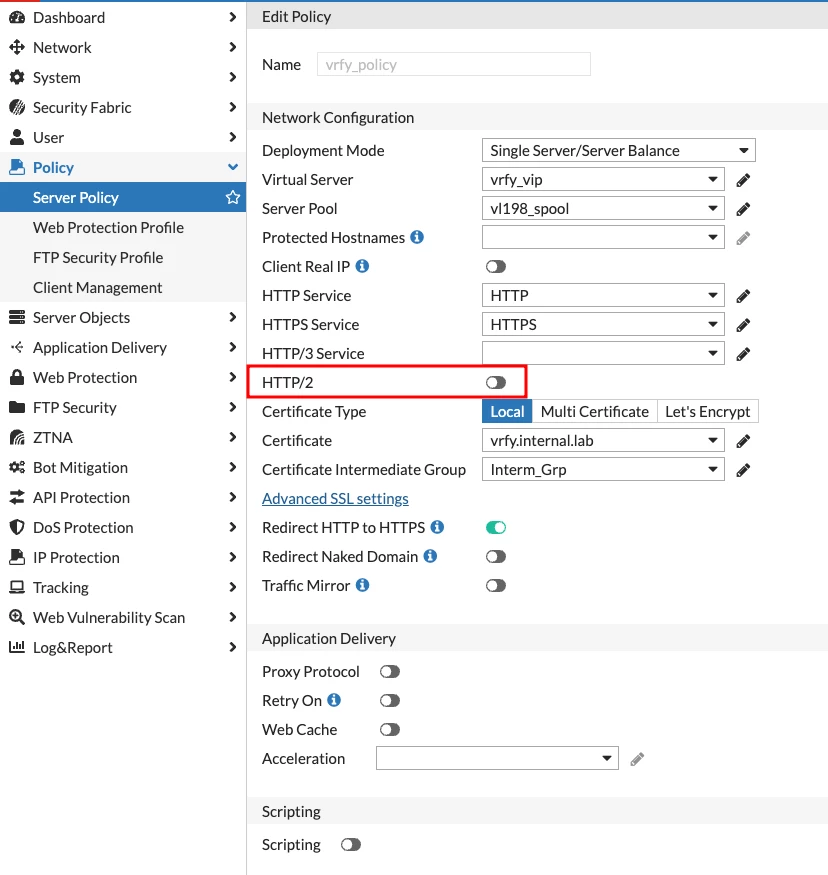
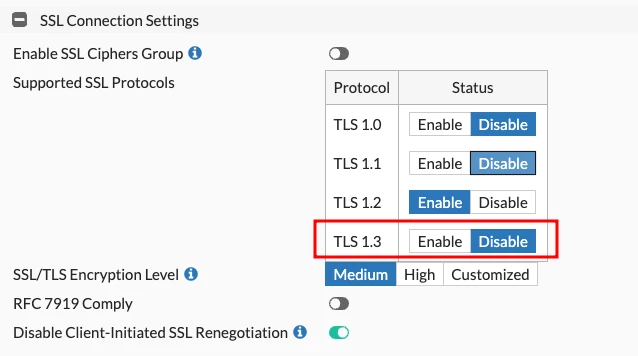
Note:
Related documents: How to apply PKI client authentication (personal certificates) |