kmak
Staff
Staff
June 9, 2025

Technical Tip: How to configure OAuth 2.0 for Server Policy Frontend Authorization with Integration of FortiAuthenticator as the OAuth Server

  • June 9, 2025
  • 0 replies
  • 694 views
Description This article describes how to configure OAuth 2.0 for server policy frontend authorization with integration of FortiAuthenticator as the OAuth Server.
Scope FortiWeb, FortiAuthenticator.
Solution

Prerequisite:

  • FortiWeb is configured to work as an OAuth 'Open Authorization' client.
  • The FortiAuthenticator interface is enabled with the OAuth services.


Create an OAuth Resource Server service in FortiAuthenticator:
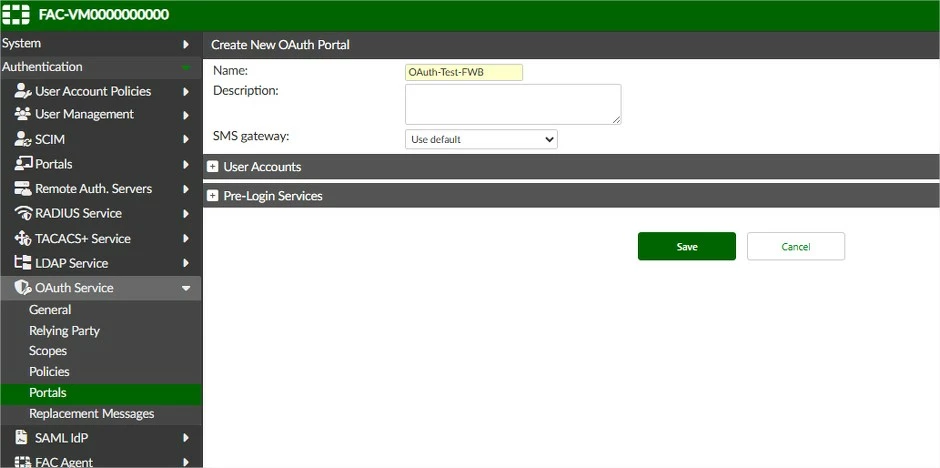
  1. Create the OAuth Portal in the OAuth Service:


kmak_0-1749443054510.jpeg


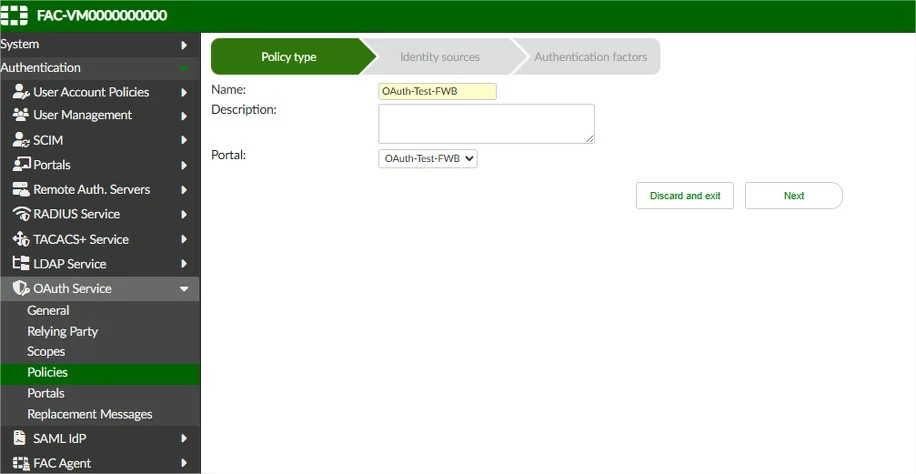
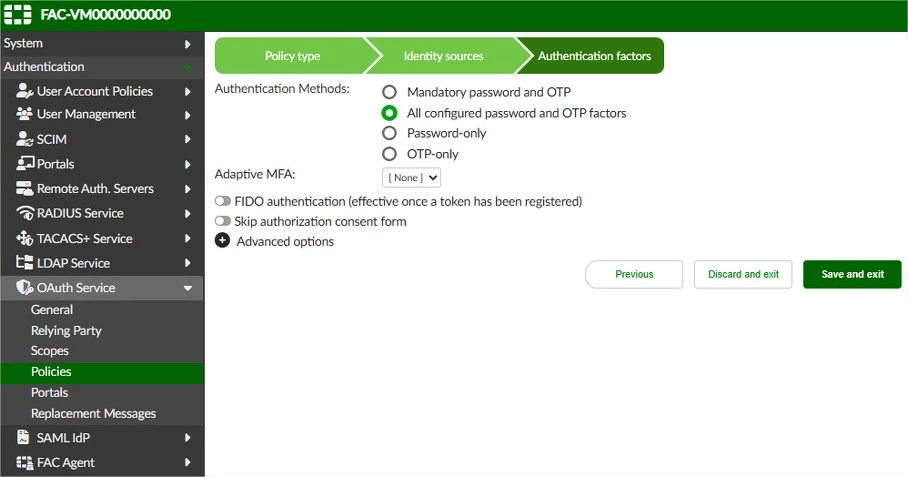
  1. Create the OAuth policy and select the OAuth Portal that is being created in the previous step.


kmak_1-1749443054518.jpeg


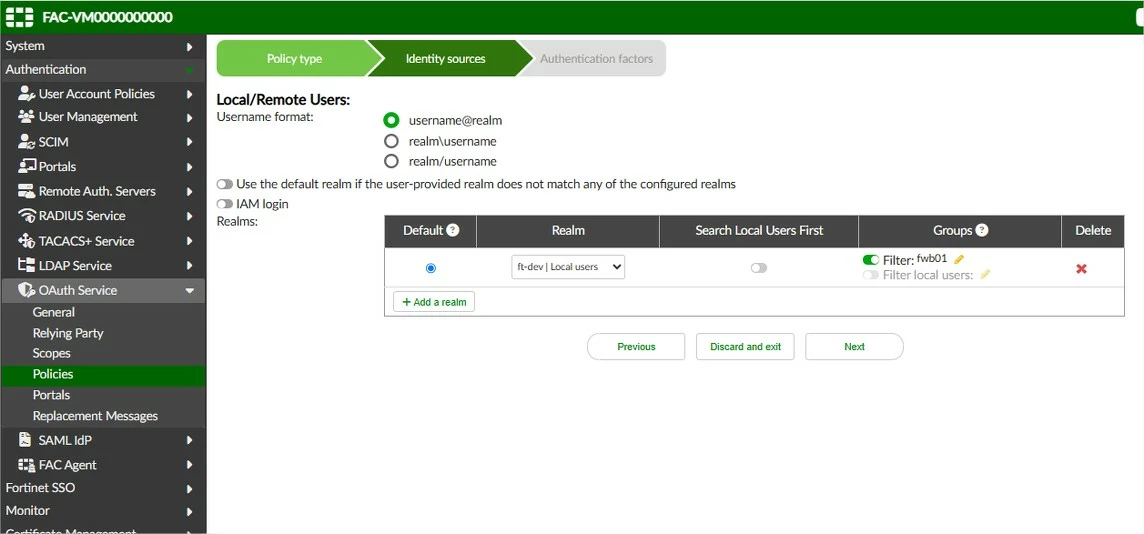
  1. In the OAuth policy identity sources setting, select the specific realm if necessary. Enable the group filter to allow specific group users to authenticate with the OAuth policy.


kmak_2-1749443054525.jpeg


  1. Save and exit the OAuth Policy settings:


kmak_3-1749443054530.jpeg


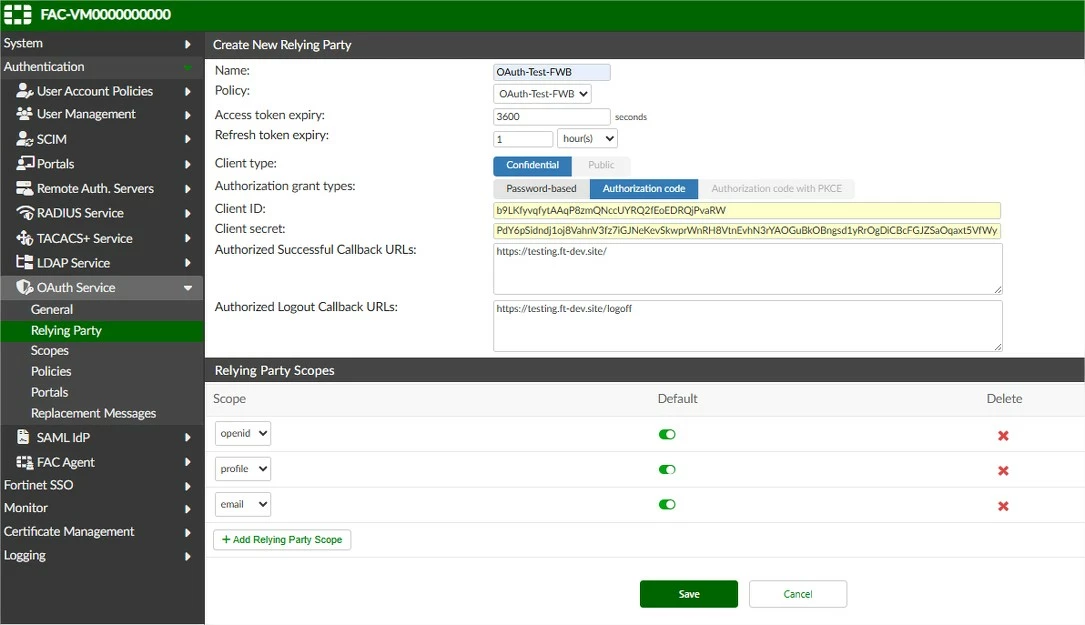
  1. Create the Relying Party and select the OAuth Policy created in the previous step. Adjust the Token expiry based on the requirements. In the Client type option, select Confidential and select Authorization code for Authorization grant types. Copy and store the client ID and client secret in a file, as the client secret value will be displayed only once. Insert the URLs that will be redirected to by the OAuth configured in FortiWeb and the logoff path of the website to log out of OAuth. Add at least one relying party scope to the relying party.


kmak_4-1749443054551.jpeg


Configure the OAuth Site Publishing policy in FortiWeb:
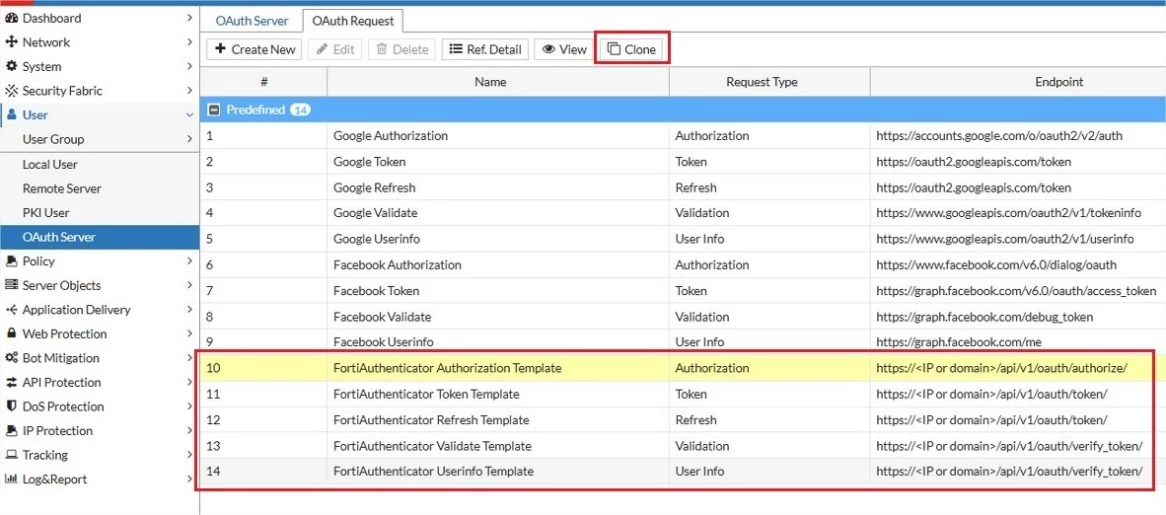
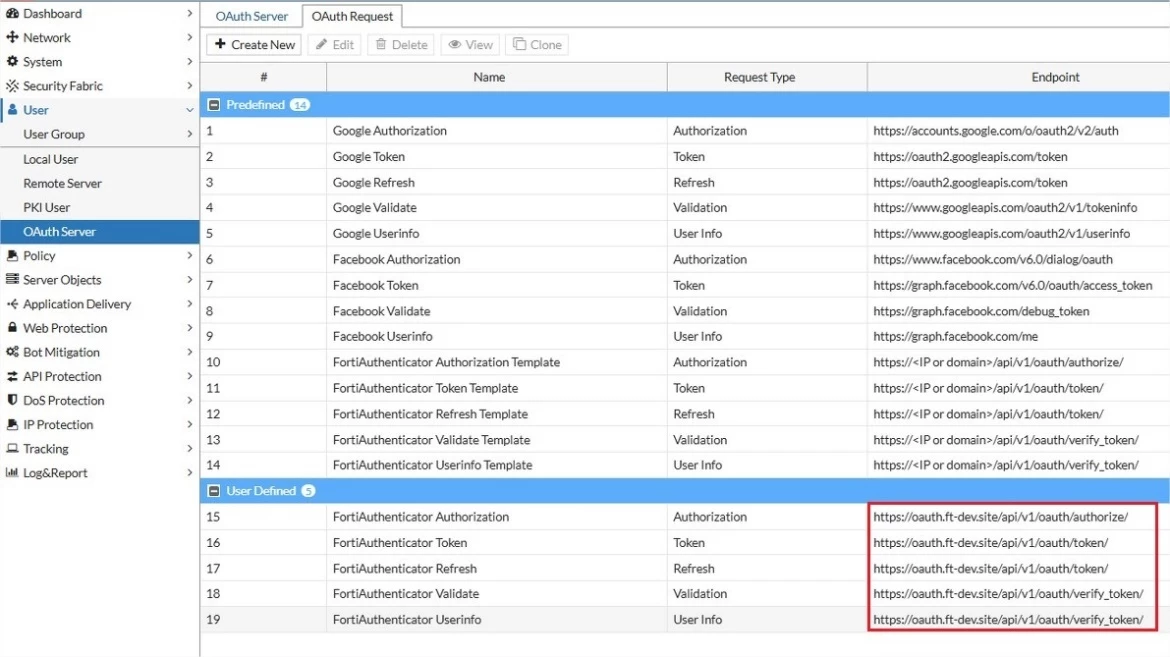
  1. After completing the configurations in FortiAuthenticator, move on to FortiWeb. Create the OAuth Request by cloning all five FortiAuthenticator OAuth request templates.


kmak_5-1749443054559.jpeg


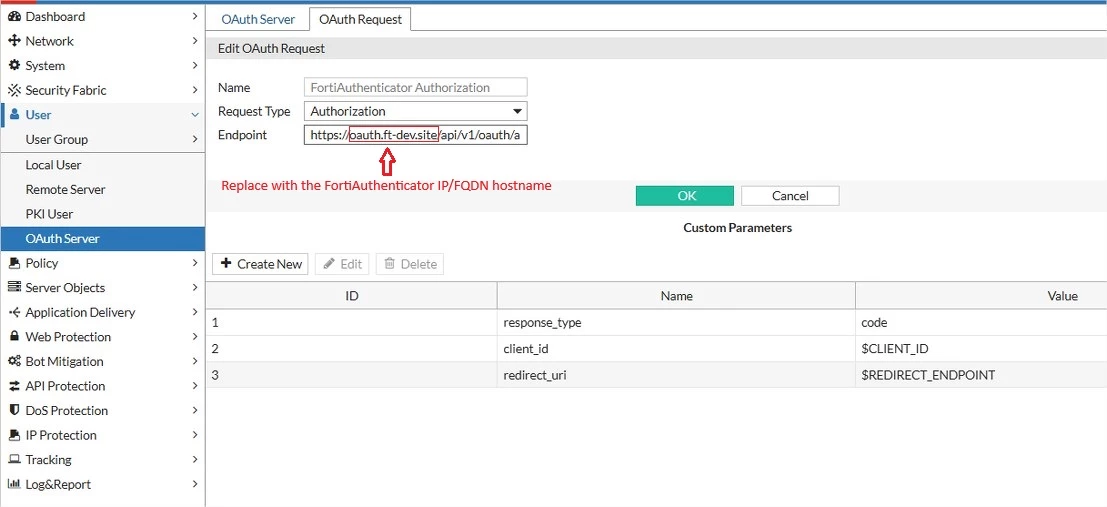
  1. Edit each of the cloned OAuth requests and replace the endpoint URL IP/Domain settings with the FortiAuthenticator IP or FQDN hostname.


kmak_6-1749443054565.jpeg


  1. Make sure all the OAuth Request has the correct endpoint URL.


kmak_7-1749443054579.jpeg


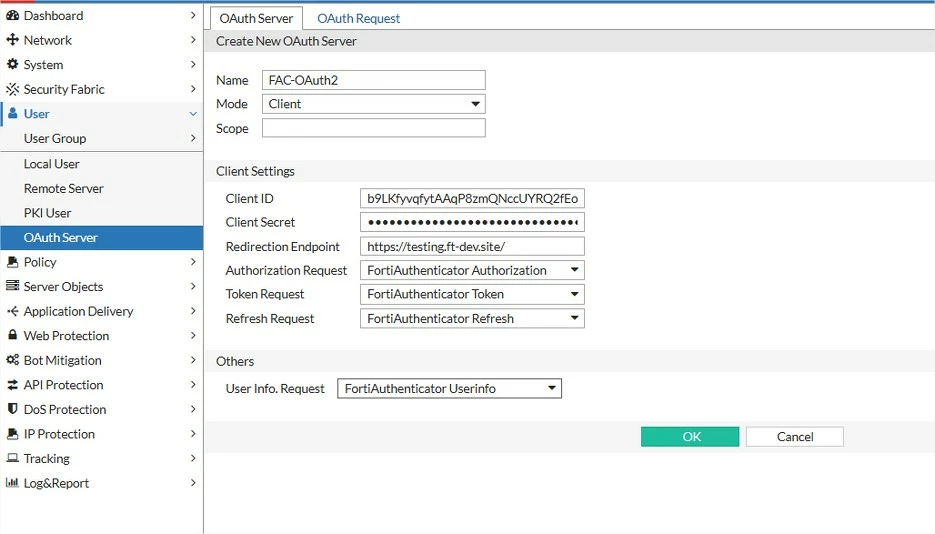
  1. Navigate to the OAuth Server tab and create a new OAuth Server. In this example, FortiWeb is acting in the OAuth Client mode. Insert the Client ID and Client Secret using the value copied from the FortiAuthenticator OAuth Relying Party. The Redirection Endpoint must be the same as the URL value configured in the FortiAuthenticator Authorized Success Callback URLs. For the list of requests on the page, select the OAuth Request that was cloned and edited in the previous steps.


kmak_8-1749443054585.jpeg


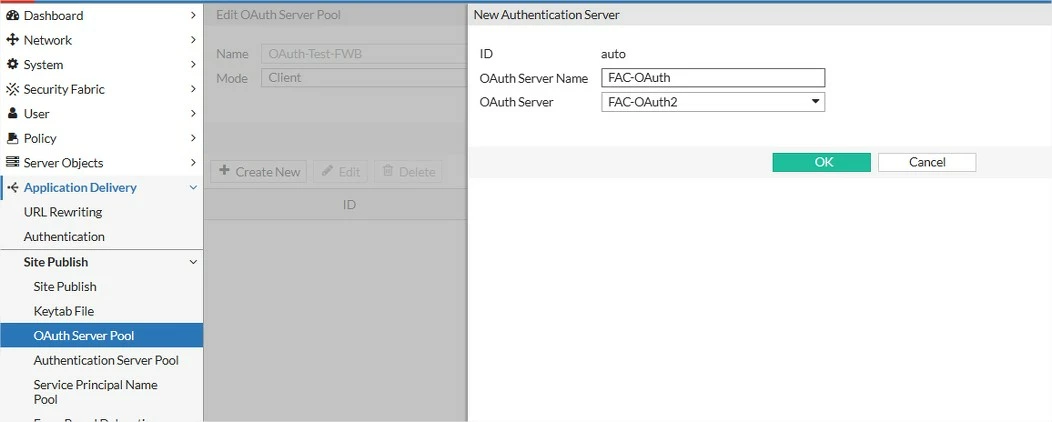
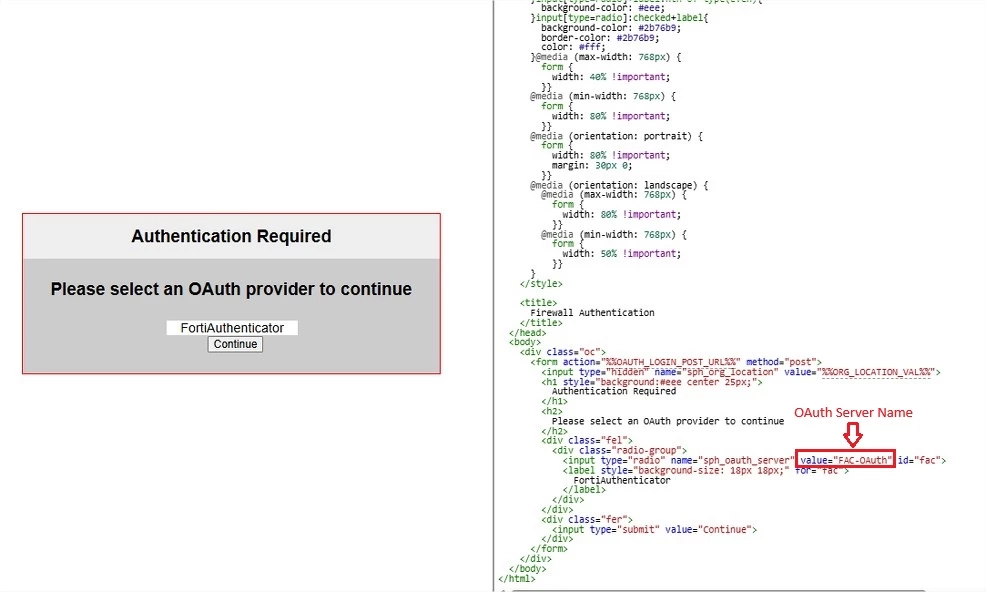
  1. Navigate to the OAuth Server Pool page under the Site Publish category. Create a new OAuth Server Pool with the same mode as the Client. Create the Authentication server in the OAuth Server Pool. Take note of the OAuth Server Name, as the value will be utilized in the FortiWeb Replacement Message later. Select the OAuth Server that is being created in the previous step.


kmak_9-1749443054588.jpeg


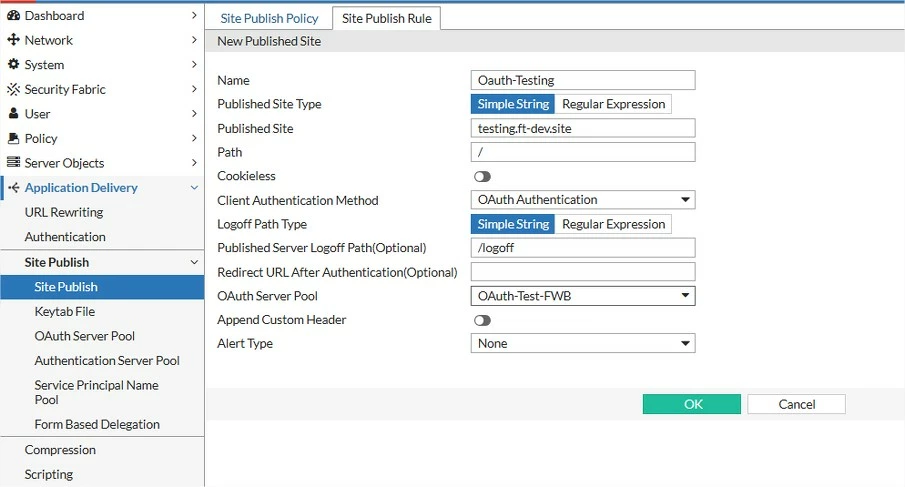
  1. Go to the Site Publish page and create a site publish rule. In the site publish rule, insert the name, published site, and path. Select the OAuth Authentication as the client authentication method and select the OAuth server pool with the pool created in the previous step.


kmak_10-1749443054593.jpeg


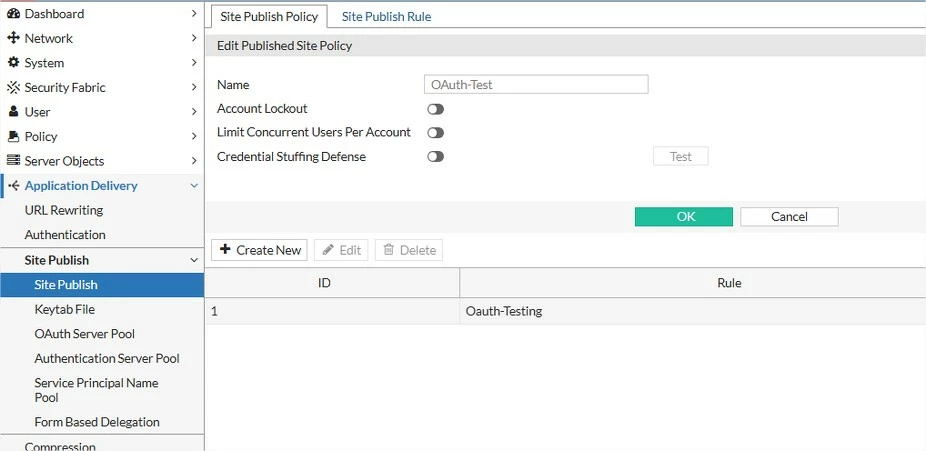
  1. Create the Site Publish Policy and add the Site Publish Rule to the policy.


kmak_11-1749443054595.jpeg


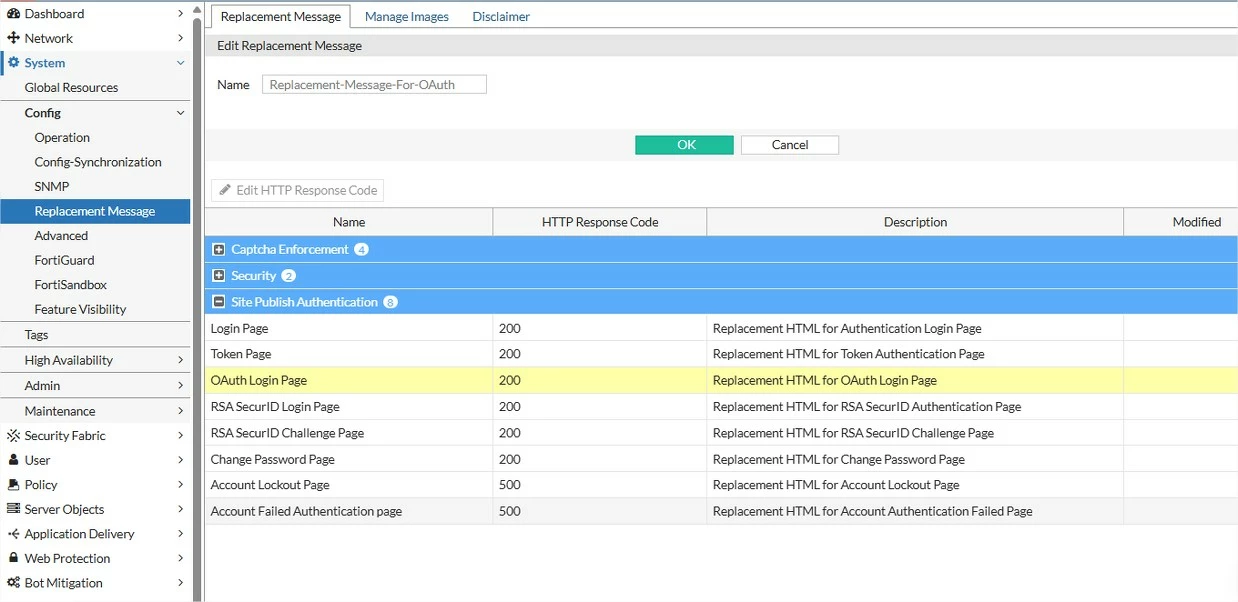
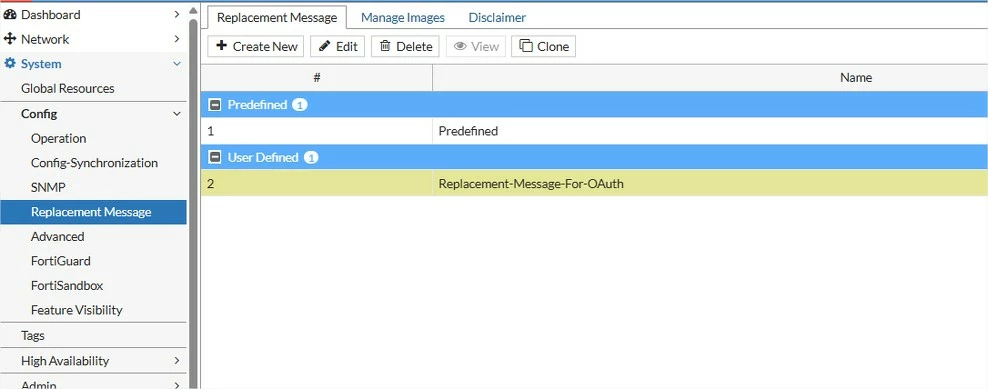
  1. The OAuth login page must be configured to match the OAuth Server name configured in [Step 5]. Clone the predefined Replacement Message policy to a new policy to customize the page.


kmak_12-1749443054598.jpeg


  1. Edit the OAuth Login Page in the Replacement Message policy.


kmak_13-1749443054603.jpeg


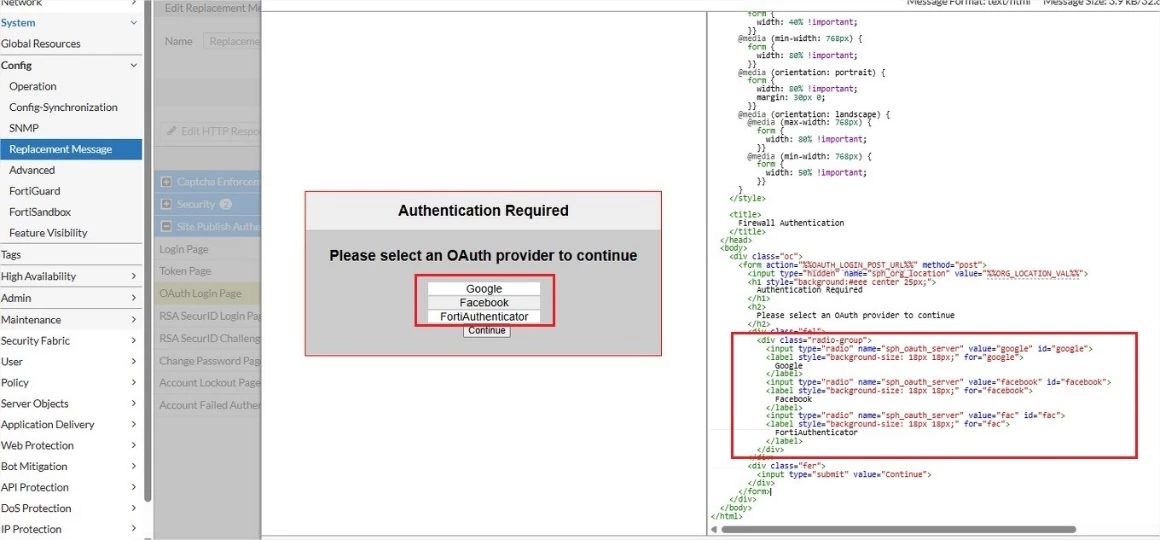
  1. The predefined OAuth login page comes with other OAuth Server provider types.


kmak_14-1749443054616.jpeg


  1. Remove the lines of the unwanted provider server type. Update the value of the FortiAuthenticator server using the OAuth Server name configured in Step 5.


kmak_15-1749443054623.jpeg


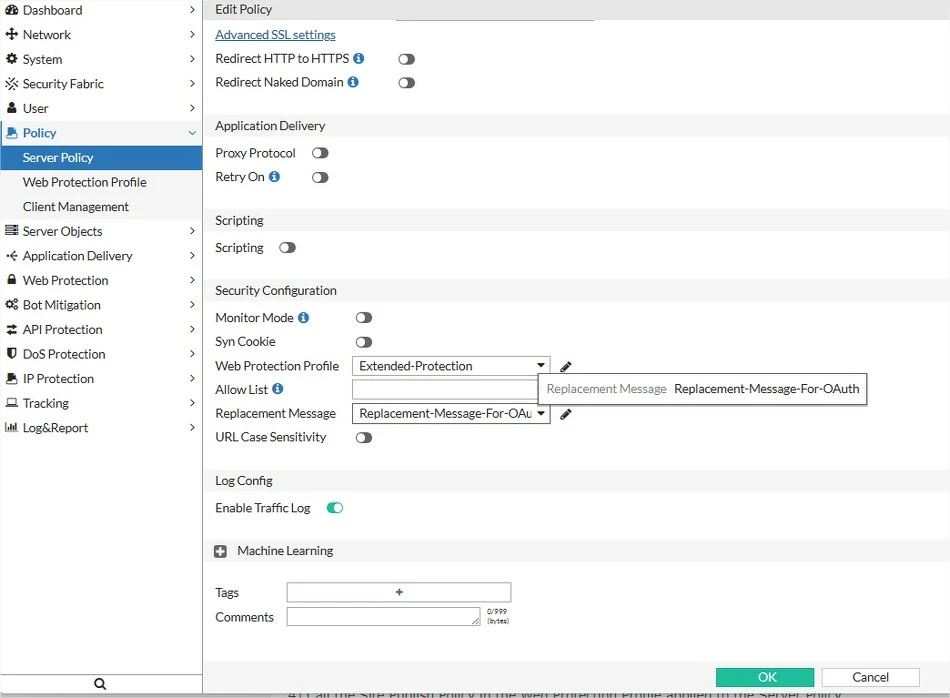
  1. The OAuth Site Publish Policy and the Replacement Message are configured. Navigate to the Server Policy to edit the relevant server policy and configure the Replacement Message policy.


kmak_16-1749443054629.jpeg


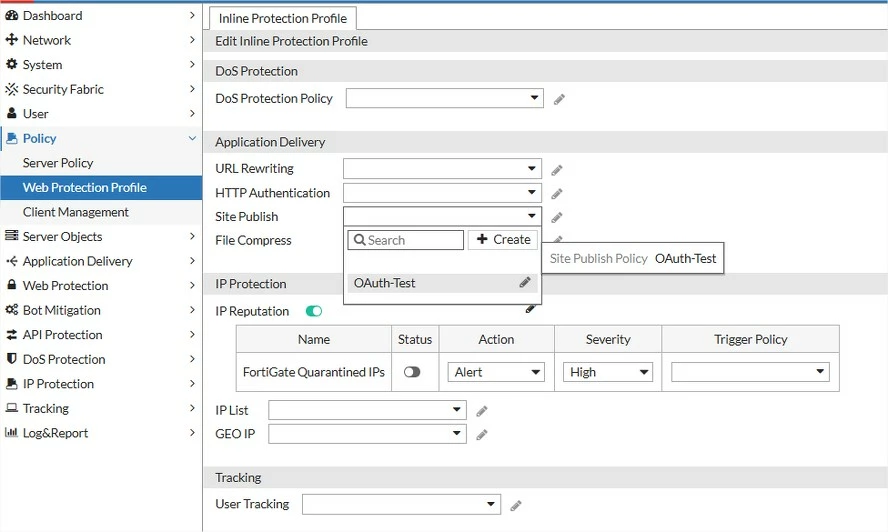
  1. Edit the Web Protection Profile of the Server Policy to enable the Site Publish Policy rule.


kmak_17-1749443054633.jpeg


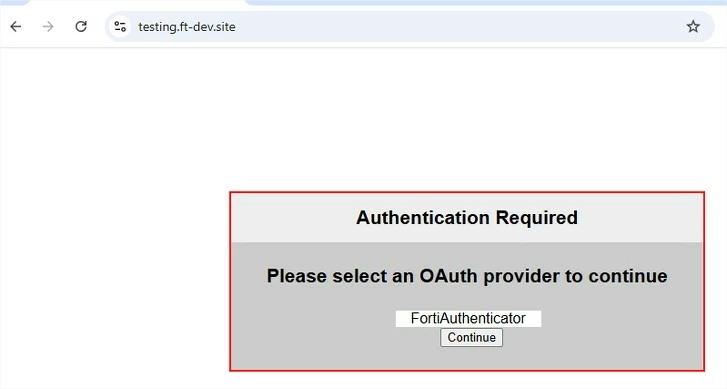
  1. Test browsing the website pointing to the server policy. The host matching the published site shall trigger the Site Publish OAuth policy, and users will be returned with the OAuth login page.


kmak_18-1749443054634.jpeg


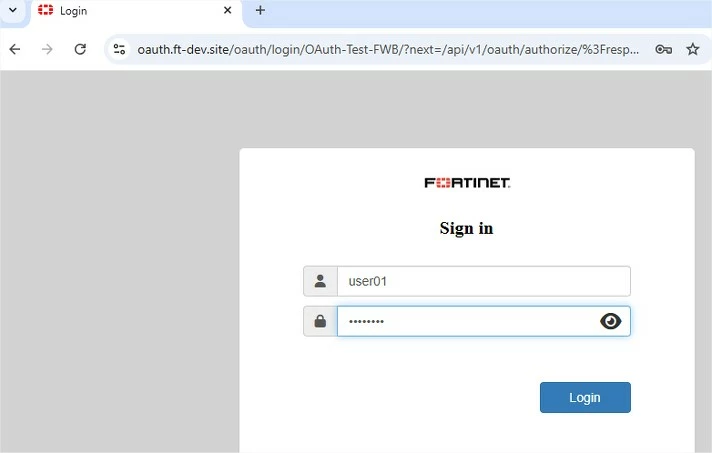
  1. Select FortiAuthenticator and continue; users will be redirected to the OAuth login page. Insert the valid username and password to log in.


kmak_19-1749443054636.jpeg


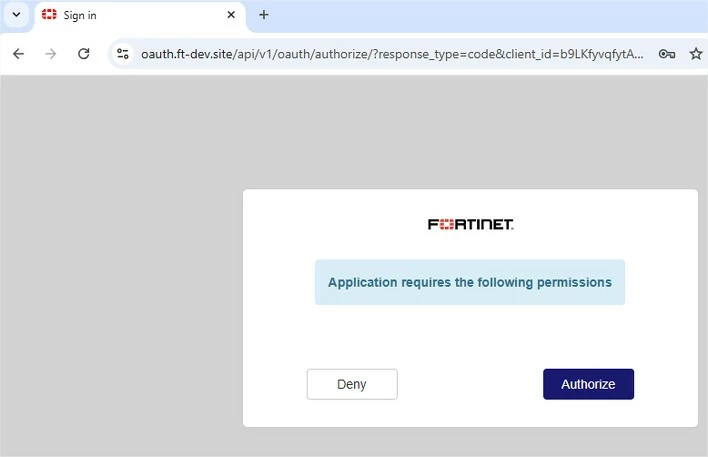
  1. Users will be prompted with the Authorize page after successful login. Select Authorize to continue.


kmak_20-1749443054637.jpeg


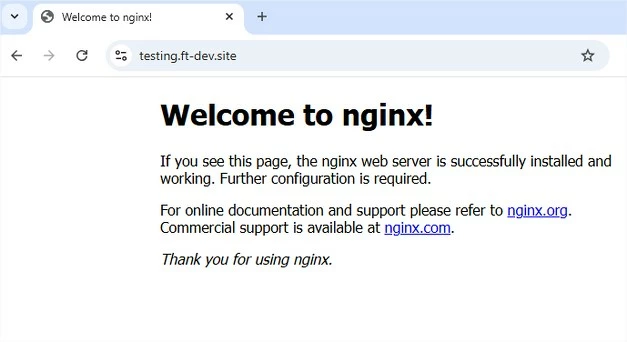
  1. The page is now showing the actual contents from the backend real server after passing the OAuth login.


kmak_21-1749443054641.jpeg


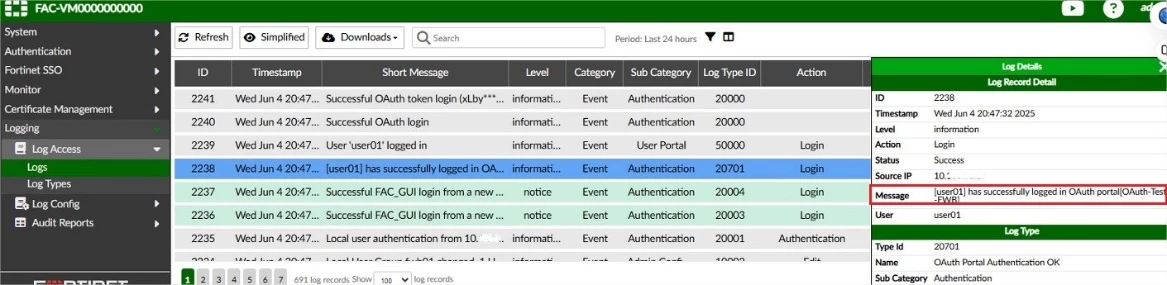
  1. Both FortiAuthenticator and FortiWeb shall be able to track the OAuth login activity if logging is enabled.


FortiAuthenticator:


kmak_22-1749443054657.jpeg


FortiWeb:


kmak_23-1749443054660.jpeg


Related documents:

OAuth authorization & OIDC authentication

OAuth Service
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!