| Solution | FortiWeb can be used to block the traffic coming from 'http_agent="Custom-AsyncHttpClient"'. This can be achieved by using a Custom Policy. Steps can be performed as below: - Navigate to Web Protection -> Advanced Protection -> Custom Policy -> Custom Rule -> Create New, give it a name accordingly, and select OK.
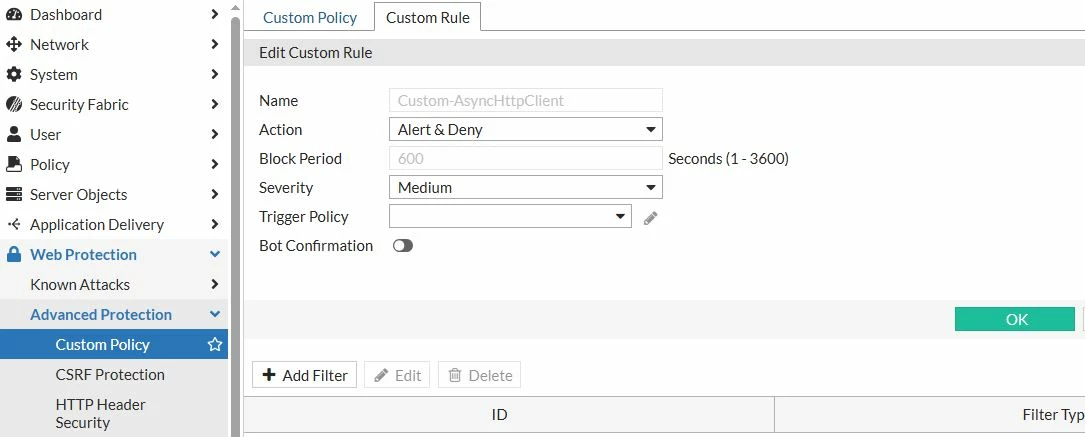 - After the rule is made, add a filter below the rule. Select Add Filter -> HTTP Header -> Select OK.
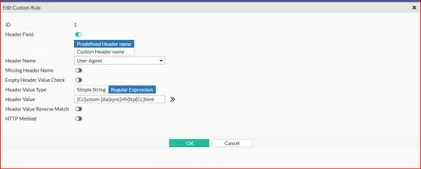
- Once it further opens the HTTP Header menu, set the Header Field as 'Predefined Header name' and Header Name as 'User-Agent'.
- In the Header Value Type, set it as Regular Expression.
- Inside the Header Value, fill the syntax as '[Cc]ustom-[Aa]sync[Hh]ttp[Cc]lient' (this can be modified based on the http_agent in the traffic logs) and select OK.
From CLI: config waf custom-access rule
edit "UserAgent"
set action alert_deny
config source-ip-filter
end
config http-header-filter
edit 1
set predefined-header user-agent
set header-value [Cc]ustom-[Aa]sync[Hh]ttp[Cc]lient
next
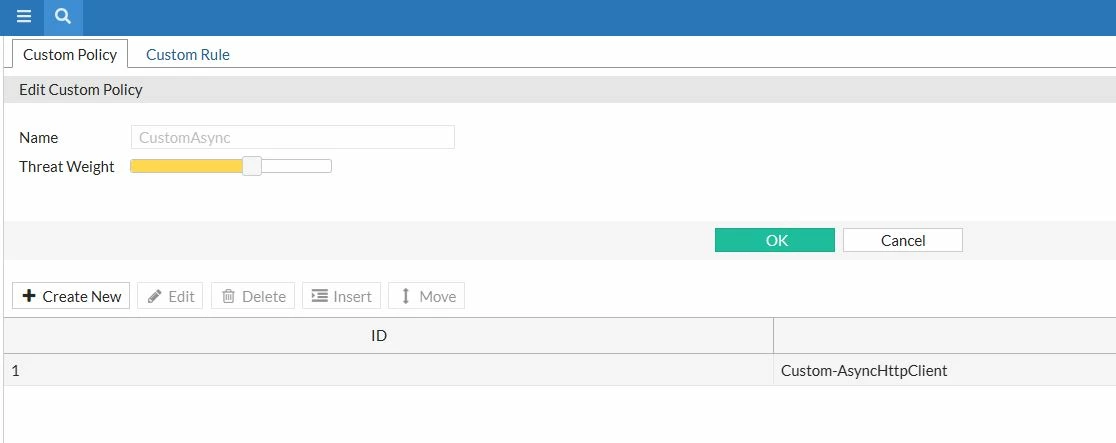
end - Once the rule is created, proceed with creating a Custom Policy and call the rule in that policy.
 From CLI: config waf custom-access policy
edit "USerAgent"
config rule
edit 1
set rule-name UserAgent
next
end
next
end -
Once this is set up, call the Custom Policy in the required Web-protection profile, under Policy -> Web Protection Profile -> Custom Policy, and select OK.
Note: If the issue is not resolved, then reach out to the Support with the required config and logs. The Regex code used above might need to be modified based on the requirement.
Related document:
custom-policy |






