



Technical Tip: How to add an exception in a signature
Description | This article describes how to add an exception for a Signature. |
Scope | FortiWeb. |
Solution | Explanation: There are multiple ways to add an exception in the Signature.
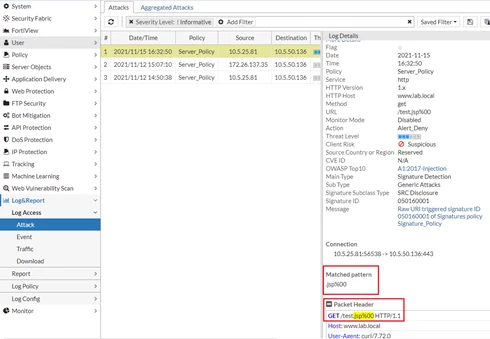
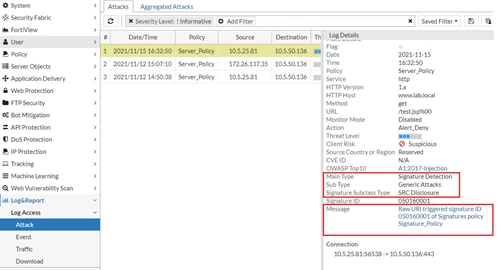
The attack log states that FortiWeb blocked the HTTP request containing the matching pattern .jsp%00 in the URI.
Now check what this signature is all about by simply selecting the ‘Message: RAWURI triggered signature ID 050160001 of signature policy Signature_Policy’ and then selecting the ‘View Signature’ option.
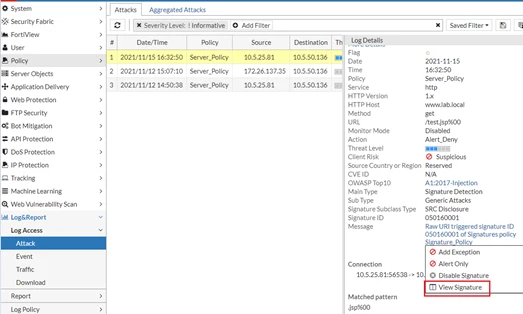
The description of the signature says: 'This signature prevents information disclosure. This injection can be achieved in HTTP URL.'
To explain it in detail, an attacker can make the remote web server disclose the source code of its JSP pages by appending a NULL character to the name of the JSP files requested (for example, 'foo.jsp%00', ‘test.jsp%00’). 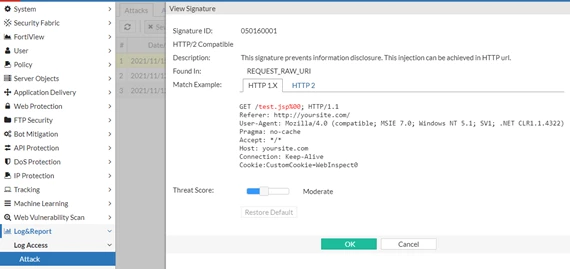
If this type of request is legitimate in the environment, then it is possible to add an exception by using one of the methods mentioned below.
Method 1:
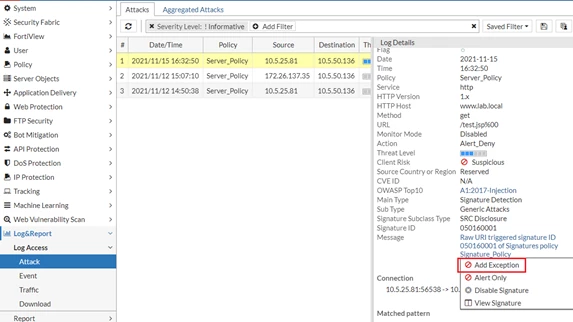
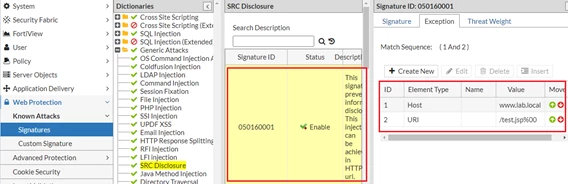
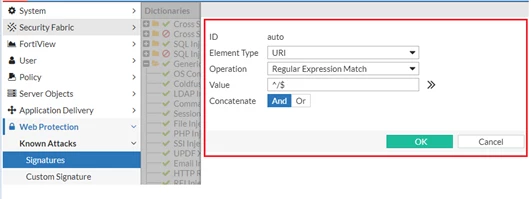
It is possible to select the desired Element type based on the strictness level of the exception to add.
Method 2:
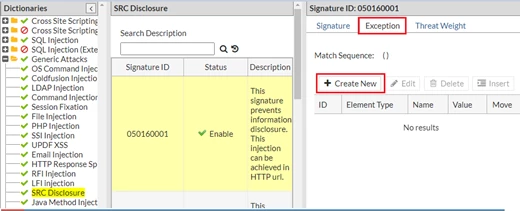
Navigate to Web Protection -> Known attacks -> Signatures -> Generic Attacks(SubType) -> SRC Disclosure (Signature Subclass type) and find the Signature ID 050160001 in the list. 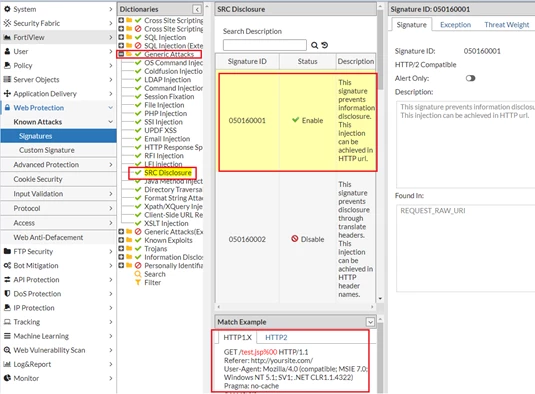
Select the Exception button and add an exception.
Method 3:
In this case, the triggered Signature ID is 050160001. 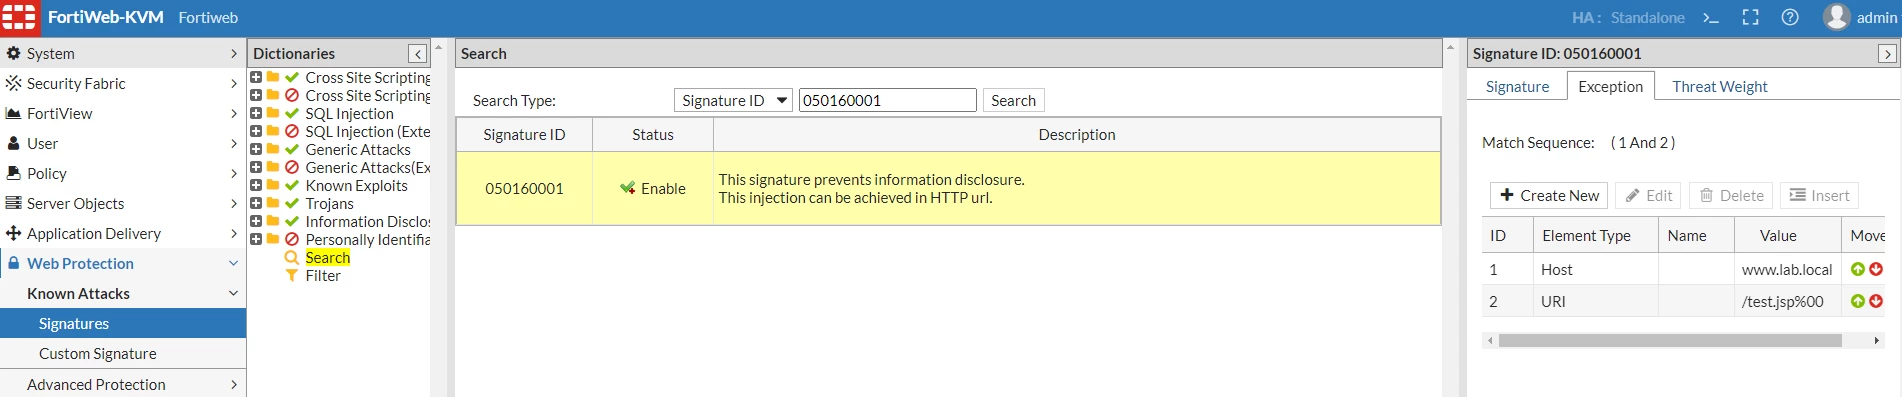
Once the exception is added, the HTTP request matching the exception rule will not be blocked. |

