


Technical Tip: FortiWeb 'period block' only blocks that client IP for that particular server policy only when multiple server policies exist
| Description | This article describes the behavior of how a client IP address is blocked after it has triggered a 'period block' in one of the server policies.
In FortiWeb, multiple Server Policies can be configured with different Web Protection profiles. These different Web Protection profiles can have different settings for violation of signatures.
For example, Server Policy 1: action 'period block'. Server Policy 2: action 'alert only'.
In such a case, even if a client IP has already triggered a 'period block' of Server Policy 1, this same client IP can still pass through Server Policy 2, which is only configured with action 'alert only'.
In other words, the action of 'period block' is 'per Server Policy' only. |
| Scope | FortiWeb. |
| Solution | For example: 2 Server Policies are configured in FortiWeb.
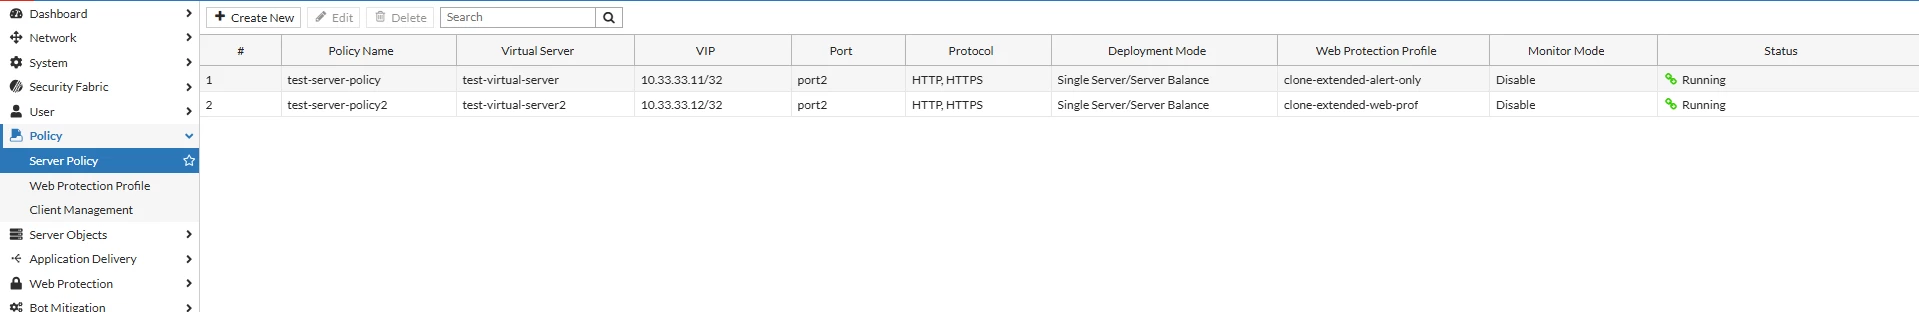
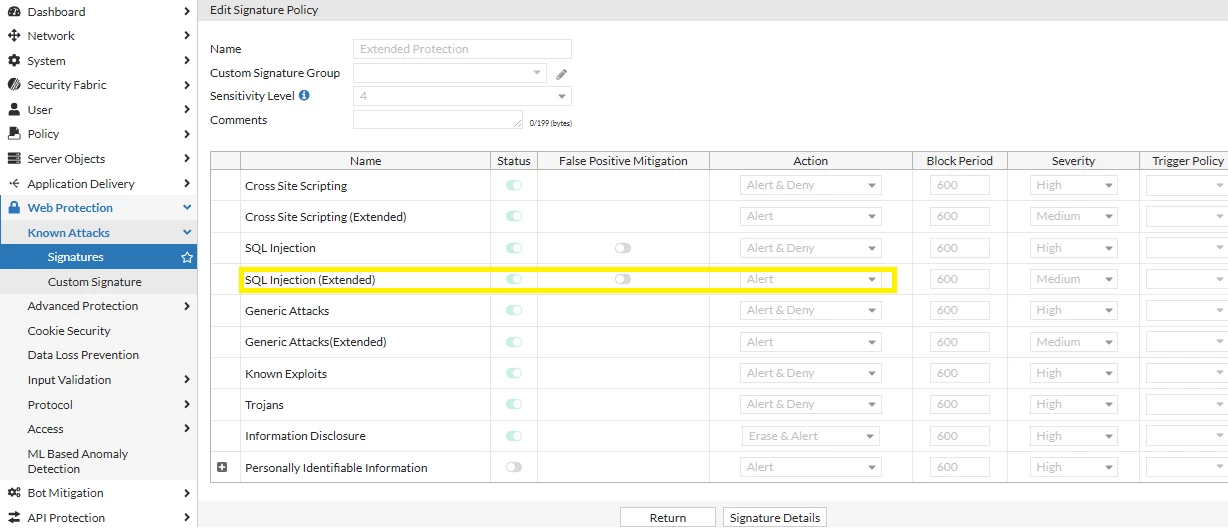
Server Policy 1 is configured with the Web Protection Signature profile of default “alert only” for violation of SQL Injection (Extended).
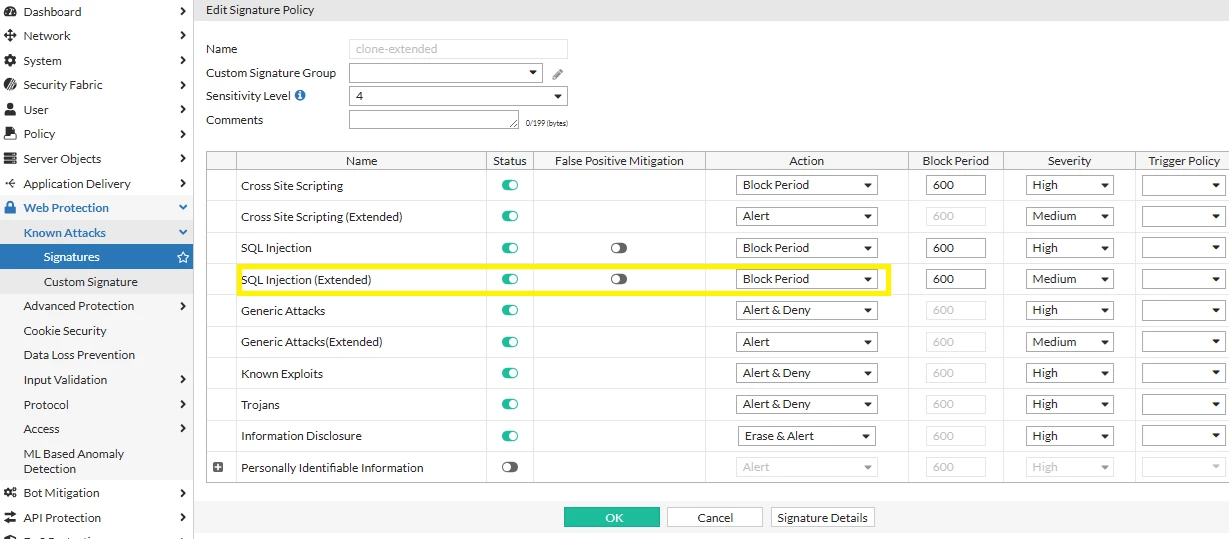
Server Policy 2 is configured with a Web Protection Signature profile of 'period block' for violation of SQL Injection (Extended).
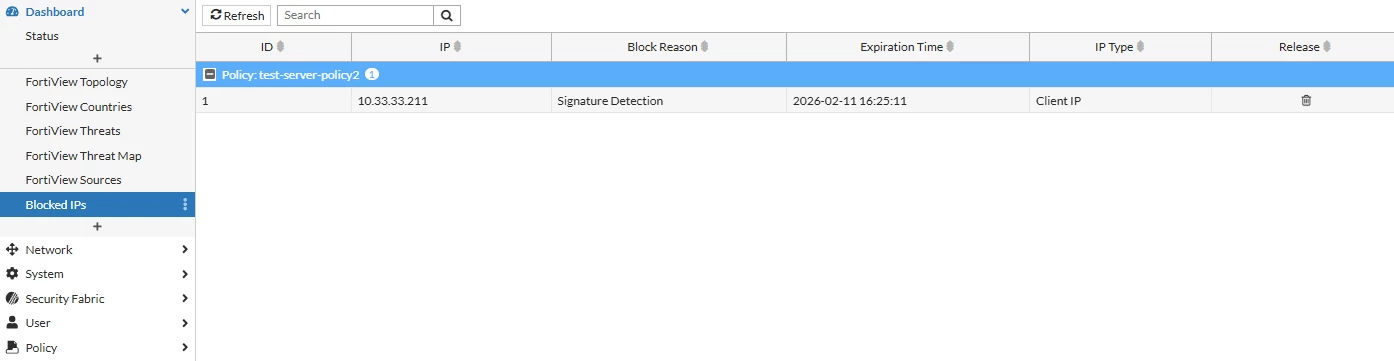
Now, client 10.33.33.211 has triggered 'period block' on Server Policy 2.
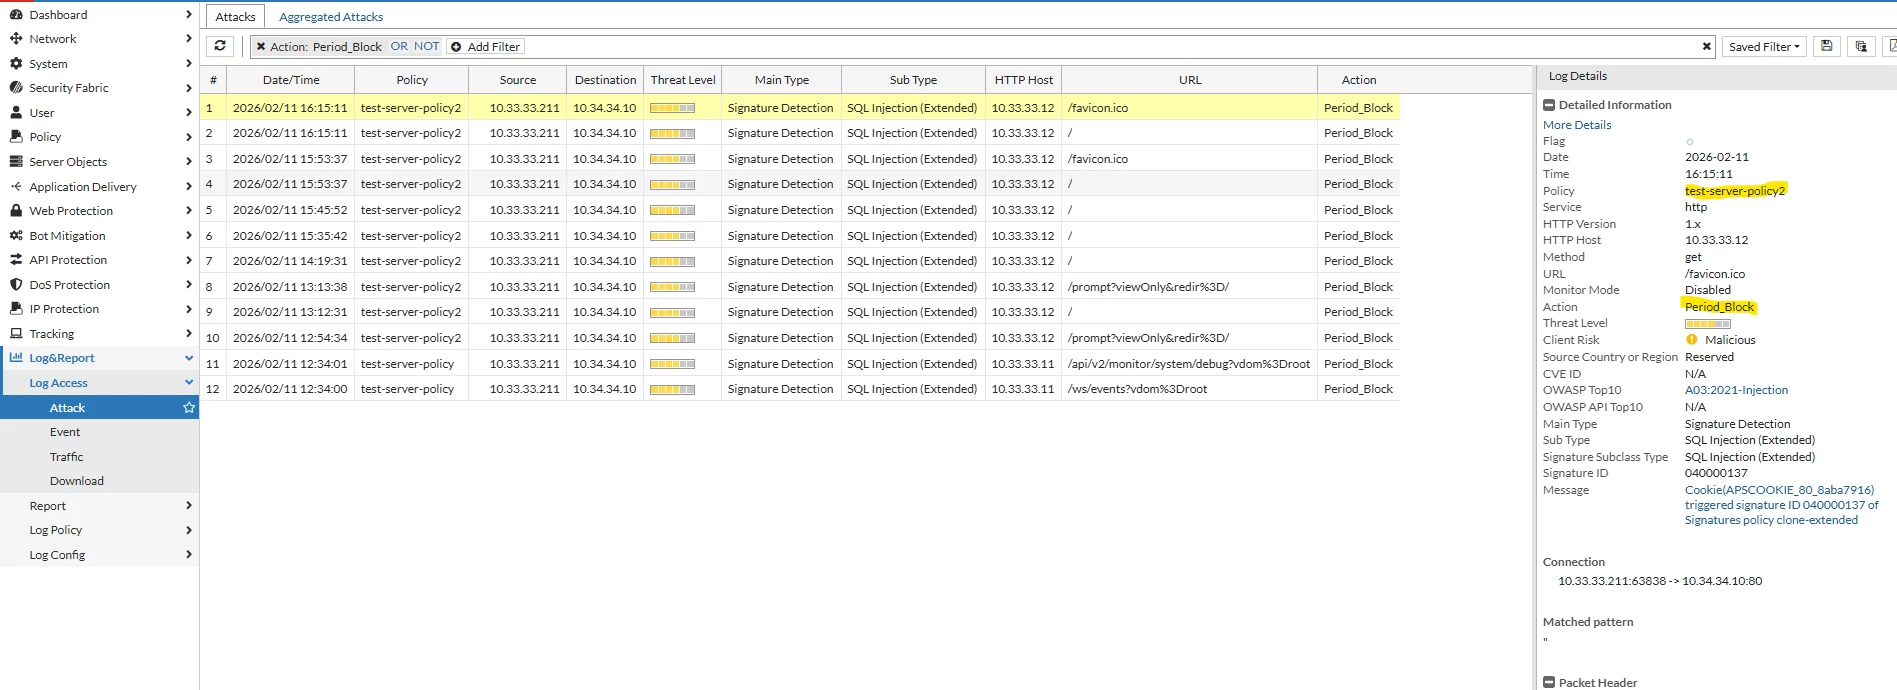
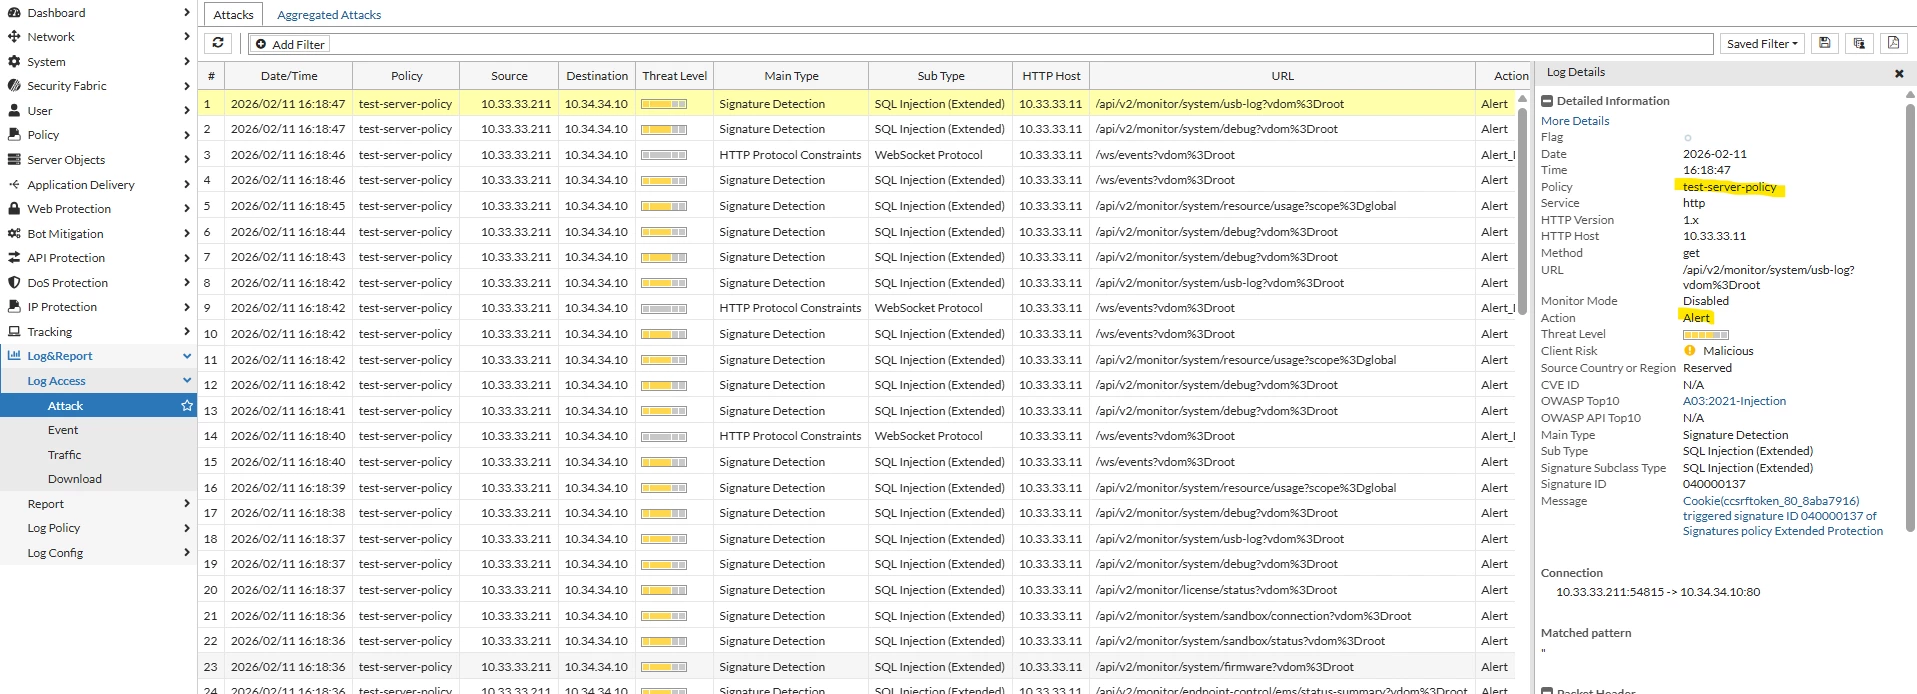
But the same client 10.33.33.211 can still pass through Server Policy 2, where 'alert only' is configured.
 |


