Solution | Prerequisite.
Configure/create an HTTP Header Security Policy:
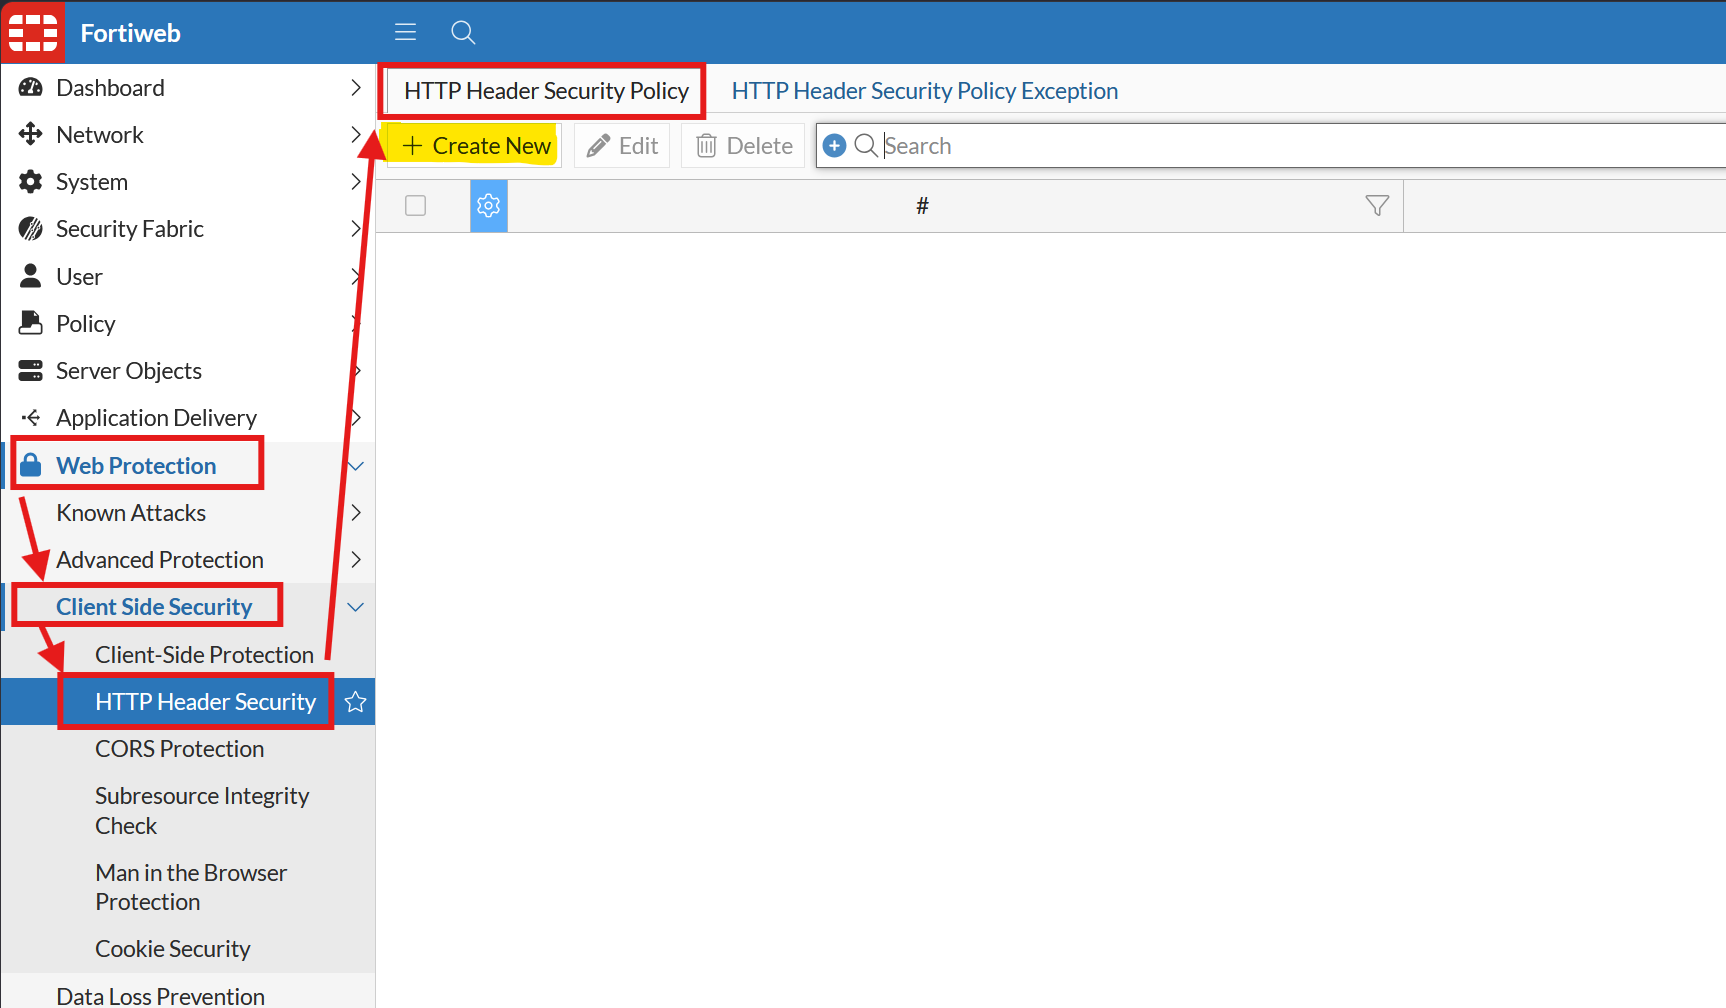
On version 7.x, navigate to Web Protection -> Advanced Protection -> HTTP Header Security -> HTTP Header Security Policy and select + Create New.
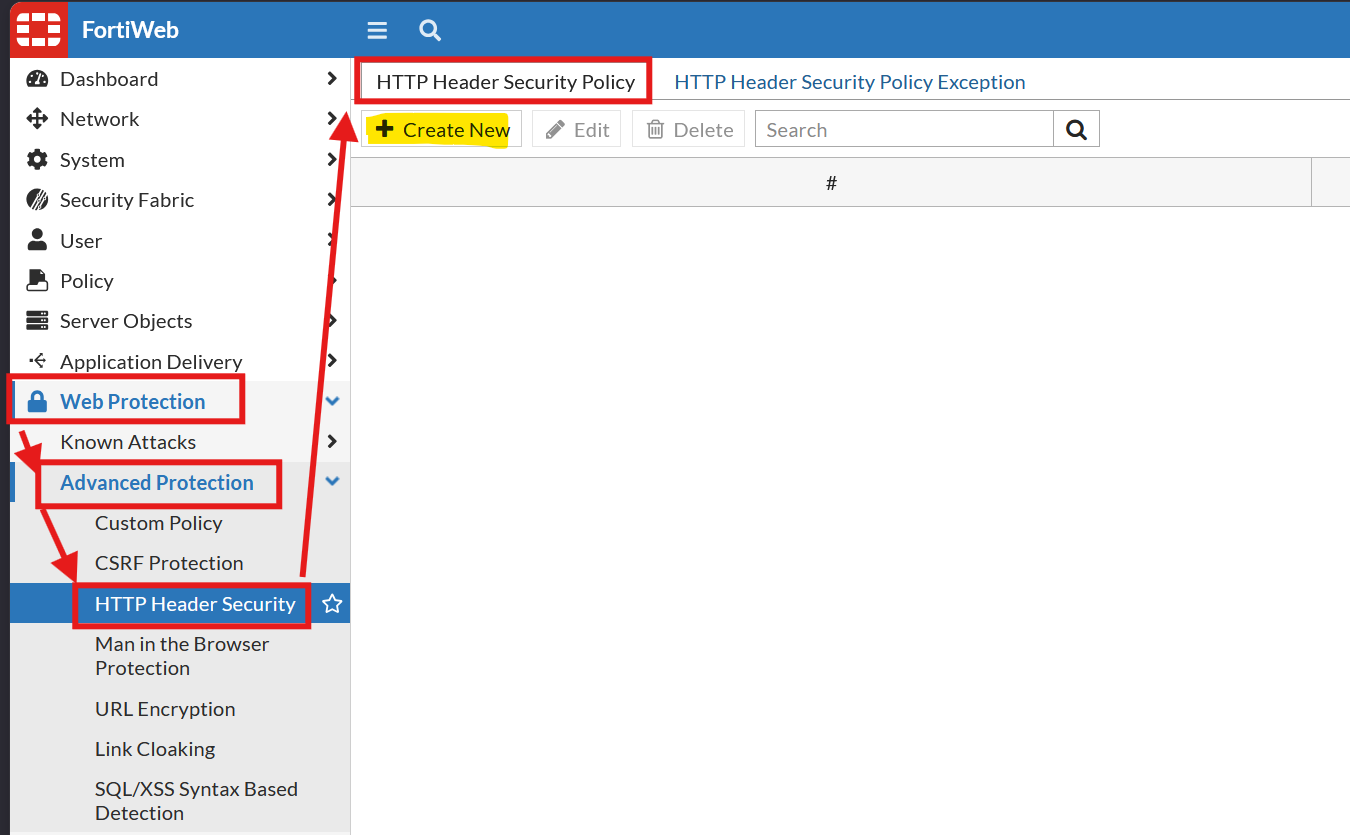
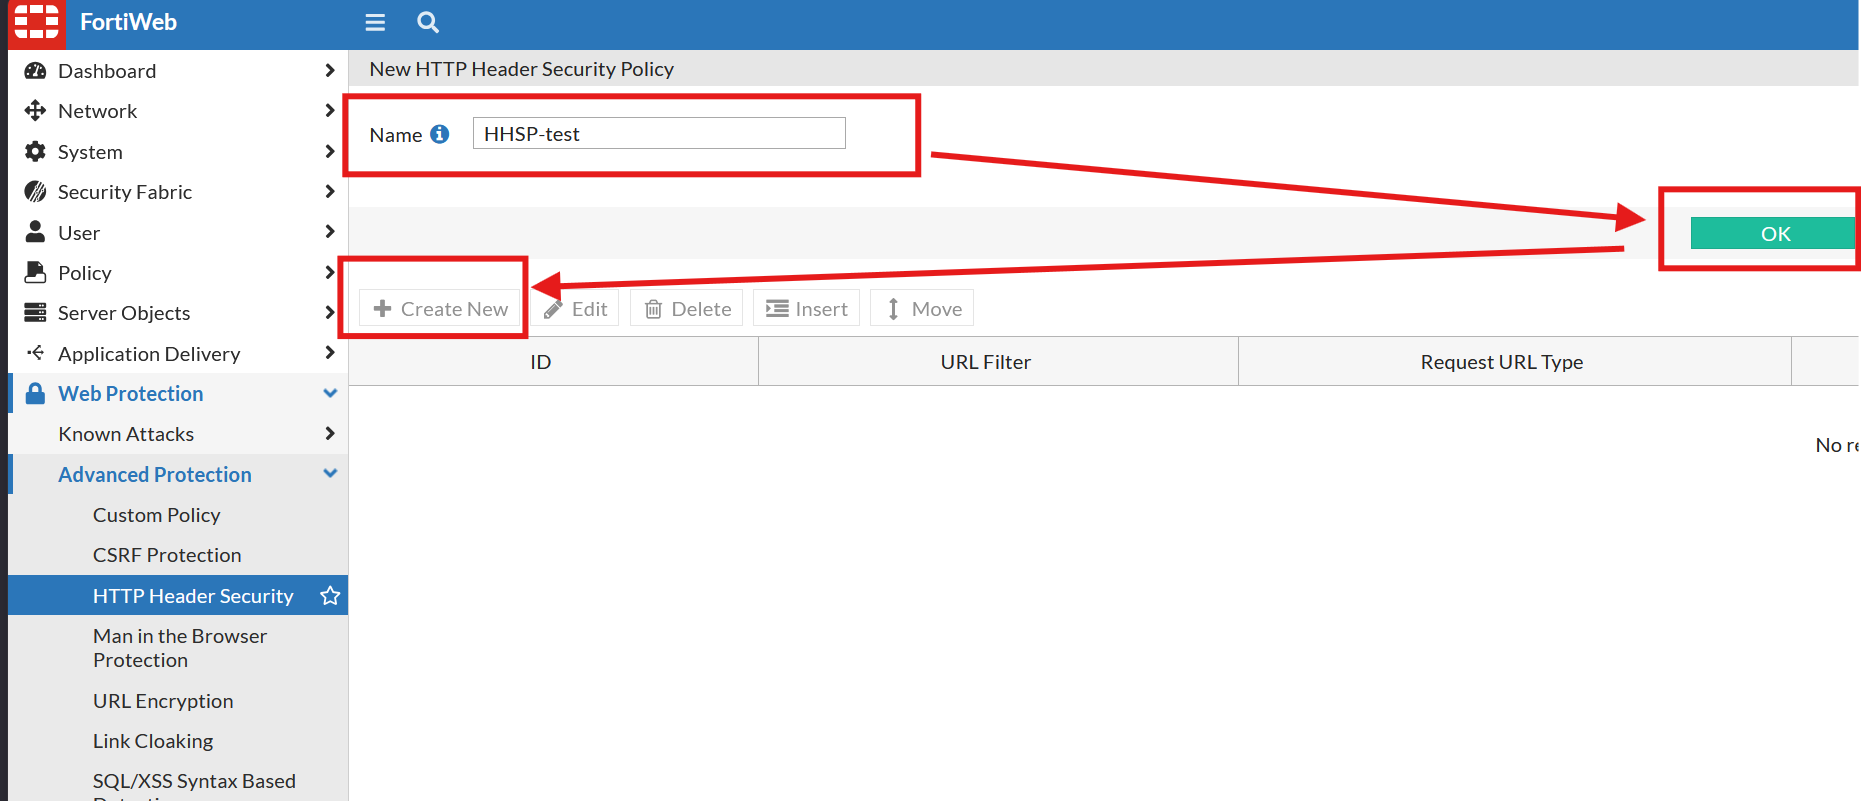
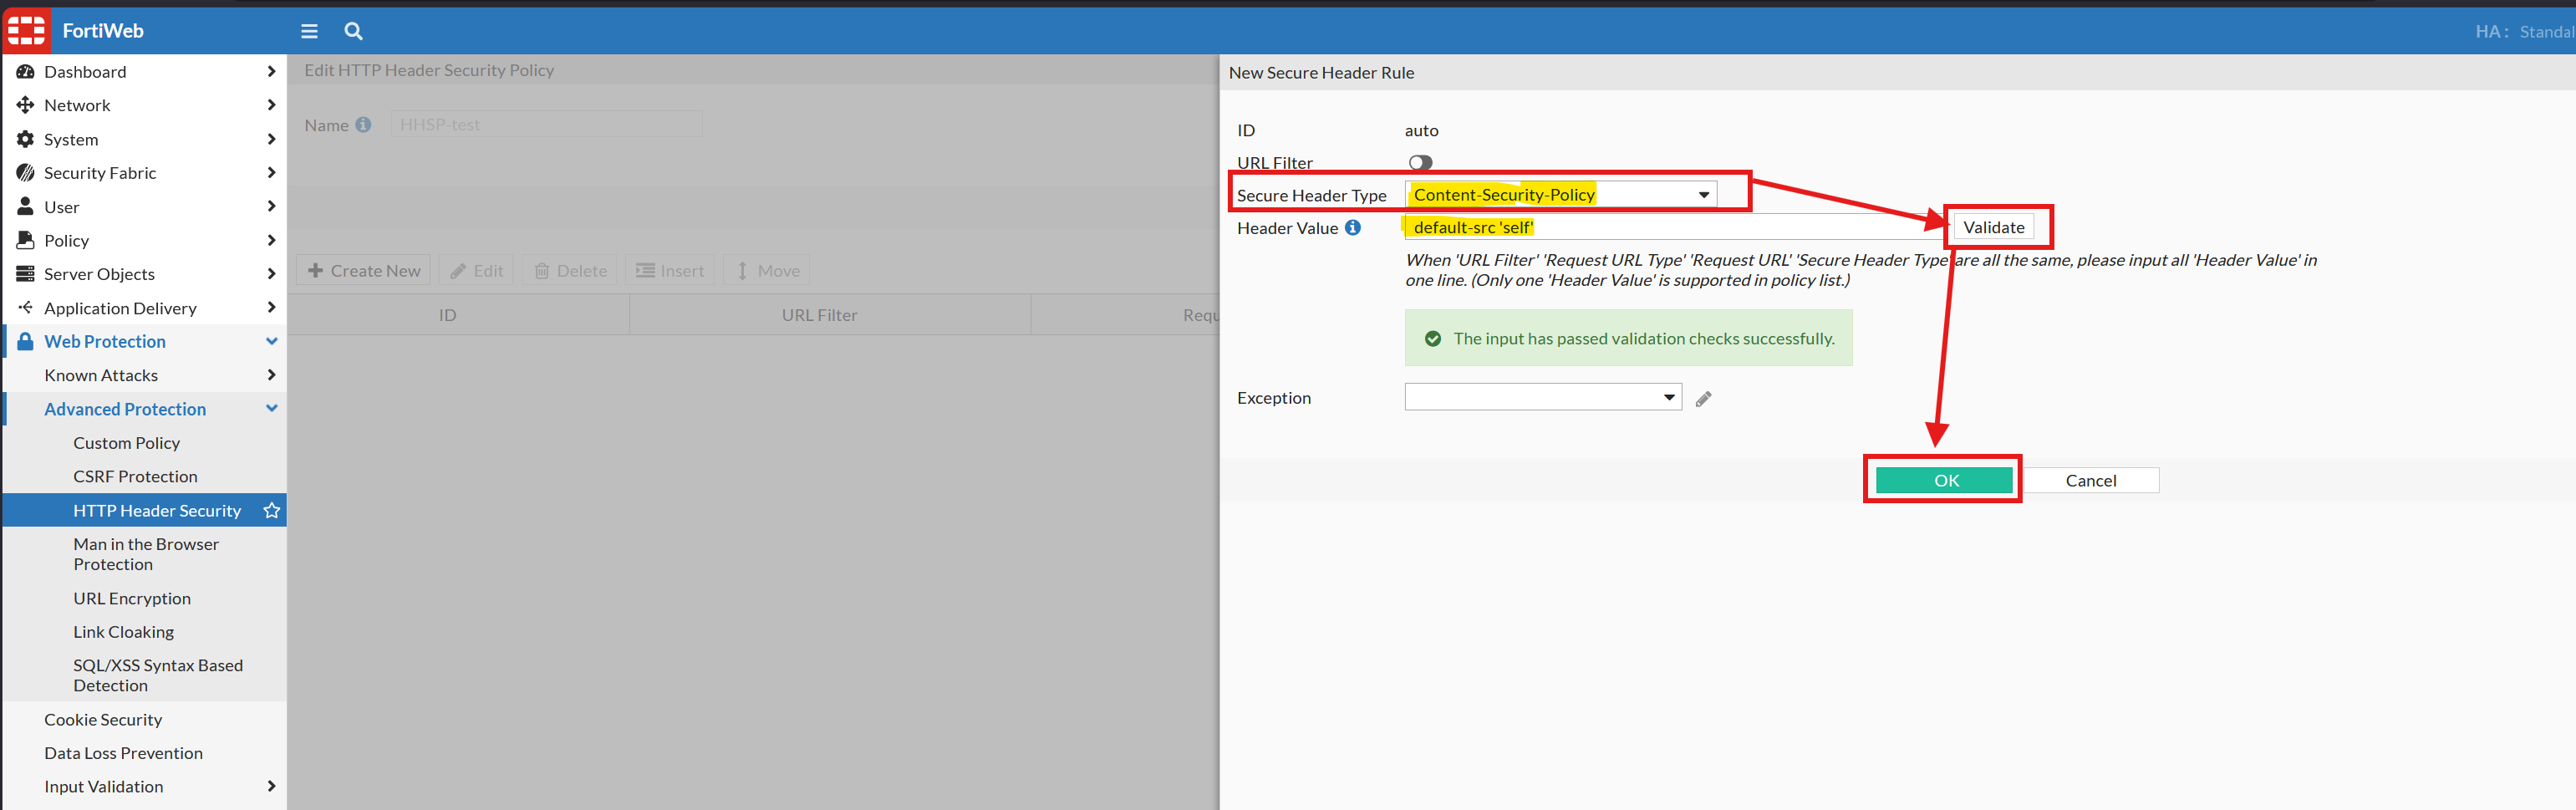
Enter a name for the new HTTP Header Security Policy and select 'OK'. To add a Content Security Policy (CSP) header, select + Create New.
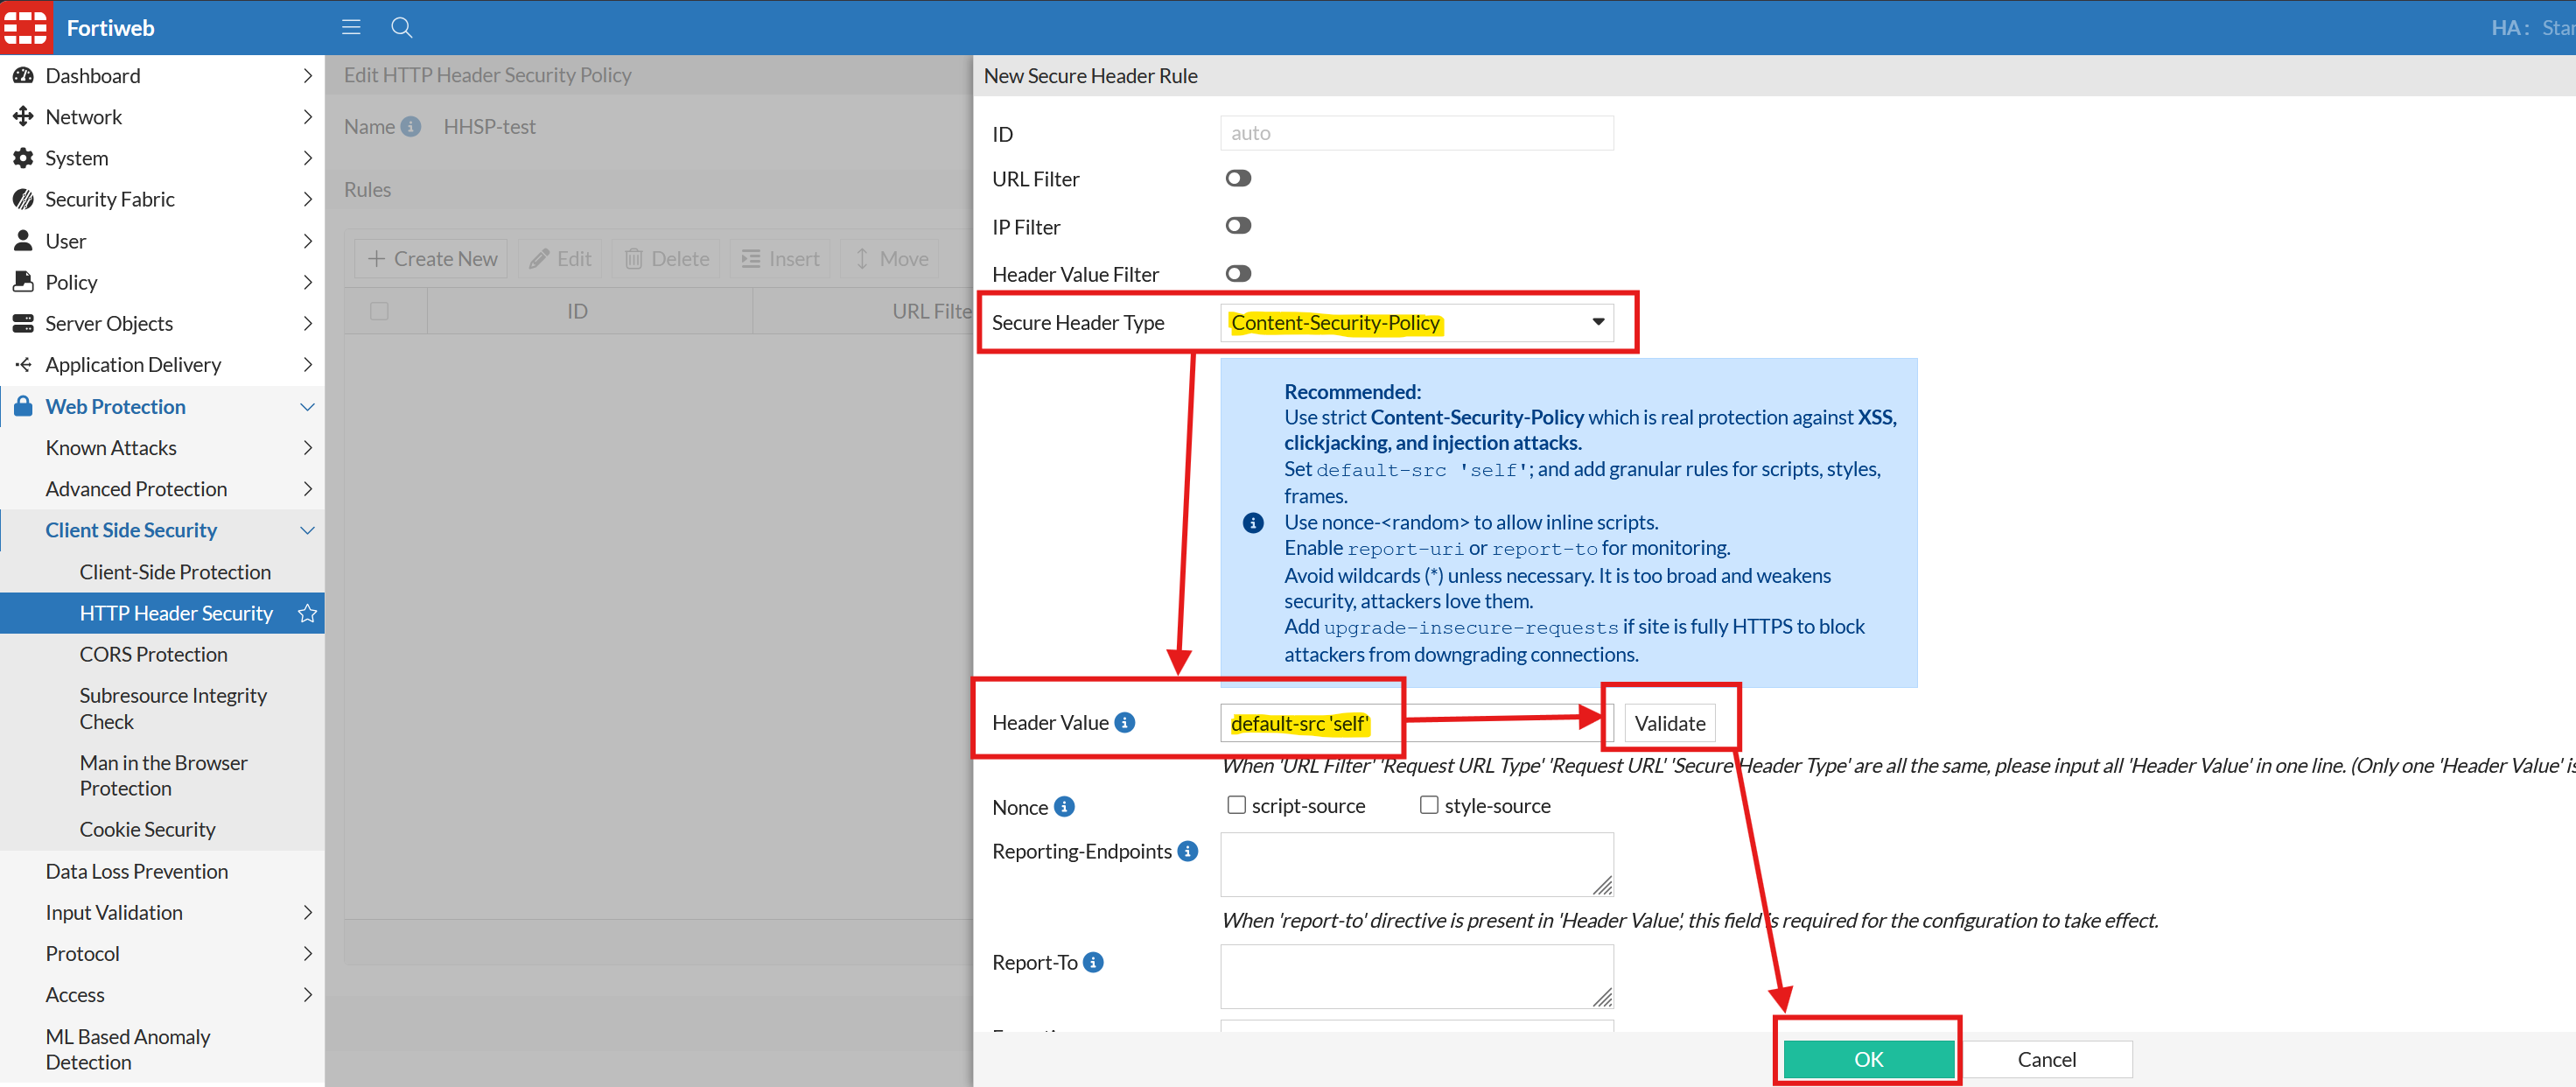
Choose Content-Security-Policy as the header type. Set the header value to 'default-src 'self'; style-src 'self' 'unsafe-inline'; img-src 'self' data:' or another value appropriate to the application's requirements. Select 'Validate' to ensure that the value entered is valid and then Select 'OK'.
The view is different on version 8.x but the settings remain the same:
Assign this new HTTP Header Security Policy with the Content-Security-Policy header to the Web Protection Profile that is applied to the protected web server policy.
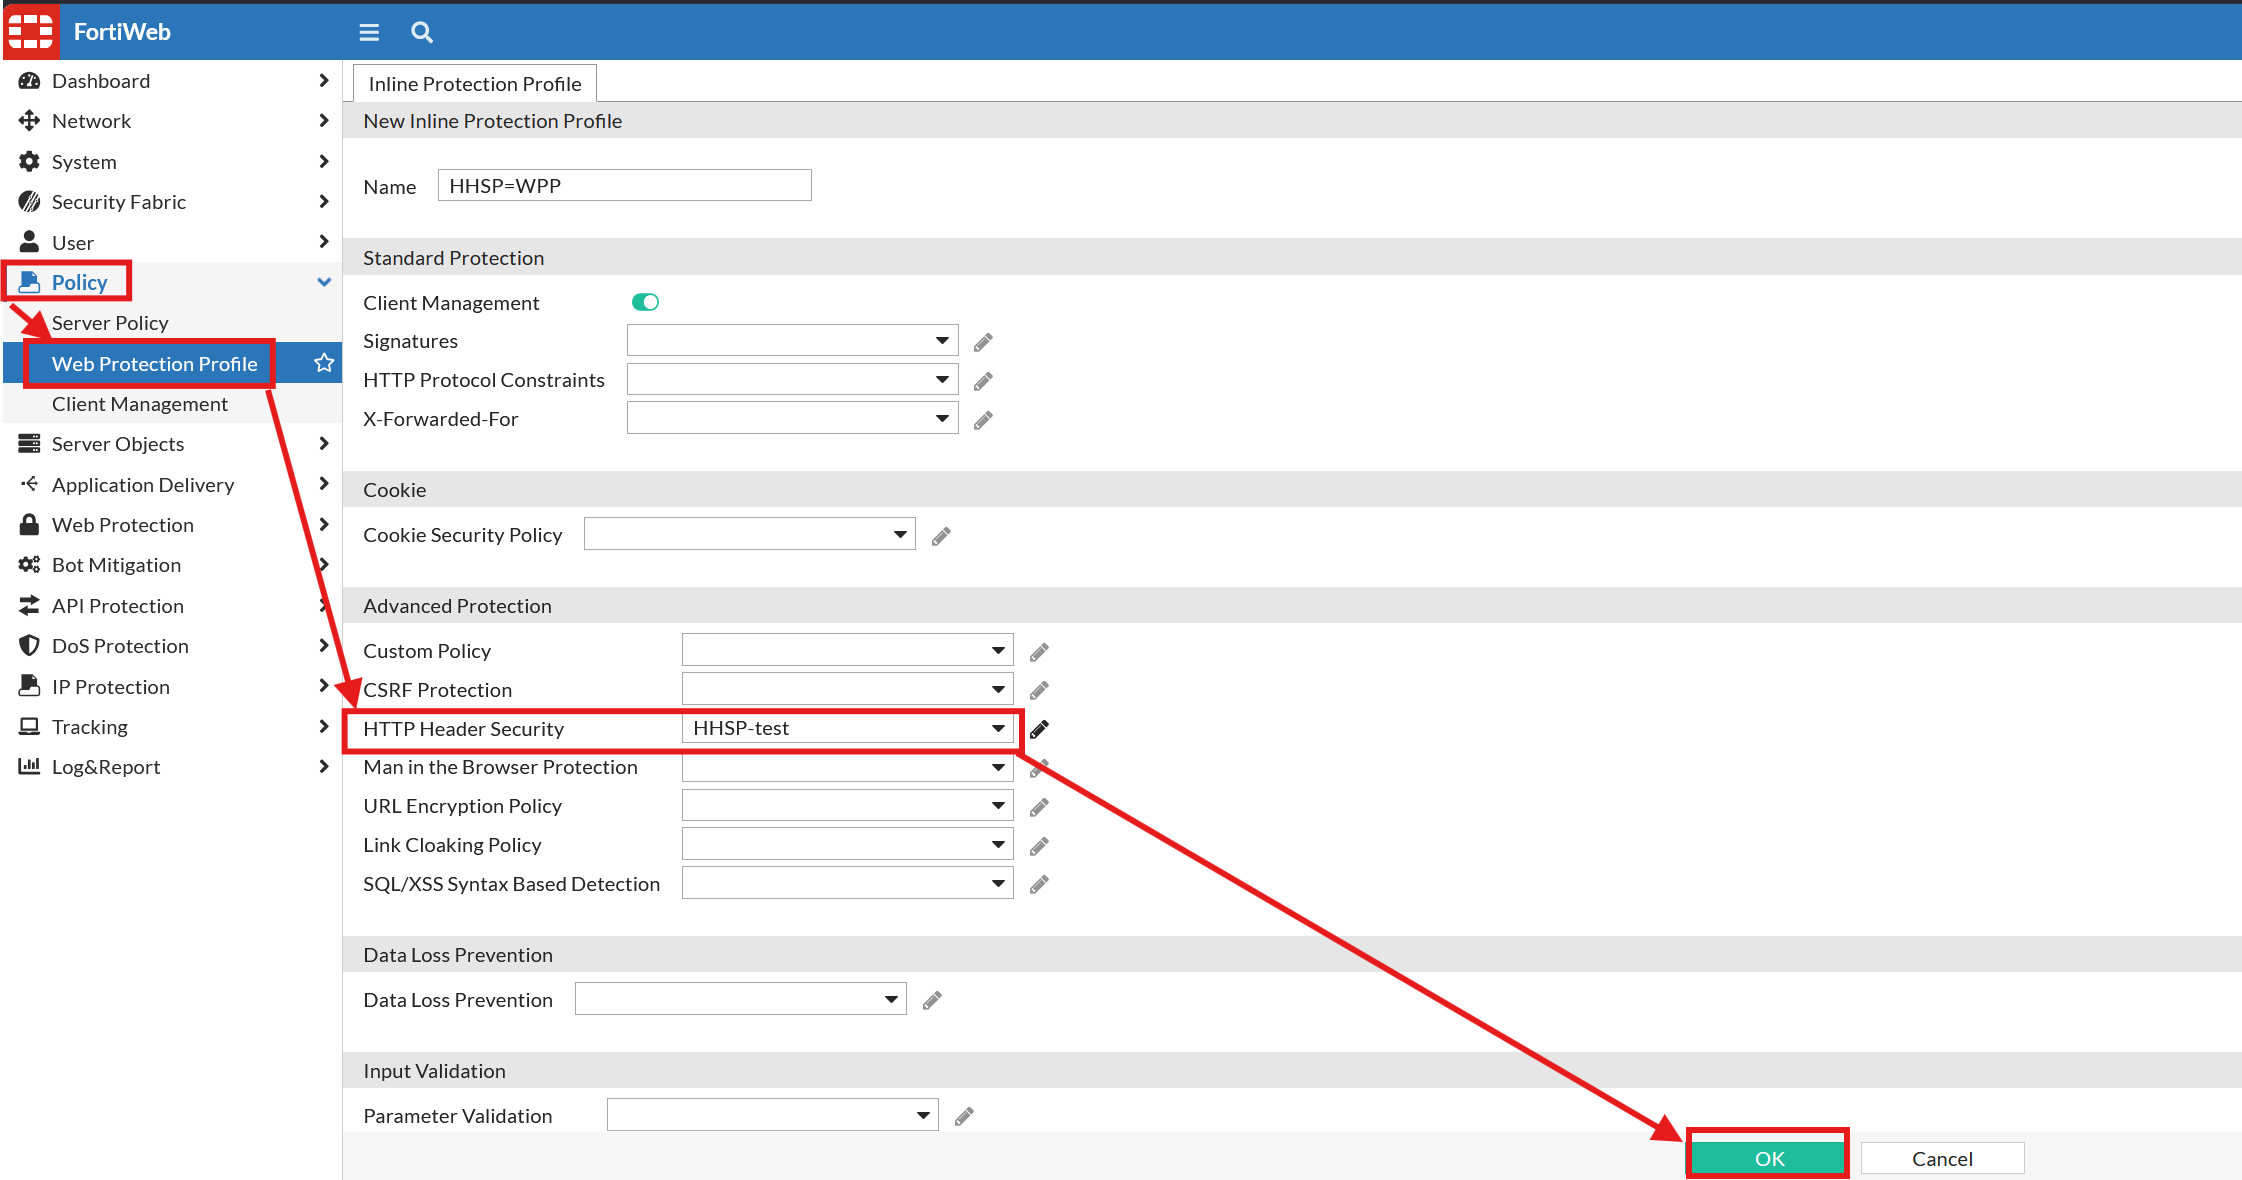
With this configuration, the Content-Security-Policy (CSP) header will be included on both block and allow pages in FortiWeb.
Note: In FortiWeb versions before v7.4.5 and v7.6.1, the CSP header was only applied to allowed traffic and not on block pages.
Related document:
HTTP Security Headers |