



Technical Tip: Blocking CVE-2026-42945 on FortiWeb
Description
This article describes blocking CVE-2026-42945 on FortiWeb.
Scope
FortiWeb.
Solution
For a newly reported endpoint Vulnerability on Fedora nginx CVE-2026-42945, FortiWeb can block this. There are 2 ways to block this vulnerability. Using Custom Signature and Creating an HTTP protocol constraint.
Method 1: Create Custom Signature:
Navigate to Web Protection -> Known Attacks -> Custom Signature -> Create Custom Signature, give it a name, and save it.
After that, create 2 conditions as shown in the image.
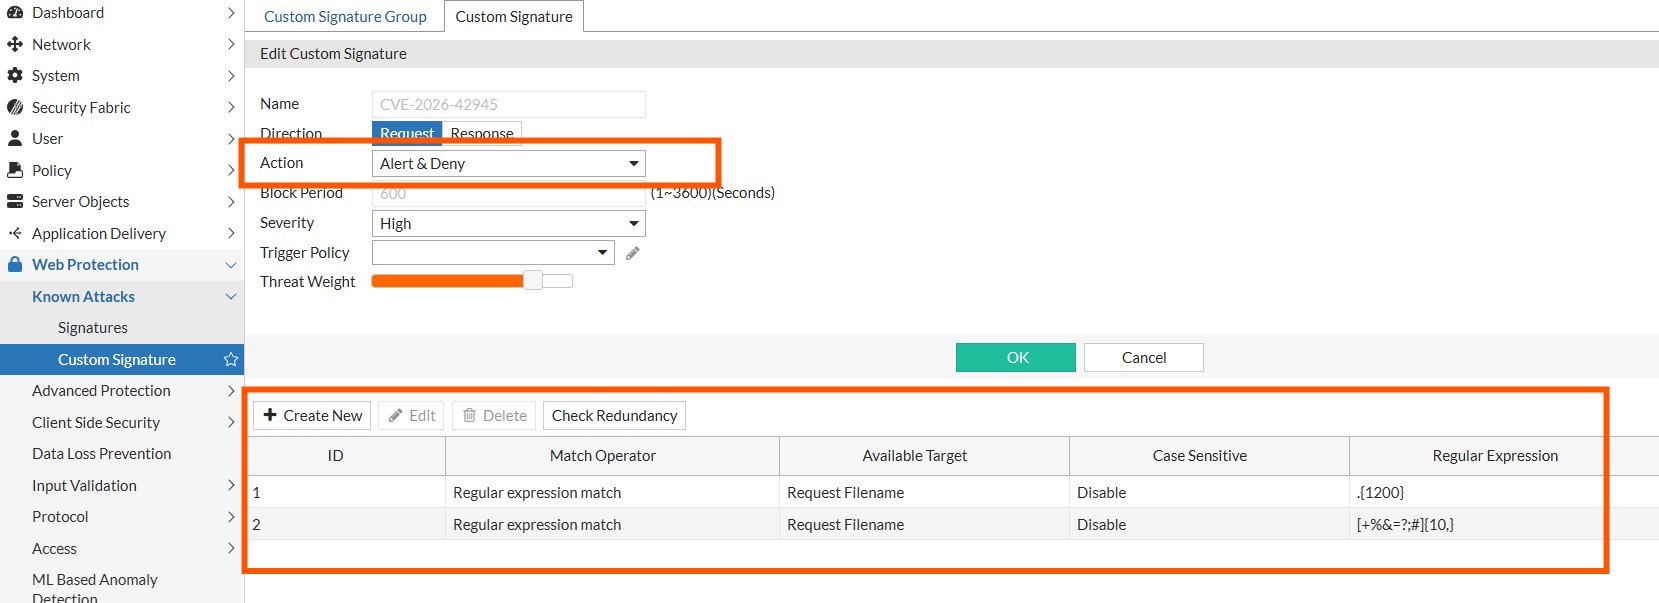
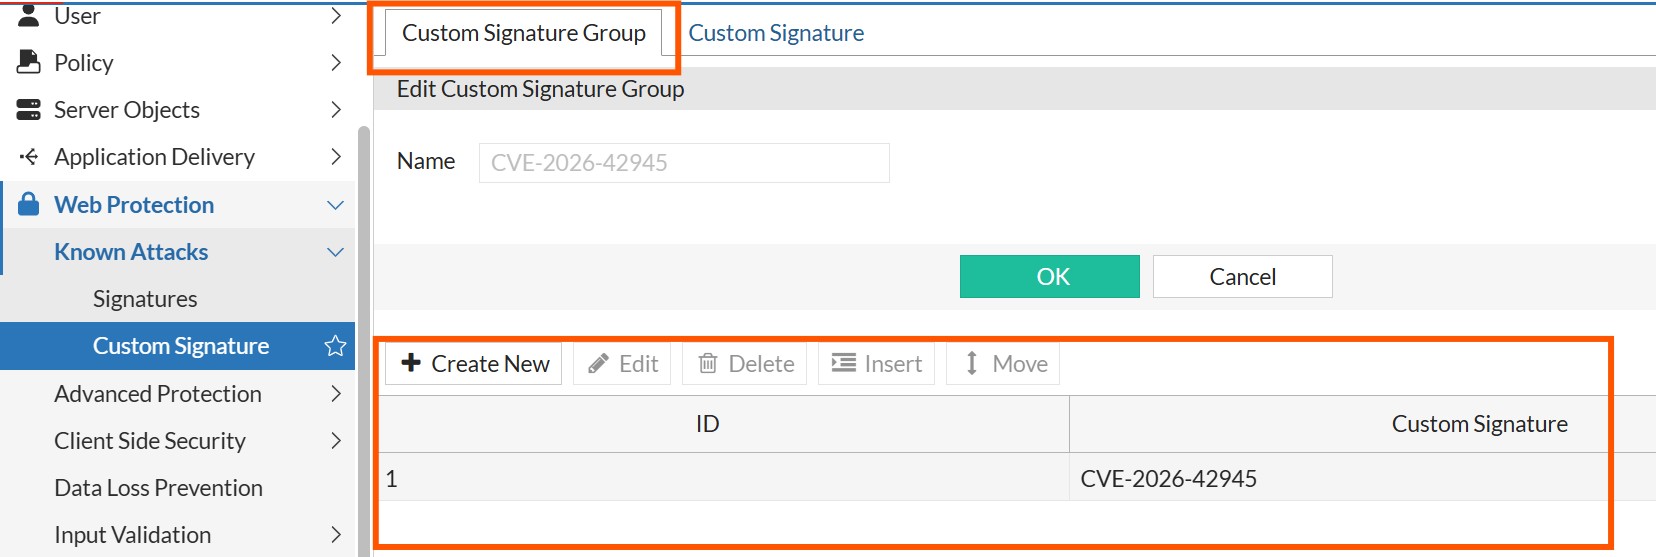
After creating a signature, call that signature in the Custom signature Group and save it.
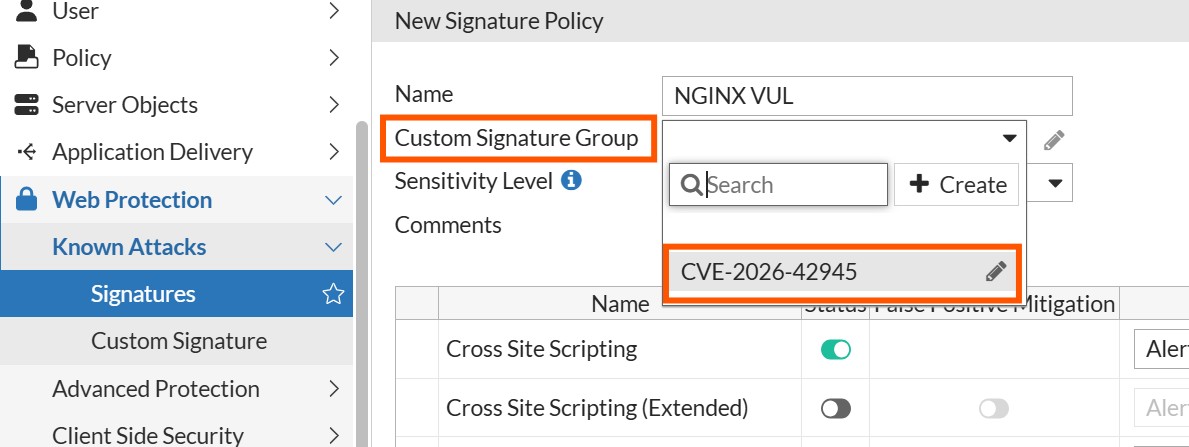
Navigate to Web Protection -> Known Attacks -> Signature -> Create New and call that Custom Signature Group to this User-defined signature.
After that, call the New Signature policy in the Web-Protection profile, which is being used in the server policy hosting the Fedora NGINX.
Method 2: Create an HTTP protocol constraint policy:
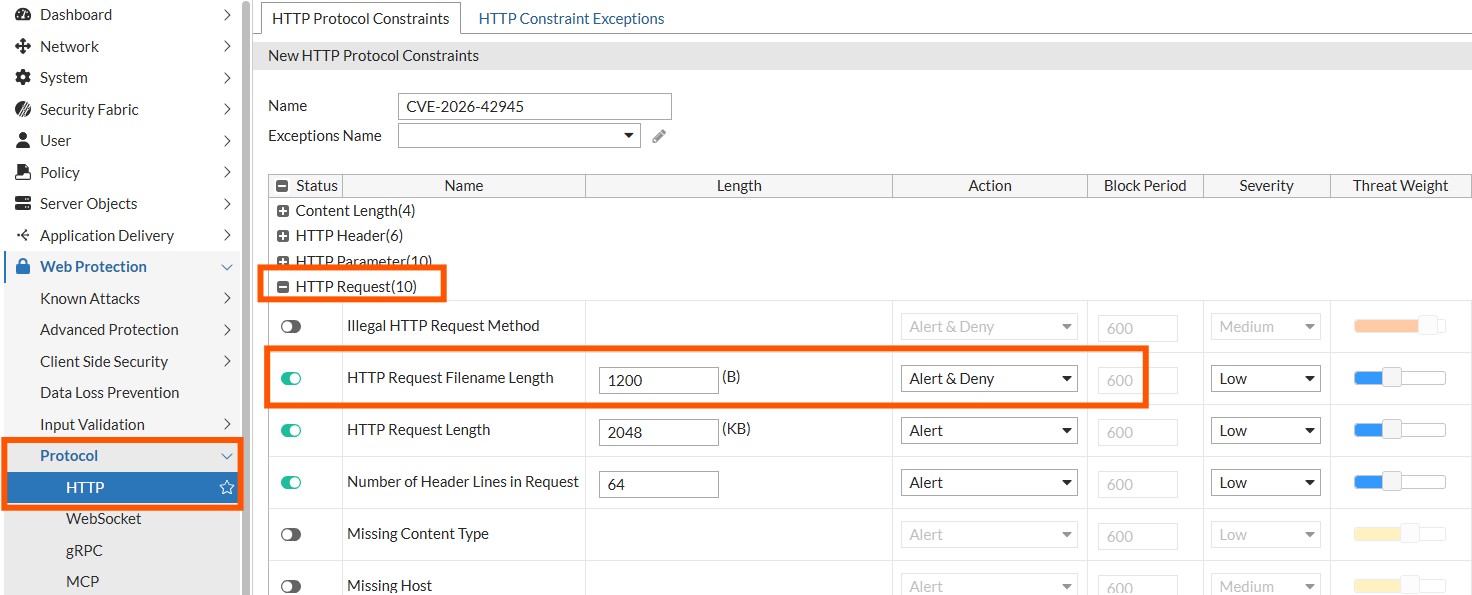
Navigate to Web-Protection -> Protocol -> HTTP -> Create New or Clone the HTTP protocol that is being used.
Navigate to HTTP request field -> HTTP Request Filename Length and set that limit to 1200.
Note: Further Details about this Vulnerability can be found here: Fedora nginx CVE-2026-42945 Buffer Overflow Vulnerability.

