
adecottignies_FTNT
Staff
Staff
January 21, 2025

Technical Tip: Multicast / IGMP behavior with FortiSwitch

Description

This article explains how multicast works within a FortiSwitch without igmp-snooping enabled.

Scope

FortiSwitch.

Solution

To test the Multicast/IGMP traffic, the tool mcjoin will be used.

This is available on GitHub: https://github.com/troglobit/mcjoin


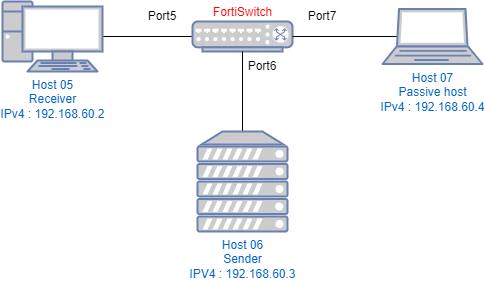
The following architecture has been built in a lab environment:
 

igmp1.png
 

Host05 will act as client/receiver.
Host06 will act as server/sender.
Host07 will act as a client that is not involved in this multicast traffic.

On switch, port5, port6, and port7 have packet-sampler enabled with a rate of 1.

These 3 ports have the same native VLAN (60).


Default behavior: 

Multicast / IGMP on Layer 2 acts like a broadcast.
With a switch configured by default, if a sender is connected, all the multicast packets from this sender will be sent to all the ports of the switch.
This behavior can generate a high number of useless packets and disrupt the traffic.


Case Study:

FortiSwitch with default configuration regarding IGMP.
Host05 will send a report to join the multicast group 225.1.2.3.
Host06 will send multicast traffic to the multicast group 225.1.2.3.
A sniffer will be run on Host07 to analyze if the traffic reaches this host, even if no report has been sent by it.


On Host05:


From the CLI:


mcjoin


By default, mcjoin uses the multicast address 225.1.2.3.

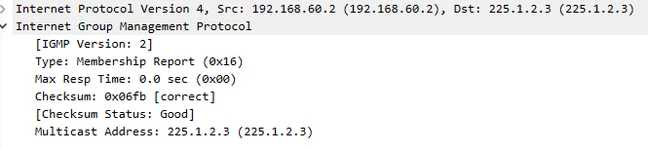
With this, a report is sent by the device to inform that the host wants to join the group 225.1.2.3.

From a sniffer on the switch, it is possible to see this packet:


155.923872 sp5 in 802.1Q vlan#60 P0 -- 192.168.60.2 -> 225.1.2.3:  ip-proto-2 8


Converting to Wireshark:
 

Picture1.png
 

On Host06:


From the CLI:


mcjoin -s -c 10 (-s allows sending the multicast traffic, -c 10 sends 10 packets.)


By default, mcjoin uses the multicast address 225.1.2.3.
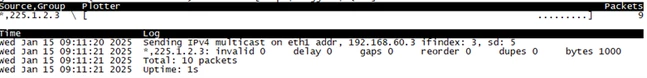
The progress bar at the top right-hand corner will display the number of packets sent.


Picture2.png


On Host05:

The progress bar at the top right-hand corner will display the number of packets sent. As 10 packets have been sent from host06, 10 packets should be received:

 

Picture3.png


On Host07:

Even if the host did not send any report to receive the multicast traffic, this traffic reached host07:


root@host07:/home/fortinet# tcpdump -i eth1 -f "host 225.1.2.3"

tcpdump: verbose output suppressed, use -v[v]... for full protocol decode
listening on eth1, link-type EN10MB (Ethernet), snapshot length 262144 bytes
09:11:21.267722 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:21.368097 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:21.468430 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:21.568797 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:21.669279 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:21.769781 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:21.870067 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:21.970527 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:22.070701 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100
09:11:22.171369 IP 192.168.60.3.51903 > 225.1.2.3.1234: UDP, length 100

This is expected, as it is the normal behavior for a switch without any configuration. The Multicast traffic is sent on all ports, as with broadcast traffic.


Related article: 

Technical Tip: Configure IGMP-snooping on FortiSwitch Managed by FortiGate (FortiLink)

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT


