



Technical Note: FortiSOAR™ Performance Benchmarking for v6.4.4
This document details the performance benchmark tests conducted in Fortinet labs. The performance benchmarking tests were performed on FortiSOAR™ version 6.4.4 Build 3164.
Solution
- Single-node FortiSOAR™ appliance
- Cluster setup of FortiSOAR™
Single Invocation Test for the single-node FortiSOAR™ appliance
Environment
FortiSOAR™ Virtual Appliance Specifications
| Component | Specifications |
| CPU | 8 CPUs |
| Memory | 32 GB |
| Storage | 250 GB virtual disk, with IOPS 2400, attached to an AWS Instance. |
Operating System Specifications
| Operating System | Kernel Version |
| CentOS 7 | 3.10.0-1160.6.1.el7.x86_64 |
External Tools Used
| Tool Name | Version |
| Zabbix | 4.2.1 |
| Internal Script to gather data |
Pre-test conditions on both the standalone FortiSOAR™ machine and the FortiSOAR™ High Availability (HA) cluster
- The test environment contained zero alerts.
- The test environment contained only the FortiSOAR™ built-in connectors such as IMAP, Utilities, etc.
- The system playbooks were deactivated such as, alert assignment notification, sla calculation,etc, and there were no running playbooks.
- The playbook execution logs were purged.
- Configured tunables as follows:
- Changed celery workers to 16
- Elastic heaps size to 8GB
- Increased PostgresSQL Shared memory to 2048MB and worker_mem to 64MB
- Disable playbook priority. To disable playbook priority, edit the /opt/cyops-workflow/sealab/sealab/config.ini file and set the ENABLE PRIORITY parameter to false. Then restart the
uwsgi and celeryd services, using the following command:
# systemctl restart celeryduwsgi
Notes on the tests performed
- The size of the alert data.
Note: For all the above tests, the average size of an alert created in FortiSOAR™ is 5KB. - The number of playbooks that are being executed in parallel for each alert. For example, system playbooks for notification or triage/investigate playbooks.
- The number of steps in each playbook.
- The network bandwidth, especially for outbound connections, to applications such as VirusTotal.
Test setup for the single-node FortiSOAR™ appliance
Tests performed
Test 1: Perform Ingestion in FortiSOAR™ using the FortiSIEM Ingestion Playbook
Description of the Test
Steps followed
- Created the alerts using the FortiSIEM Ingestion playbook. The JSON for the sample playbooks that have been used are attached with this article (Test_1_Info_Json_Files.zip) so that you can run the same tests in your environment to see the performance in your version/hardware platforms. Or, if you want to do some additions that are specific to your environment, you can also tweak the existing playbooks.
- Once the alerts were created, measured the total time taken to create all the alerts in FortiSOAR™.
Observations
The data in the following table outlines the number of alerts ingested and the total time taken to ingest those alerts.
Single Invocation Test run on a single-node FortiSOAR™ appliance
| Number of alerts created in FortiSOAR™ | Total time (in seconds) taken to create all alerts in FortiSOAR™ | Total number of playbooks executed in FortiSOAR™ |
| 1 | 0.32 | 1 |
| 5 | 0.47 | 1 |
| 10 | 0.67 | 1 |
| 25 | 1.69 | 1 |
| 50 | 2.66 | 1 |
| 100 | 6.13 | 1 |
Test 2: Perform Ingestion in FortiSOAR™ using the FortiSIEM Ingestion Playbook and after the alerts are created execute an "Extraction" playbook
Description of the Test
Steps followed
- Created the alerts using the FortiSIEM Ingestion playbook.
- Once the alerts are created, the "Extraction" playbooks are triggered. The JSON for the sample playbooks that have been used are attached with this article (Test_2_Info_Json_Files.zip) so that you can run the same tests in your environment to see the performance in your version/hardware platforms. Or, if you want to do some additions that are specific to your environment, you can also tweak the existing playbooks.
The playbooks perform the following steps: - Declares variables using the "Set Variable Step".
- Updates the existing indicator list using mapping.
- Retrieves indicators from the source data of the alert.
- Creates indicators in the "Indicators" Module.
- Link alerts to the indicators.
- Update Alert State.
Observations
The data in the following table outlines the number of alerts ingested, the total time taken to ingest those alerts, and the total time taken for all the triggered playbooks to complete their execution.
Single Invocation Test run on a single-node FortiSOAR™ appliance
| Number of alerts created in FortiSOAR™ | Total time (in seconds) taken to execute all the playbooks | Total number of playbooks executed in FortiSOAR™ |
| 1 | 1.62 | 2 |
| 5 | 2.71 | 6 |
| 10 | 3.57 | 16 |
| 25 | 6.35 | 37 |
| 50 | 11.40 | 73 |
| 100 | 23.11 | 144 |
Test 3: Perform Ingestion in FortiSOAR™ using the FortiSIEM Ingestion Playbook and after the alerts are created execute "Extraction" and "Enrichment" playbooks
Description of the Test
Important: The setup for this test is exactly the same, however this test additionally requires the "VirusTotal" connector to be configured.
Steps followed
- Created the alerts using the FortiSIEM Ingestion playbook.
- Once the alerts are created, the "Extraction" playbooks are triggered. The JSON for the sample playbooks that have been used are attached with this article (Test_3_Info_Json_Files.zip) so that you can run the same tests in your environment to see the performance in your version/hardware platforms. Or, if you want to do some additions that are specific to your environment, you can also tweak the existing playbooks.
The playbooks perform the following steps:- Declares variables using the "Set Variable Step".
- Updates the existing indicator list using mapping.
- Retrieves indicators from the source data of the alert.
- Creates indicators in the "Indicators" Module.
- Link alerts to the indicators.
- Update Alert State.
- Once the indicators were extracted, the "Enrichment" playbooks are triggered and they perform the following steps: Once the indicators were extracted, the "Enrichment" playbooks are triggered and they perform the following steps:
- Matches the IP in an internal subnet through the "Utilities" subnet.
- Validates whether the IP is Private or Public.
- Performs enrichment using the "Utilities" connector, if the IP is "Private".
Performs enrichment using the "VirusTotal" connector, if the IP is "Public". - Updates the indicator status based on the IP’s vulnerability.
- Updates the state of the indicator State.
Observations
The data in the following table outlines the number of alerts ingested, the total time taken to ingest those alerts, and the total time taken for all the triggered playbooks to complete their execution.
Single Invocation Test run on a single-node FortiSOAR™ appliance
| Number of alerts created in FortiSOAR™ | Total time (in seconds) taken to execute all the playbooks | Total number of playbooks executed in FortiSOAR™ * |
| 1 | 4.93 | 4 |
| 5 | 6.28 | 16 |
| 10 | 11.53 | 31 |
| 25 | 25.87 | 76 |
| 50 | 47.52 | 151 |
| 100 | 1 minute 34 seconds | 301 |
Sustained Invocation Test for the single-node FortiSOAR™ appliance
Description
Results
Graphs
CPU Load Average Utilization Graph
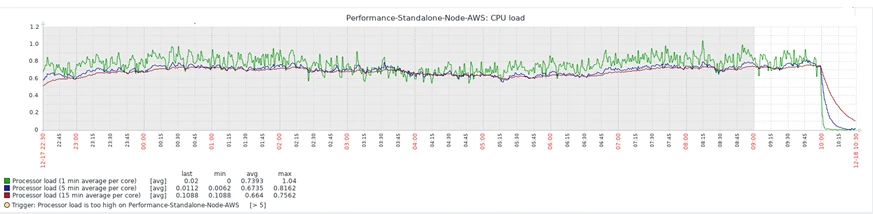
Memory Utilization Graph
Analysis of memory utilization when the test run was in progress on the appliance: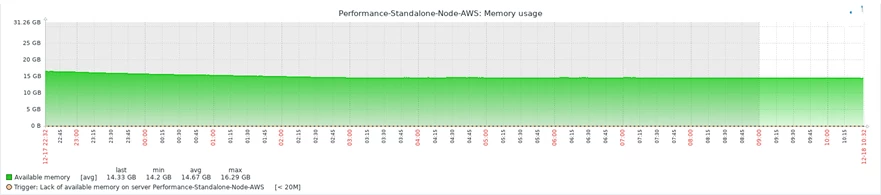
Redis PB Queue Count Graph
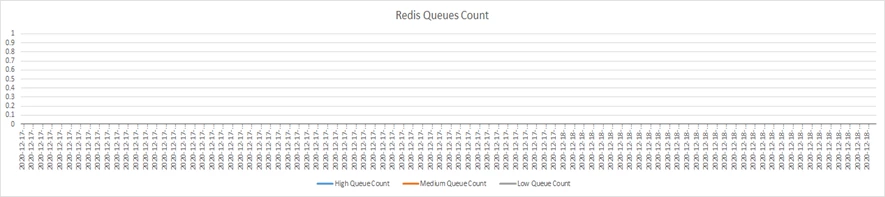
IO Wait Graph
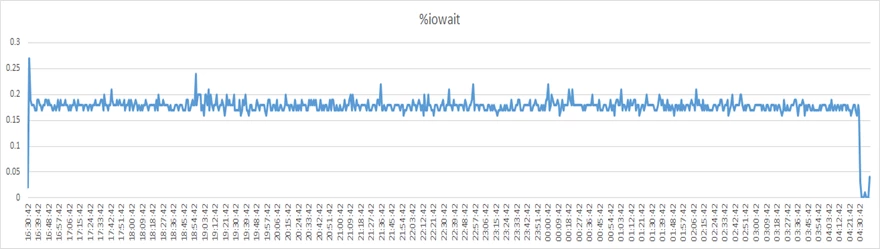
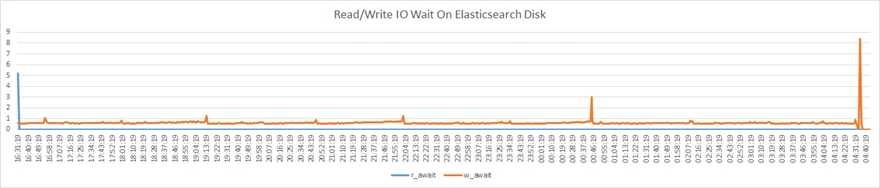
Read/Write IO Wait Graph for ElasticSearch
Read/Write IO Wait Graph for PostgreSQL
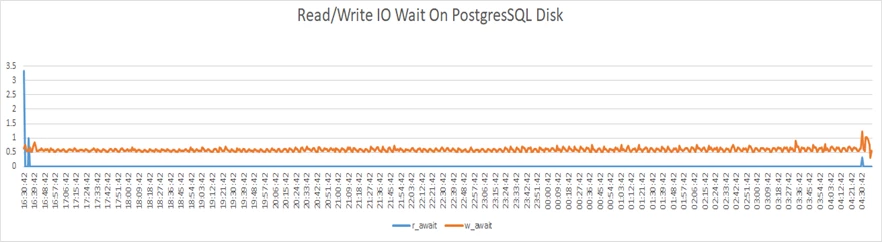
Using the system resources specified in the "Environment" and "Pre-Test Conditions" sections, it was observed that while the "Sustenance Test" was running, the "Read" Wait for the PostgreSQL disk averaged around 1 millisecond, with the maximum wait of 3 milliseconds and the minimum wait of 0 milliseconds. The "Write" Wait for the PostgreSQL disk averaged around 1 millisecond, with the maximum wait of 5.5 milliseconds and the minimum wait of 1 millisecond.
Single Invocation Test for the High Availability (HA) active-active cluster of two FortiSOAR™ nodes
Test setup for the HA active-active cluster of two FortiSOAR™ nodes
- Cluster of two FortiSOAR™ machines that are joined in the Active-Active state using the FortiSOAR™ HA feature
- The machines that form the HA cluster must be in the same network subnet.
Tests performed
Test 1: Perform Ingestion in FortiSOAR™ using the FortiSIEM Ingestion Playbook
Description of the Test
Steps followed
- Created the alerts using the FortiSIEM Ingestion playbook. The JSON for the sample playbooks that have been used are attached with this article (Test_1_Info_Json_Files.zip) so that you can run the same tests in your environment to see the performance in your version/hardware platforms. Or, if you want to do some additions that are specific to your environment, you can also tweak the existing playbooks.
- Once the alerts were created, measured the total time taken to create all the alerts in FortiSOAR™.
Observations
The data in the following table outlines the number of alerts ingested and the total time taken to ingest those alerts.
Single Invocation Test run on a two-node active-active FortiSOAR™ cluster
| Number of alerts created in FortiSOAR™ | Total time (in seconds) taken to create all alerts in FortiSOAR™ | Total number of playbooks executed in FortiSOAR™ |
| 1 | 0.80 | 1 |
| 5 | 0.48 | 1 |
| 10 | 0.70 | 1 |
| 25 | 1.45 | 1 |
| 50 | 2.69 | 1 |
| 100 | 6.36 | 1 |
Test 2: Perform Ingestion in FortiSOAR™ using the FortiSIEM Ingestion Playbook and after the alerts are created execute an "Extraction" playbook
Description of the Test
Steps followed
- Created the alerts using the FortiSIEM Ingestion playbook.
- Once the alerts are created, the "Extraction" playbooks are triggered. The JSON for the sample playbooks that have been used are attached with this article (Test_2_Info_Json_Files.zip) so that you can run the same tests in your environment to see the performance in your version/hardware platforms. Or, if you want to do some additions that are specific to your environment, you can also tweak the existing playbooks.
The playbooks perform the following steps: - Declares variables using the "Set Variable Step".
- Updates the existing indicator list using mapping.
- Retrieves indicators from the source data of the alert.
- Creates indicators in the "Indicators" Module.
- Link alerts to the indicators.
- Update Alert State.
Observations
The data in the following table outlines the number of alerts ingested, the total time taken to ingest those alerts, and the total time taken for all the triggered playbooks to complete their execution.
Single Invocation Test run on a two-node active-active FortiSOAR™ cluster
| Number of alerts created in FortiSOAR™ | Total time (in seconds) taken to execute all the playbooks | Total number of playbooks executed in FortiSOAR™ |
| 1 | 3.41 | 2 |
| 5 | 2.38 | 6 |
| 10 | 3.23 | 16 |
| 25 | 5.79 | 37 |
| 50 | 10.80 | 73 |
| 100 | 20.70 | 144 |
Test 3: Perform Ingestion in FortiSOAR™ using the FortiSIEM Ingestion Playbook and after the alerts are created execute "Extraction" and "Enrichment" playbooks
Description of the Test
Important: The setup for this test is exactly the same, however this test additionally requires the "VirusTotal" connector to be configured.
Steps followed
- Created the alerts using the FortiSIEM Ingestion playbook.
- Once the alerts are created, the "Extraction" playbooks are triggeredThe JSON for the sample playbooks that have been used are attached with this article (Test_2_Info_Json_Files.zip) so that you can run the same tests in your environment to see the performance in your version/hardware platforms. Or, if you want to do some additions that are specific to your environment, you can also tweak the existing playbooks.
The playbooks perform the following steps:- Declares variables using the "Set Variable Step".
- Updates the existing indicator list using mapping.
- Retrieves indicators from the source data of the alert.
- Creates indicators in the "Indicators" Module.
- Link alerts to the indicators.
- Update Alert State.
- Once the indicators were extracted, the "Enrichment" playbooks are triggered and they perform the following steps:
- Matches the IP in an internal subnet through the "Utilities" subnet.
- Validates whether the IP is Private or Public.
- Performs enrichment using the "Utilities" connector, if the IP is "Private".
- Performs enrichment using the "VirusTotal" connector, if the IP is "Public".
- Updates the indicator status based on the IP’s vulnerability.
- Updates the state of the indicator State.
Observations
The data in the following table outlines the number of alerts ingested, the total time taken to ingest those alerts, and the total time taken for all the triggered playbooks to complete their execution.
Single Invocation Test run on a two-node active-active FortiSOAR™ cluster
| Number of alerts created in FortiSOAR™ | Total time (in seconds) taken to execute all the playbooks | Total number of playbooks executed in FortiSOAR™ |
| 1 | 5.39 | 4 |
| 5 | 6.46 | 16 |
| 10 | 8.59 | 31 |
| 25 | 19.44 | 76 |
| 50 | 35.66 | 151 |
| 100 | 1 minute 6 seconds | 301 |
Sustained Invocation Test for the HA active-active cluster of two FortiSOAR™ nodes
Description
Results
Graphs
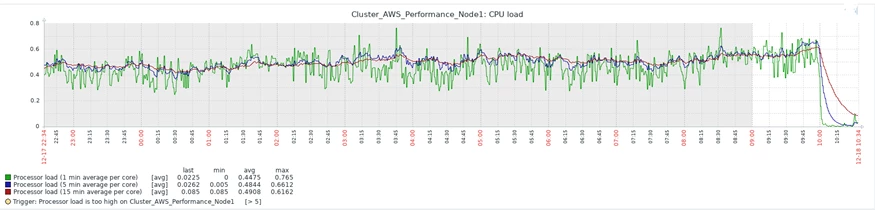
CPU Load Average Utilization Graph
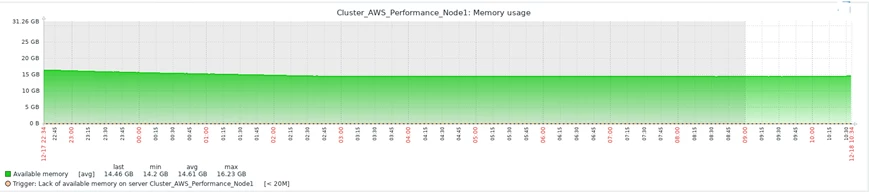
Memory Utilization Graph
Redis PB Queue Count Graph
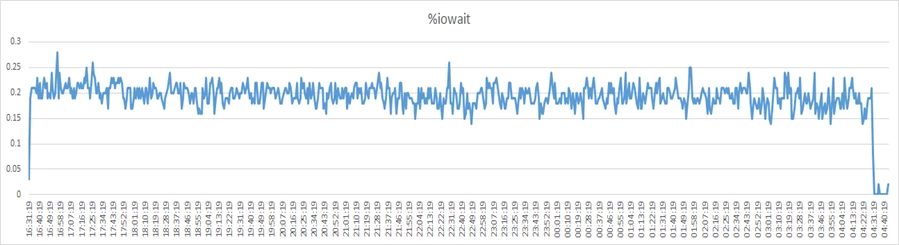
IO Wait Graph
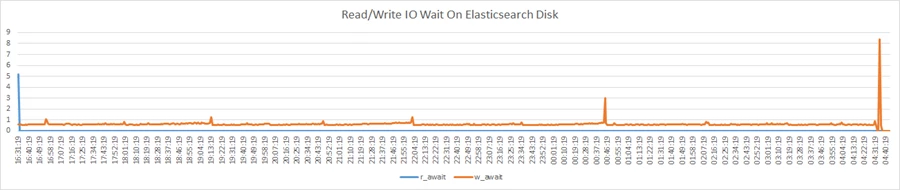
Read/Write IO Wait Graph for ElasticSearch
Read/Write IO Wait Graph for PostgreSQL
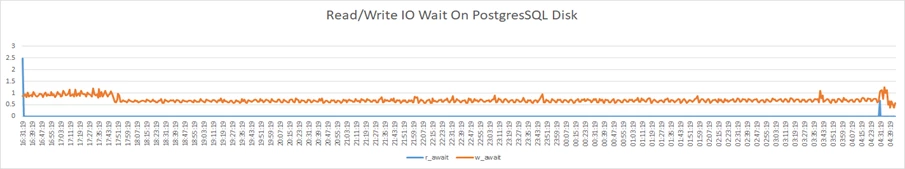
Using the system resources specified in the "Environment" and "Pre-Test Conditions" sections, it was observed that while the "Sustenance Test" was running, the "Read" Wait for the PostgreSQL disk averaged around 0 millisecond. The "Write" Wait for the PostgreSQL disk averaged around 8 milliseconds, with the maximum wait of 25 milliseconds and the minimum wait of 1 millisecond.

