


Troubleshooting Tip: FortiSIEM Windows Agent consumes high CPU/Memory on Windows server
Description
This article describes how to investigate if FortiSIEM Windows Agent spikes high CPU utilization on Windows servers.
Scope
Windows Agent v4.4.x, v5.x, v7.x.x, v7.1.x, v7.2.x,v7.3.x,v7.4.x,v7.5.x. Supervisor and Collector v6.x, v7.x, v7.1.x, v7.2.x, v7.3.x, v7.4.x, v7.5.x.
Solution
- Verify if high utilization is caused by the FortiSIEM Agent by checking the CPU and Memory Utilization of the FSMLogAgent process on the Windows server Task Manager.
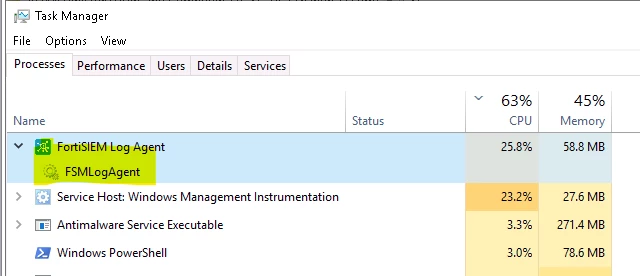
FortiSIEM Agents are designed to be lightweight and not consume more than 5% of a system's CPU and memory.
-
Ensure that the system has met the prerequisites defined in the Windows Agent Installation Guide and FortiSIEM Version Compatibility Matrix as per the installed agent version.
-
On the Windows server, navigate to Windows Event Viewer -> Application, System, and Security logs. Check if any event is generated by the Windows OS. These events are triggered based on the Local Security Policy settings (Control Panel -> System and Security -> Windows Tools). Note that it is possible these settings are managed vía GPO by Windows Server administrators.
-
On the Windows server, navigate to Windows Event Viewer -> Application, System, and Security logs. Assess for any unusually high number of events. In this case, fine-tune the system audit policies and analyze what is triggering such a high event rate.
-
Investigate from the FortiSIEM Analytics tab to find out which event type has the maximum count.
Run a historical search for 10 minutes or 1 hour:
Filters: Reporting IP = <Windows-IP> AND System Event Category BETWEEN 0,6
Display conditions: Reporting IP , Event Name , Count(Matched Events)
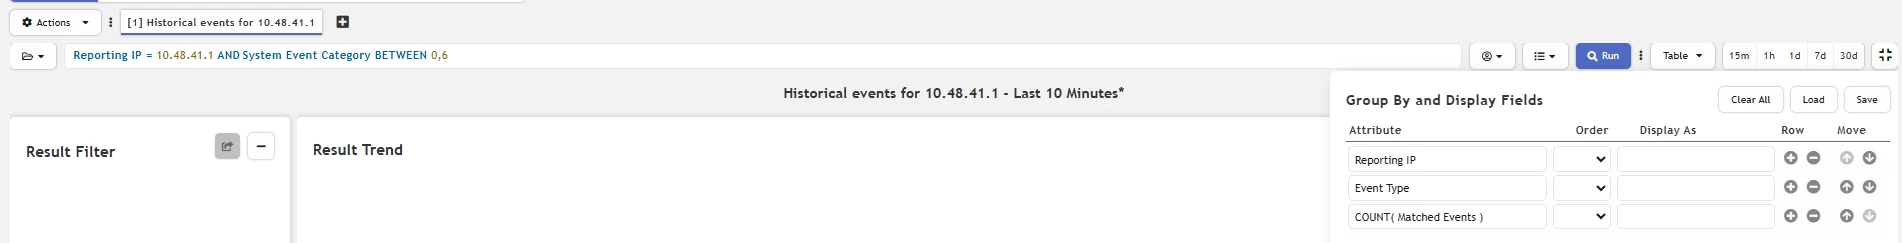
Export a 10-60-minute duration report and review.
-
Temporarily exclude the high event type eventID from the Windows Agent Template and click Apply on Template, to observe if system utilization has restored to normal. Later, evaluate if the event is still required in FortiSIEM or can be reduced on the Windows server.
-
Probe for any errors in Agent logs from the Windows server located in:
C:\ProgramData\FortiSIEM\Agent\Logs\FSMLogAgent.log
C:\ProgramData\FortiSIEM\Agent\Logs\Trace.log
C:\Program Files\Fortinet\FortiSIEM\logs\cms.log
-
Probe for any errors in FortiSIEM collector logs, phAgentManager process:
cat /opt/phoenix/log/phoenix.log | grep -i phAgentManager
-
Inspect the network connectivity between the Windows server and the collector for any latency.
-
Verify if large events are cached on the Windows server. The cache for the Windows agent is stored in the following directory:
C:\ProgramData\AccelOps\Agent\Database\AoWinAgt.db
-
For Windows Agent v5.0.0 or later, ensure the following are whitelisted in antivirus software, or it may result in high CPU and memory usage, and can significantly slow down the machine.
c:\Program Files\Fortinet\FortiSIEM\certs.pem
c:\Program Files\Fortinet\FortiSIEM\cn.bat
c:\Program Files\Fortinet\FortiSIEM\fins.xml
c:\Program Files\Fortinet\FortiSIEM\FortiSIEM.Common.dll
c:\Program Files\Fortinet\FortiSIEM\FortiSIEM.Security.dll
c:\Program Files\Fortinet\FortiSIEM\FortiSIEM.Utilities.dll
c:\Program Files\Fortinet\FortiSIEM\FortiSIEM.Utilities.manifest
c:\Program Files\Fortinet\FortiSIEM\FortiSIEM.WebProxy.dll
c:\Program Files\Fortinet\FortiSIEM\FortiSIEM.WebProxy.manifest
c:\Program Files\Fortinet\FortiSIEM\FortiSIEM.WinRTWrapper.dll
c:\Program Files\Fortinet\FortiSIEM\FSMLogAgent.exe
c:\Program Files\Fortinet\FortiSIEM\FSMLogAgent.exe.config
c:\Program Files\Fortinet\FortiSIEM\License_3rd_party.txt
c:\Program Files\Fortinet\FortiSIEM\log4net.config
c:\Program Files\Fortinet\FortiSIEM\log4net.dll
c:\Program Files\Fortinet\FortiSIEM\monitorStatus.xml
c:\Program Files\Fortinet\FortiSIEM\osquery.exe
c:\Program Files\Fortinet\FortiSIEM\data\*
c:\Program Files\Fortinet\FortiSIEM\logs\*
c:\ProgramData\FortiSIEM\Database\*
c:\ProgramData\FortiSIEM\Logs\*
c:\Windows\System32\drivers\FortiInsight.sys
If the issue persists, contact Fortinet Support (Support) with all of the above details.


