



Technical Tip: Syslog over TLS from FortiAnalyzer/FortiManager to FortiSIEM
Description
This article describes how to configure syslog over TLS from FortiAnalyzer or FortiManager to FortiSIEM.
Scope
FortiSIEM, FortiAnalyzer, FortiManager.
Solution
Generate CA key in FortiSIEM.
openssl genrsa -out <CA key name> 2048
Example: openssl genrsa -out ca.key 2048.
Generate client key in FortiSIEM.
openssl genrsa -out <Client key name> 2048
Example: openssl genrsa -out client.key 2048.
Generate CA cert (Change the -subj to user country, location, and CN name).
openssl req -x509 -new -nodes -key <CA key generated in Step 1> -sha256 -days 3650 -out <CA cert name> -subj /C=<Country>/ST=<State>/L=<Location>/O=<Organization>/CN=<CA cert CN name>
Example: openssl req -x509 -new -nodes -key ca.key -sha256 -days 3650 -out ca.cert.pem -subj /C=AU/ST=QLD/L=Brisbane/O=IT/CN=FortiSIEMCA.
Generate CSR with client key (Change the -subj to user country, location, and CN name).
openssl req -new -sha256 -key <Client key name in Step2> -subj /C=<Country>/ST=<State>/L=<Location>/O=<Organization>/CN=<CSR cert CN name> -out <CSR name>
Example: openssl req -new -sha256 -key client.key -subj /C=AU/ST=QLD/L=Brisbane/O=IT/CN=FortiSIEM -out Collector.csr
Sign the CSR using CA cert and key:
openssl x509 -req -in <CSR generated in Step 4> -CA <CA cert generated in Step 3> -CAkey <CA key generated in Step 1> -CAcreateserial -out <Certificate Name> -days 365 -sha256
Example: openssl x509 -req -in collector-8.csr -CA ca.cert.pem -CAkey ca.key -CAcreateserial -out Collector.crt -days 365 -sha256
Move the new cert and key generated in Step 5 and Step 2 into the path below:
# cp Collector.crt /etc/pki/tls/certs/
# cp client.key /etc/pki/tls/private/
Edit FortiSIEM config to use the correct client cert and key:
# vi /opt/phoenix/config/phoenix_config.txtLine 596 # Already preserved
Line 597 tls_certificate_file=/etc/pki/tls/certs/Collector.crt
Line 598 # Already preserved
Line 599 tls_key_file=/etc/pki/tls/private/client.keyRestart the correct FortiSIEM service:
# killall -9 phParserIn the FortiAnalyzer/FortiManager -> Certificates -> Create New/Import -> CA certificate -> Import CA Certificate from Step 3:
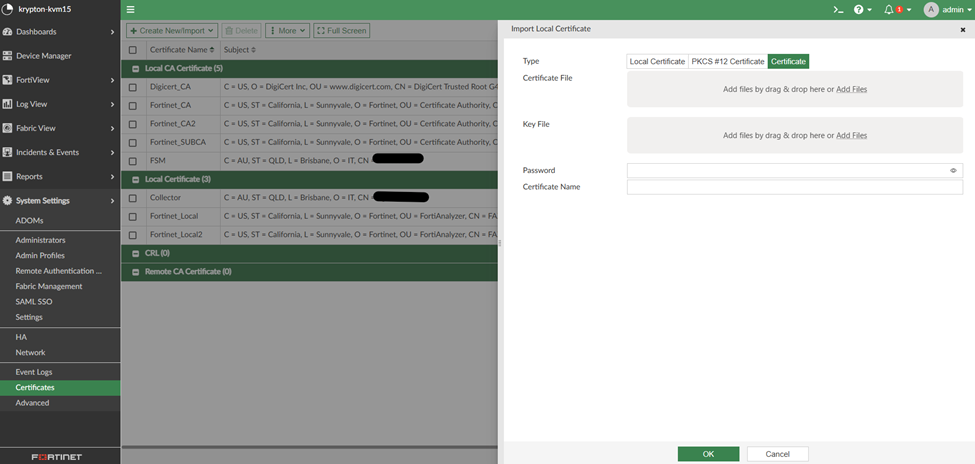
In the FortiAnalyzer/FortiManager -> Certificates -> Create New/Import -> Certificate -> Certificate -> Import Certificate and key generated in Steps 2 and 5.
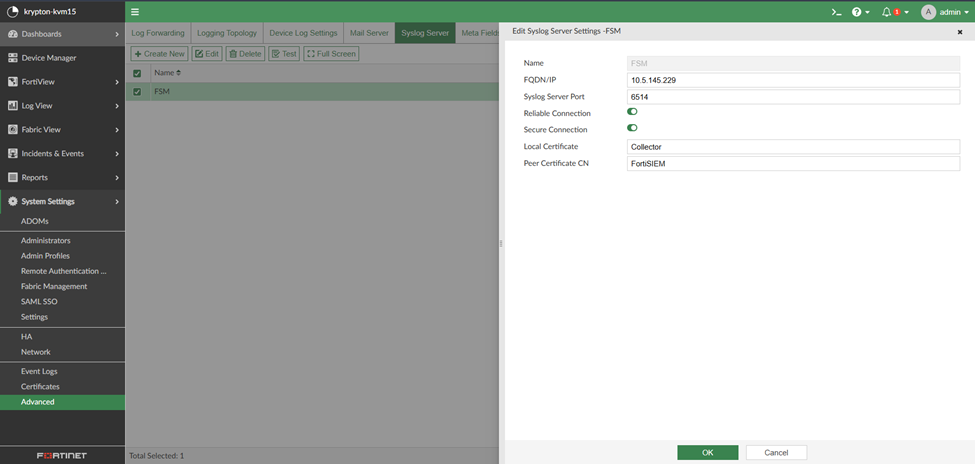
Go to FortiAnalyzer -> Advanced -> Syslog -> Configure as below:
Local Certificate = <Certificate name configured in Step 10>.
Peer Certificate CN = <CN configured in Step 4>.
After finishing configuring in FortiAnalyzer/FortiManager, test the syslog and make sure it is successful.
Notes:
If syslog failed, packet capture in FortiSIEM at port 6514 for more information:
tshark -f "dst port 6514"
Related documents:
Technical Tip: Log forwarding to rsyslog server over TLS (OpenSSL)
