Technical Tip: Resolve connectivity issues between FortiSIEM and FortiEDR
| Description | This article describes how to resolve any connectivity issues between FortiSIEM and FortiEDR. |
| Scope | FortiSIEM. |
| Solution | After performing the first verification steps through the documents below: FortiSIEM and FortiEDR External Systems Configuration Guide FortiSIEM and FortiEDR Integration Setup
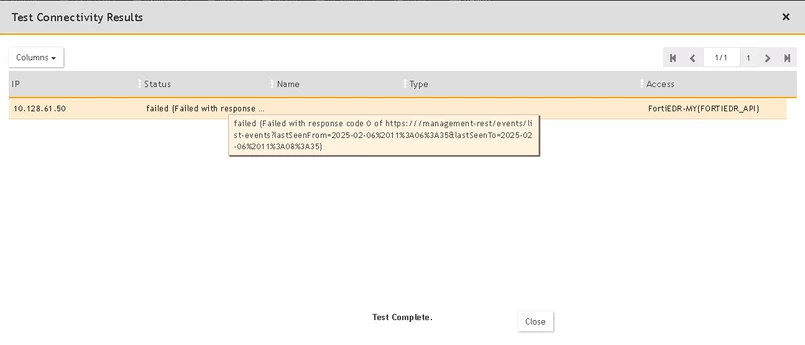
The following tests the connectivity issue of FortiEDR under Admin -> Setup > Credentials. Test Connectivity can be observed below:
The URL is missing https://(FortiEDR HOST IP)/management-rest. Connectivity from FortiSIEM to FortiEDR URL on port 443 needs to be verified further:
# curl -v -k https://(FortiEDR Host IP)/management-rest/
Verify through phoenix.log from the FortiSIEM discovering node - Supervisor or Collector:
2025-02-06T12:49:52.916993+08:00 fortisiem phDiscover[8914]: [PH_AGENTMGR_SERVER_IP_RESOLVE_WARNING]:[eventSeverity]=PHL_WARNING,[procName]=phDiscover,[fileName]=phBaseAgent.h,[lineNumber]=141,[serverIpAddr]=10.128.61.50,[jobName]=,[phLogDetail]=Could not resolve server IP
Workaround:
On the FortiSIEM discovering node, SSH intothe Supervisor or Collector:
# vi /etc/hosts
Add the hostname of FortiEDR to resolve the connection:
10.128.61.50 <hostname of FortiEDR>
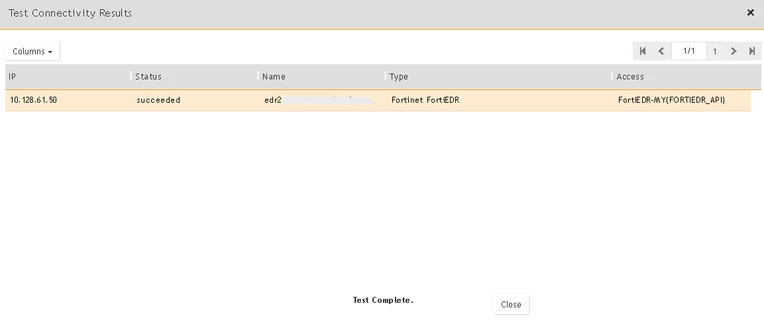
This will allow the test connection to be successful:
|