


Detecting 3-Day Sustained NAC Breach Using Rule Logic in FortiSIEM
Overview:
In NAC-based environments, it's common to see compliance violations or host breaches reported daily. However, not all of them require immediate action—especially if they self-remediate. The real concern arises when a host remains non-compliant for consecutive days [Taking 3 days as an example].
In this post, I’ll walk you through how to design a correlation rule that ignores isolated Day-1 and Day- 2 alerts but fires only when the same host is non-compliant over 3 days—a common compliance logic for risk-aware environments.
Objective:
Trigger an alert only if a host remains in NAC breach for 3 continuous days. As Saturday and Sunday is Holiday- Thursday, Friday and Monday would be only trigger an alert.
Rule Design Philosophy:
Skip isolated or sporadic violations.
Only trigger if breach continues beyond 48 hours (i.e. on the third day).
Prevent noise from multiple Day-1 alerts or flapping.
Pattern Configuration:
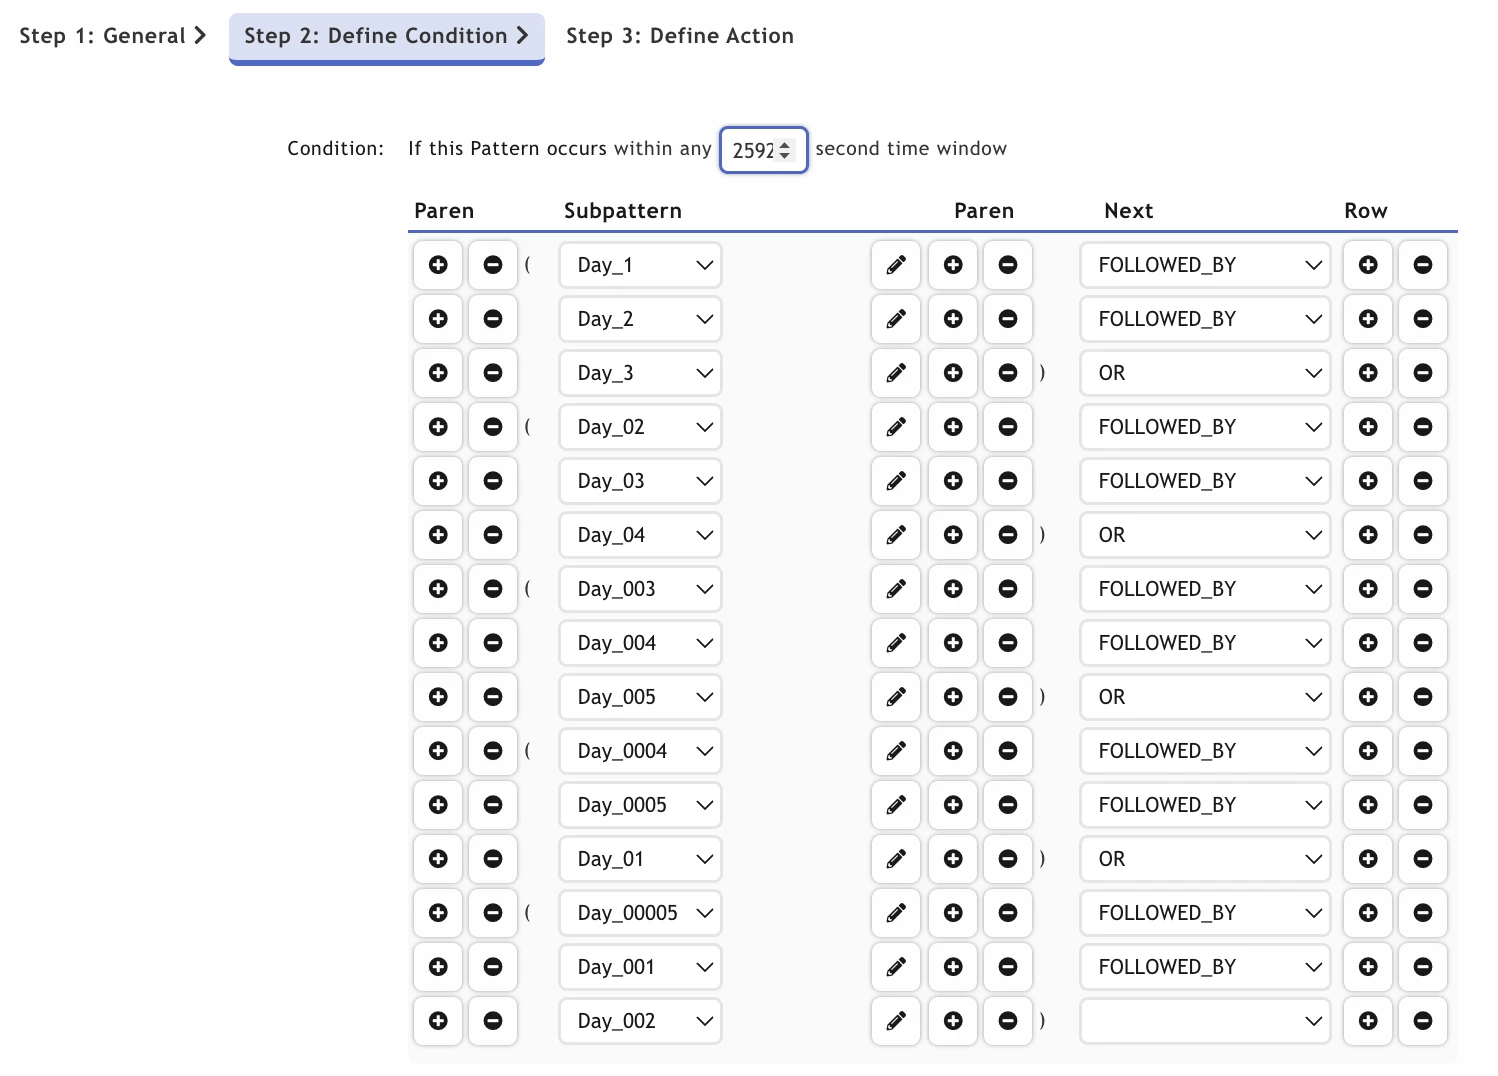
Time Window:
Set a time window wide enough to allow detection across 3 days, e.g.:
Tip:
If your source system uses inconsistent naming (e.g. Day_1, Day_01, Day_001), make sure to include all formats in pattern logic.
Always test with historical logs to ensure detection is not too restrictive or too noisy.
Use Case Impact:
This rule is very useful in enterprise SOC environments where:
NAC breaches are frequent but mostly self-remediating
Security teams want to focus on persistent compliance failures
Helps prioritize response to meaningful threats instead of chasing false alarms
Final Note:
Feel free to copy the pattern logic into your own FortiSIEM. If you have different naming conventions, just update the subpattern values.
Let me know if you'd like a ready-to-import JSON or help tuning it to your log format.

