Troubleshooting Tip: FortiSASE VPN connection stuck at 45% with event log 'sslvpn_login_no_matching_policy'
| Description | This article describes how to fix the FortiSASE VPN connection issue with FortiAuthenticator used as authentication server. |
| Scope | FortiSASE. |
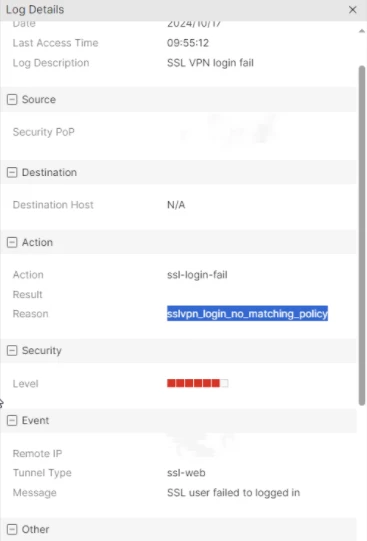
| Solution | VPN connection gets stuck at 45% and the following log will be present under Analytics -> Events.
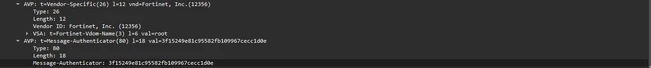
FortiAuthenticator is used as a RADIUS server and the sniffer on the FortiSASE instance would show the message-authenticator attribute being sent in Access-request however the authentication would fail with the debug log.
The following logs can be noticed in the debug which shows the server is responding without the Message-Authenticator attribute.
2024-10-17 09:25:09 [1522] fnbamd_auth_handle_radius_result-Timer of rad 'FortiAuthenticator' is deleted
Also, the RADIUS config under FortiSASE would show 'Invalid secret' while performing Test Connection. The secret change would not help in this scenario. The behavior change is due to mitigating RADIUS Protocol CVE-2024-3596. Refer CVE-2024-3596. The solution would be to upgrade FortiAuthenticator to 6.4.10, 6.5.6, 6.6.2, or 7.0.0. FortiAuthenticator 6.6.2 is currently released, and the rest are expected to be released shortly. |