
Troubleshooting Tip: FortiSASE SAML VPN Authentication Failure for AD-Integrated Users on FortiAuthenticator
Description
This article describes a scenario where FortiSASE SAML VPN authentication succeeds for local FortiAuthenticator users but fails for Active Directory (AD)–integrated users and how to troubleshoot it.
Scope
FortiSASE, FortiAuthenticator.
Solution
Users connect to the VPN in FortiSASE using SAML, with FortiAuthenticator acting as the IdP. The VPN connection works successfully for local users created on FortiAuthenticator.
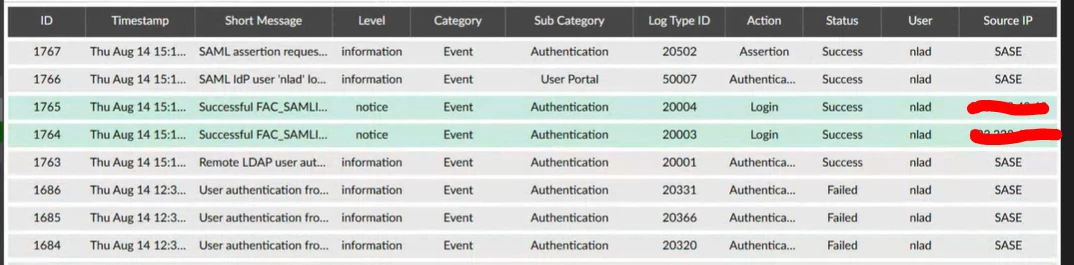
However, when LDAP is integrated on FortiAuthenticator, the VPN connection fails for remote AD users. LDAP connection on the FortiAuthenticator is up and is able to import the AD user successfully on the FortiAuthenticator.
Verify that the required realm is created and properly linked to the LDAP user source configuration.
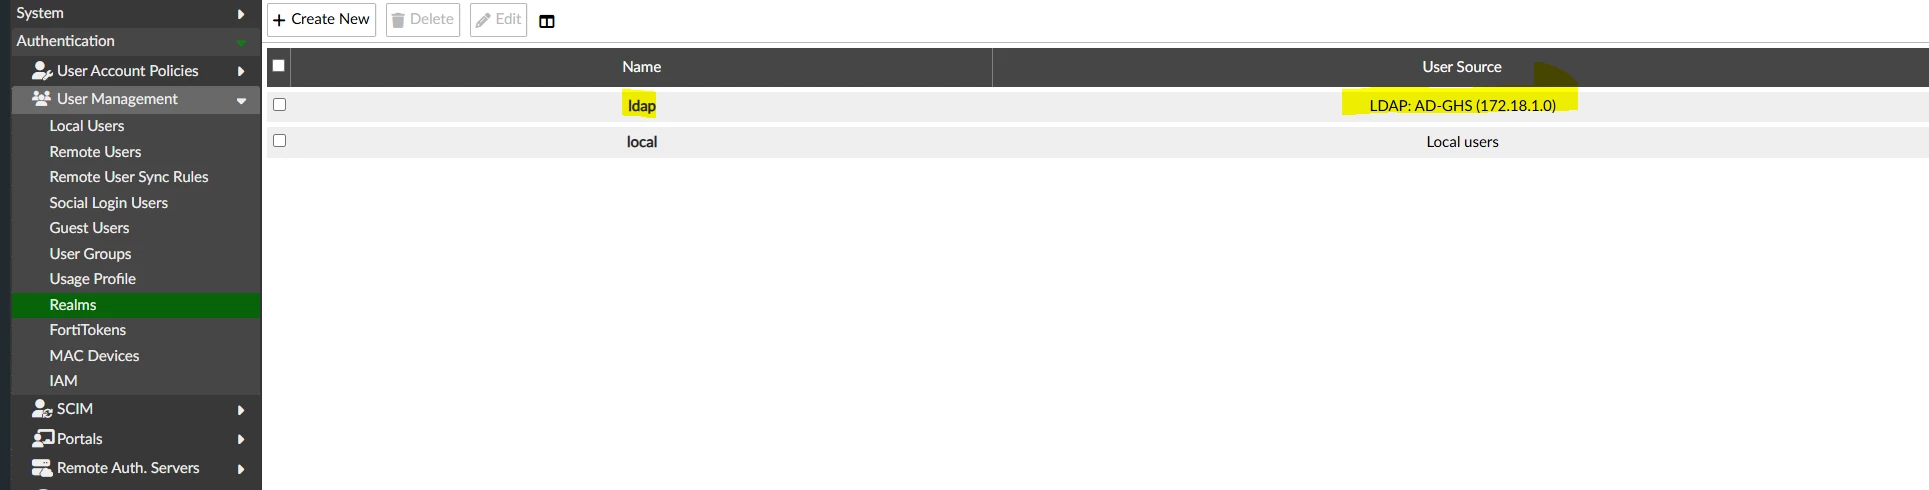
Only the local user realm is configured, and no realm exists for LDAP users. As a result, authentication fails when an LDAP user attempts to connect to the FortiSASE VPN.
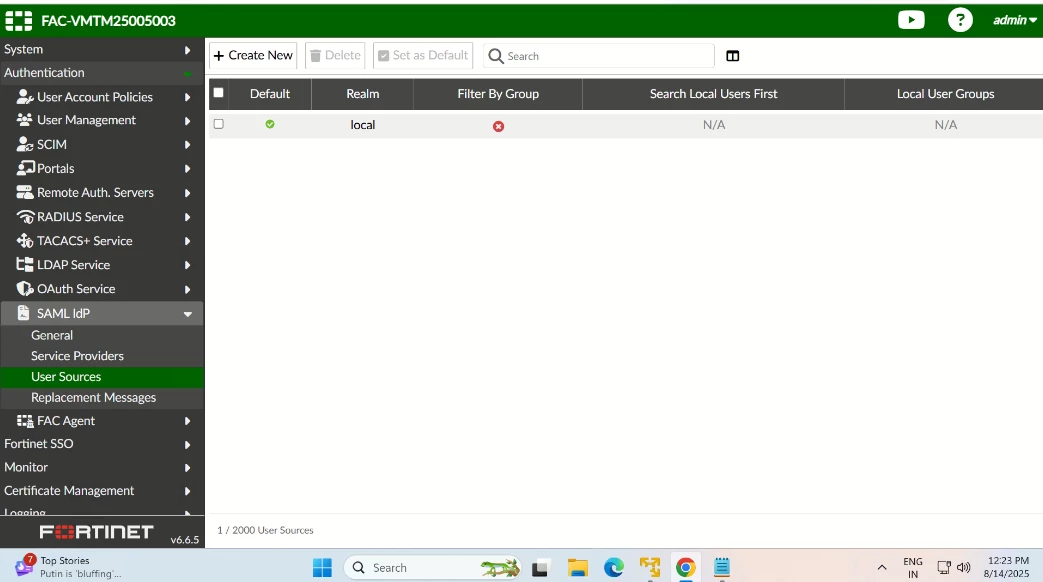
Create a new User Sources under Authentication -> SAML IdP -> User Sources and set the LDAP realm as the default.
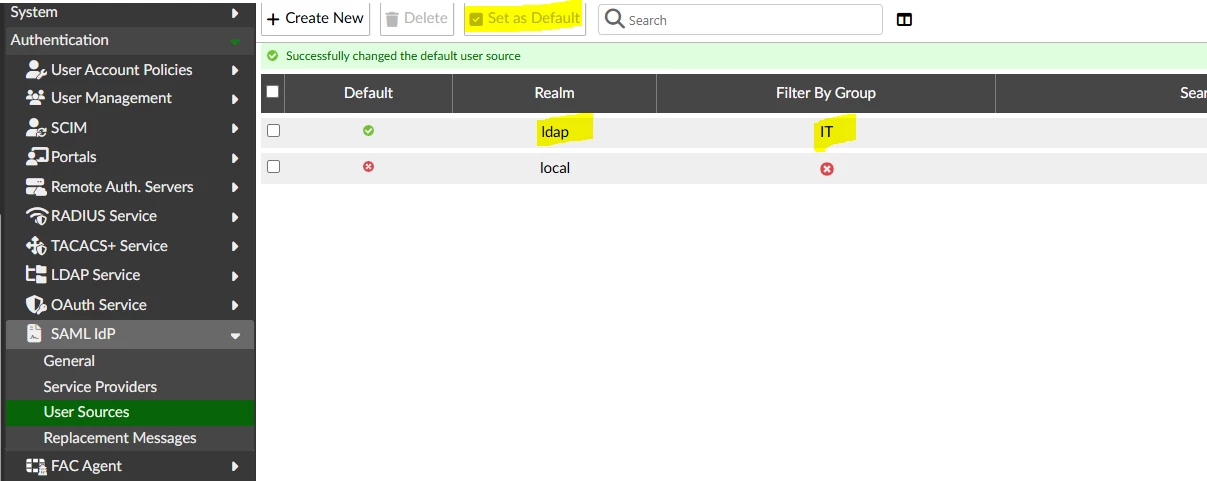
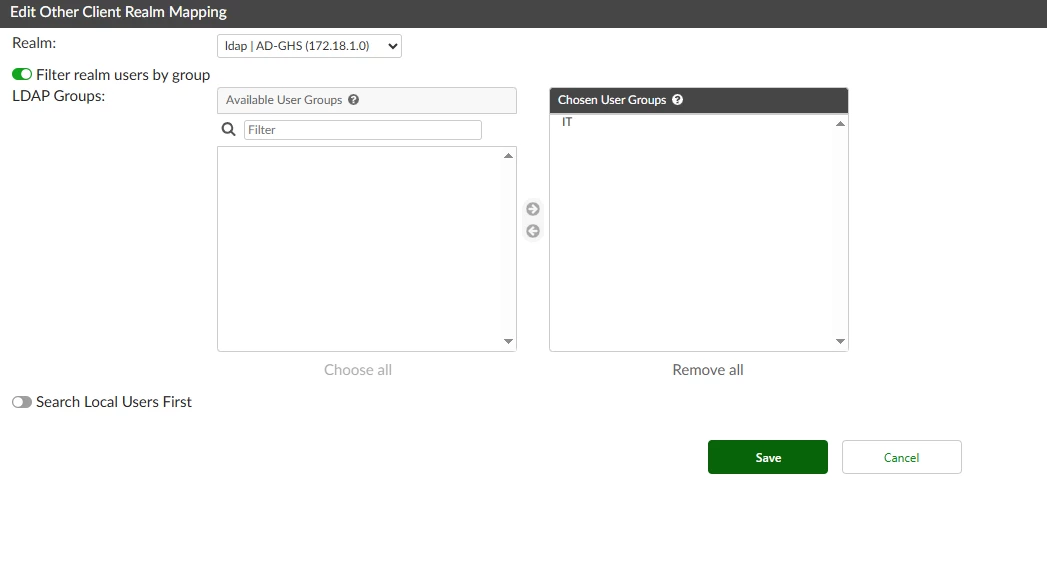
Remote AD users can now connect to the FortiSASE VPN, resolving the previous authentication failures.