Step 1 - Validate the Issue.
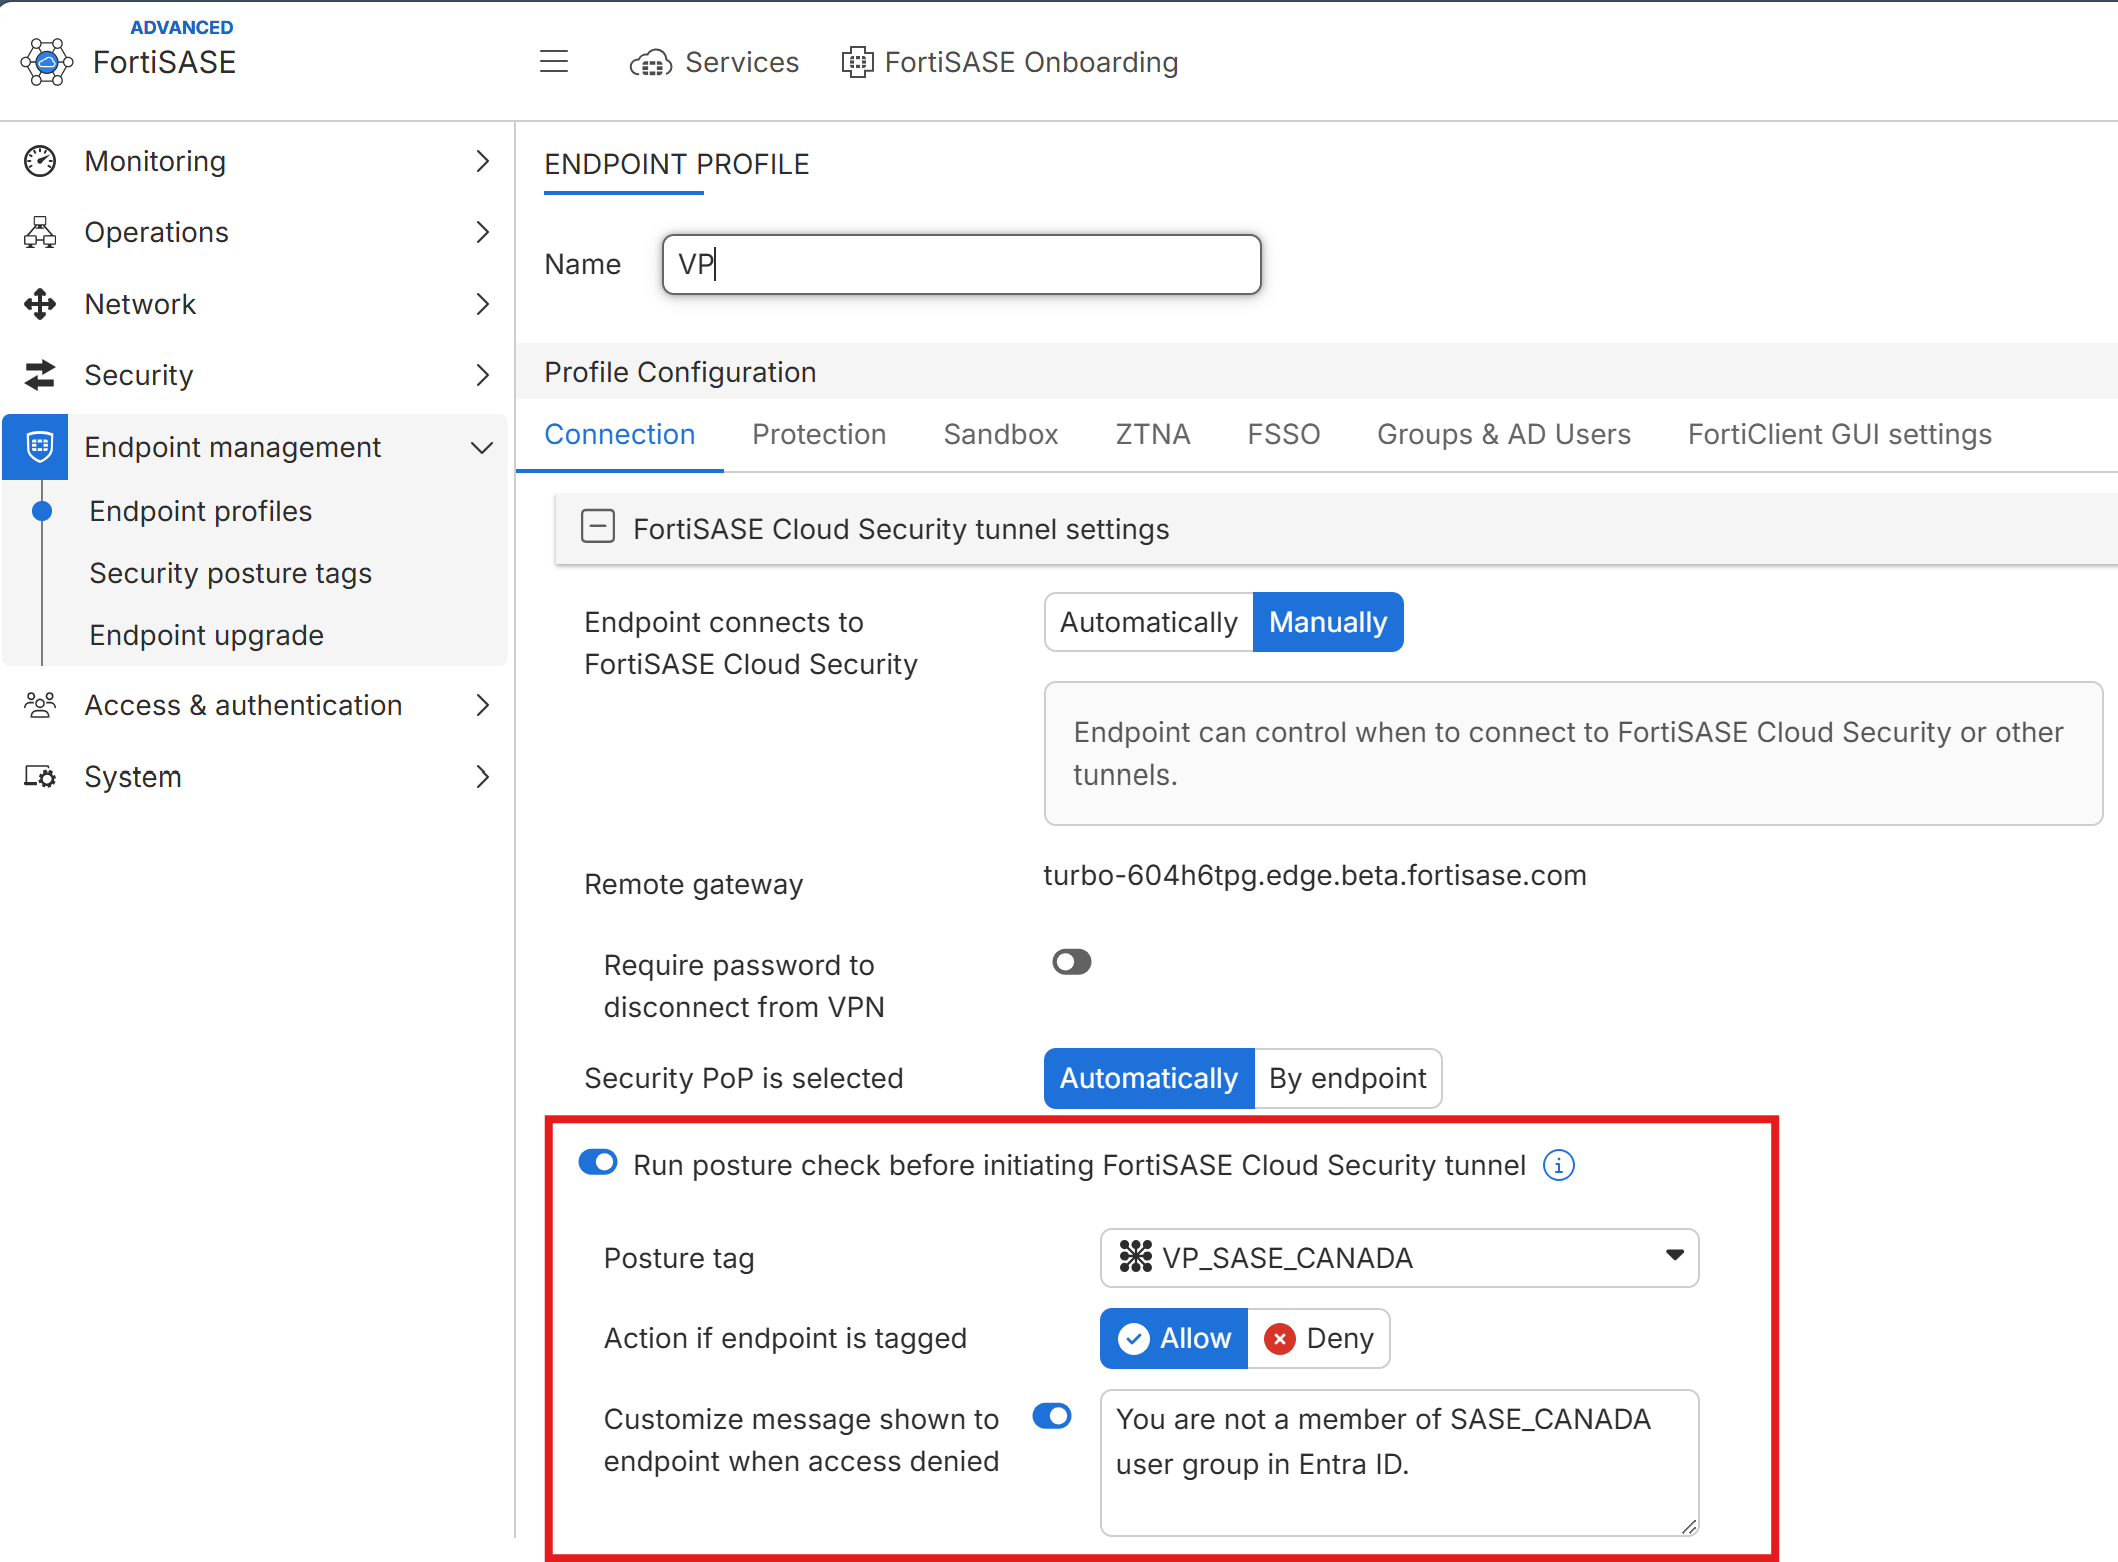
First, if not set, configuration of the customizable message is highly encouraged not only from the user experience perspective but also from a troubleshooting standpoint as it clearly communicates the issue is with the posture check.
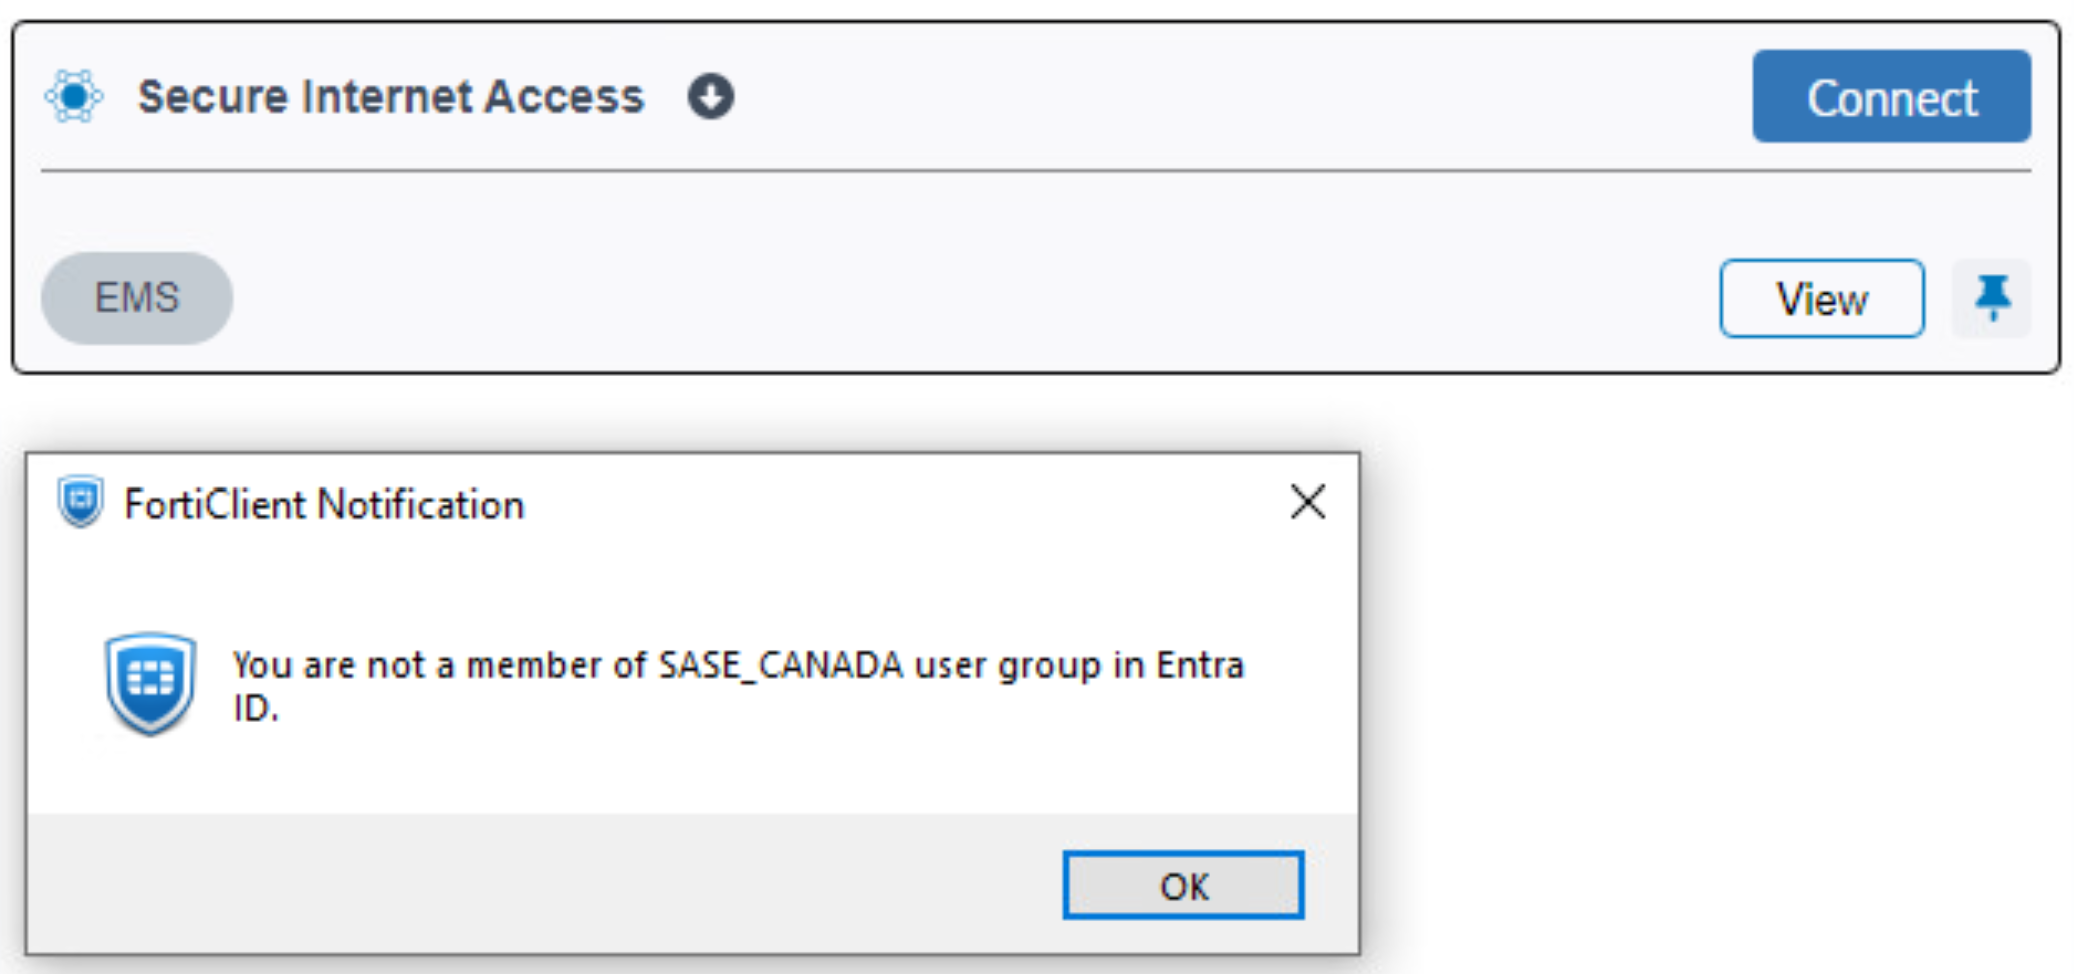
Otherwise, a generic error is presented (FortiClient v7.4.6):
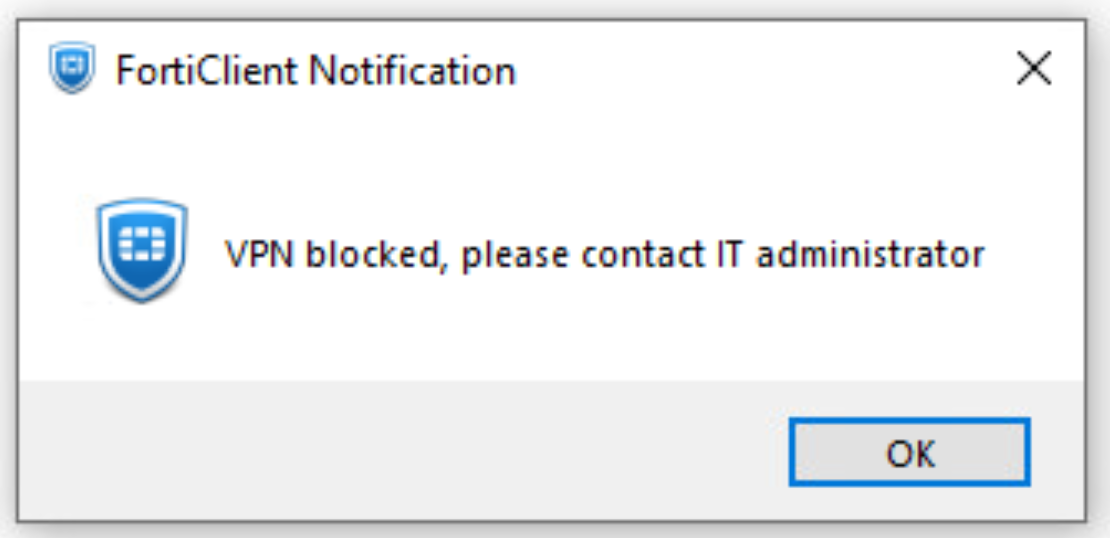
To validate the exact reason for the block, verify the FcVpnSched.log.
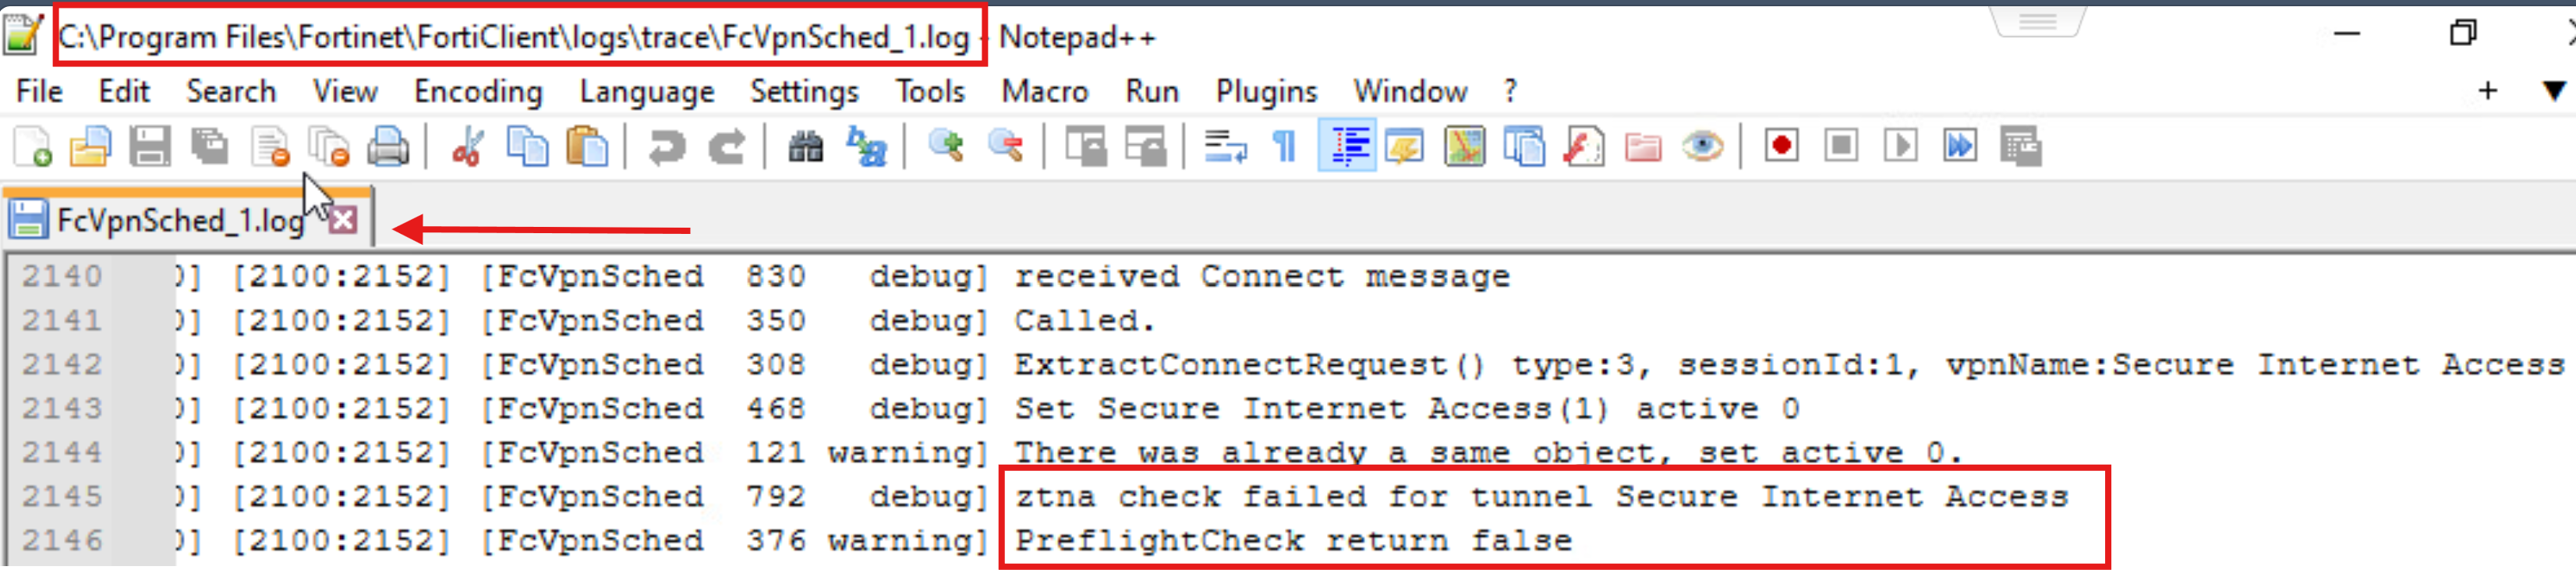
Step 2 - Check tag requirements for posture verification.
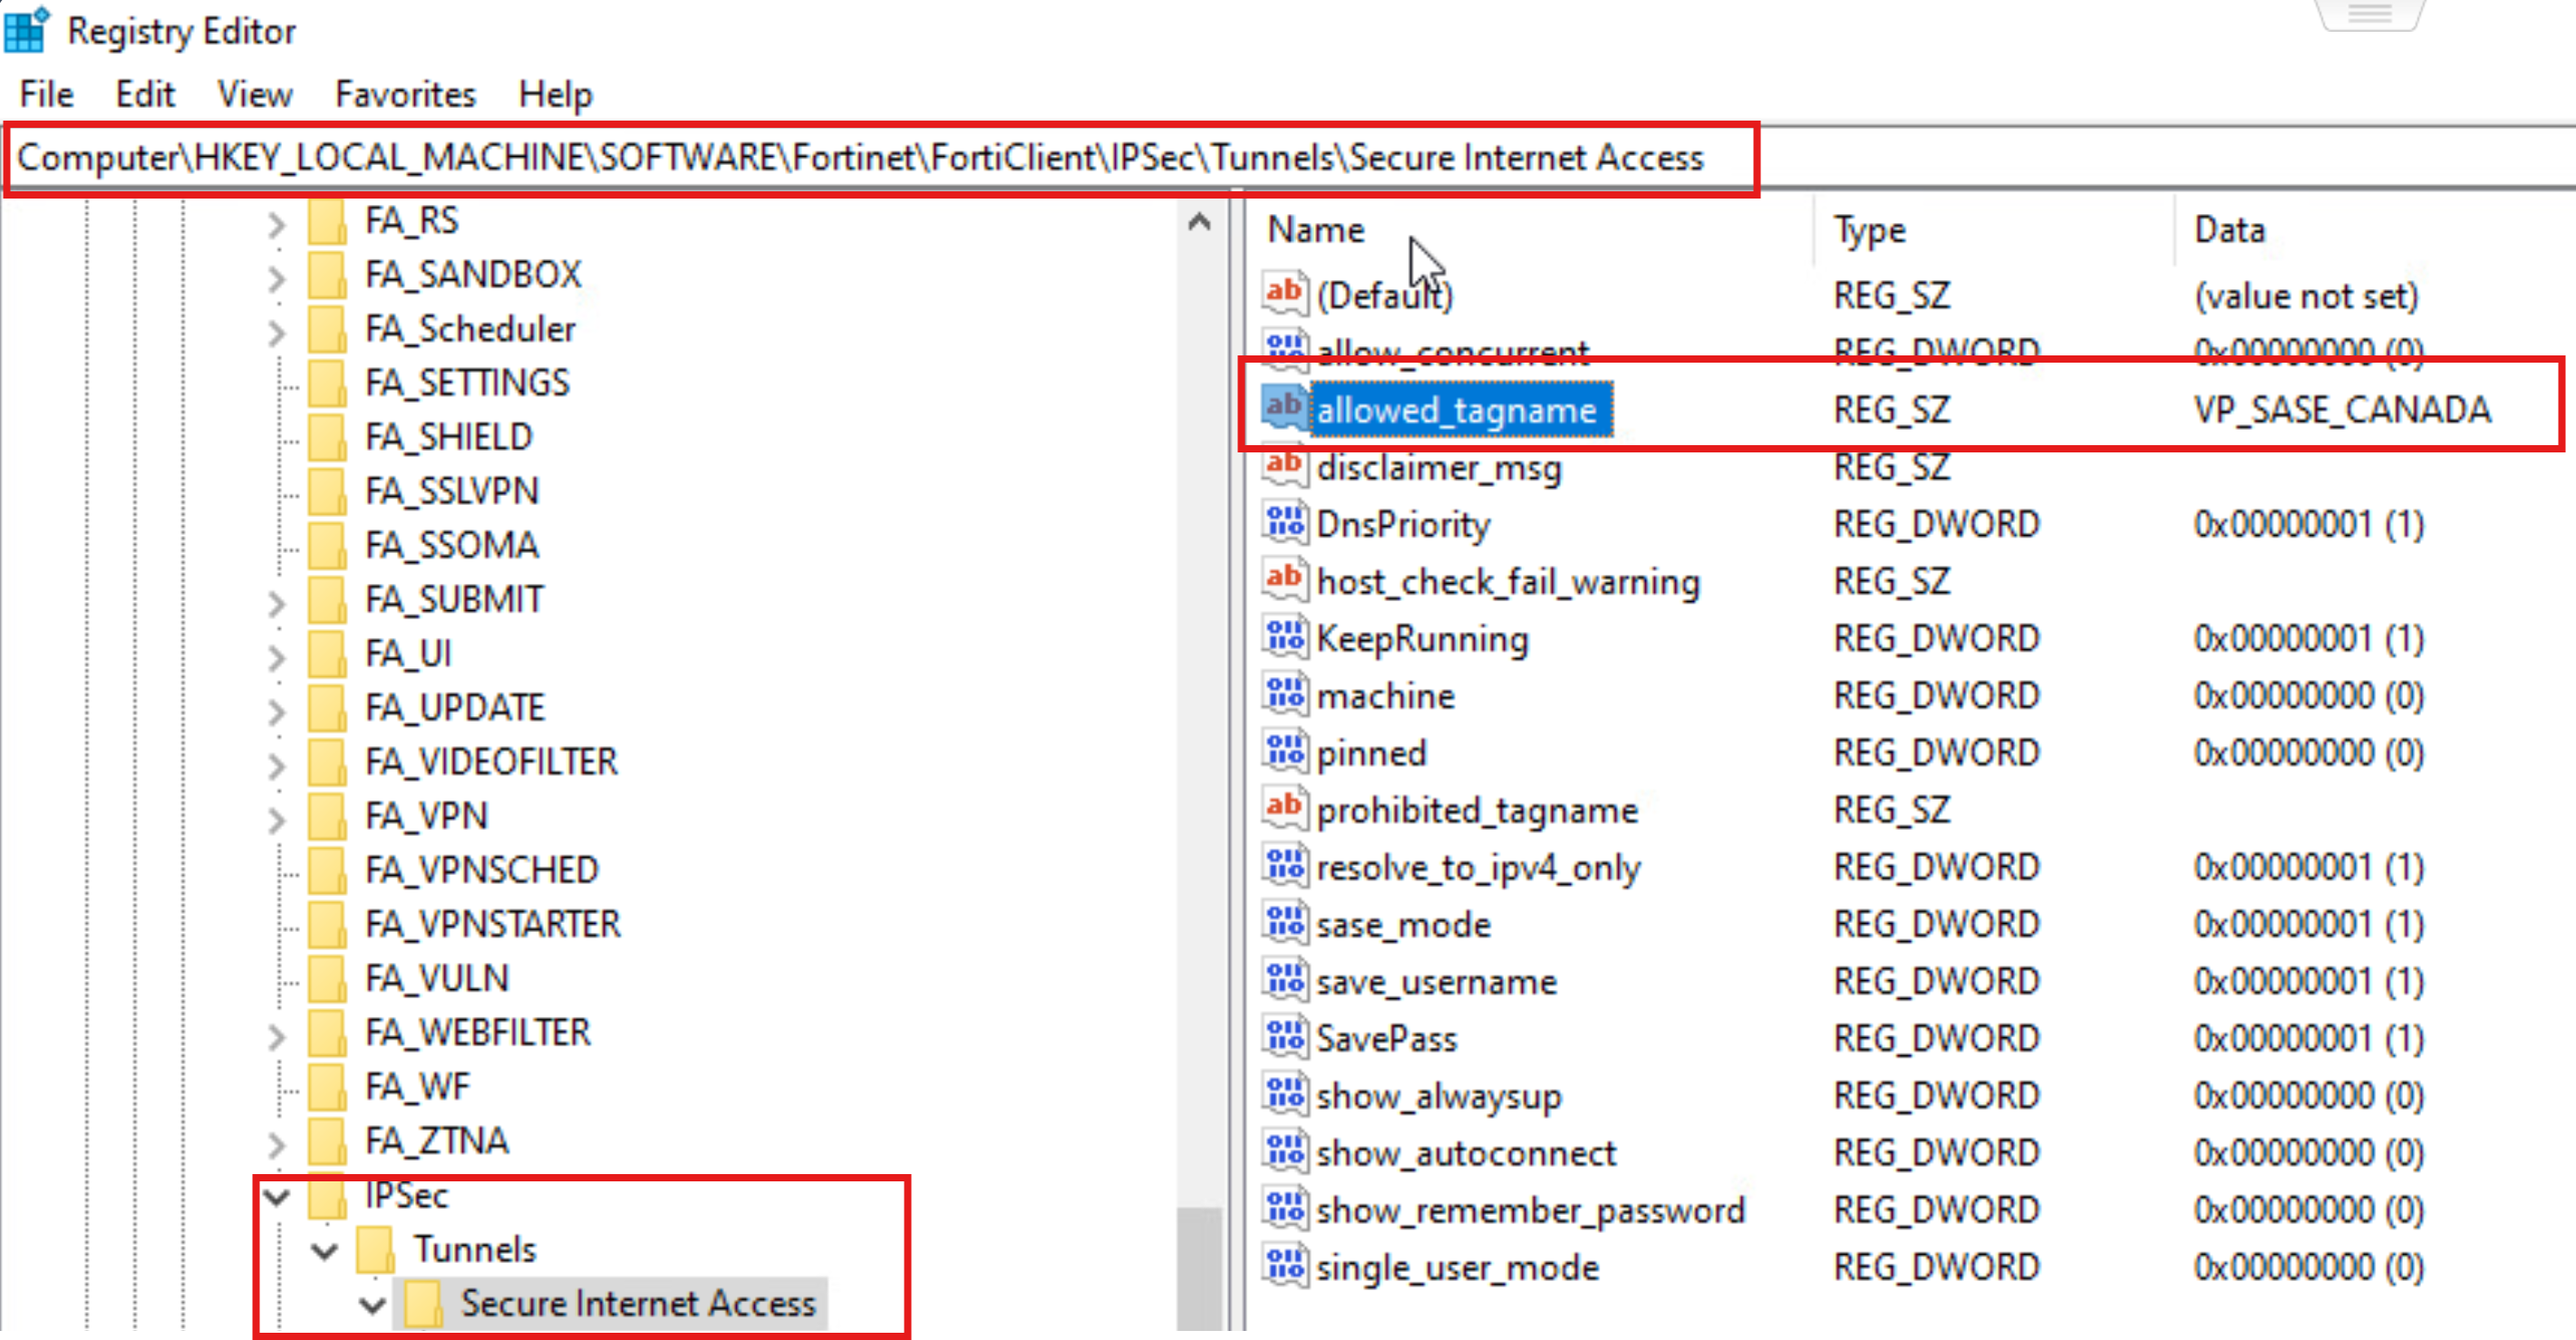
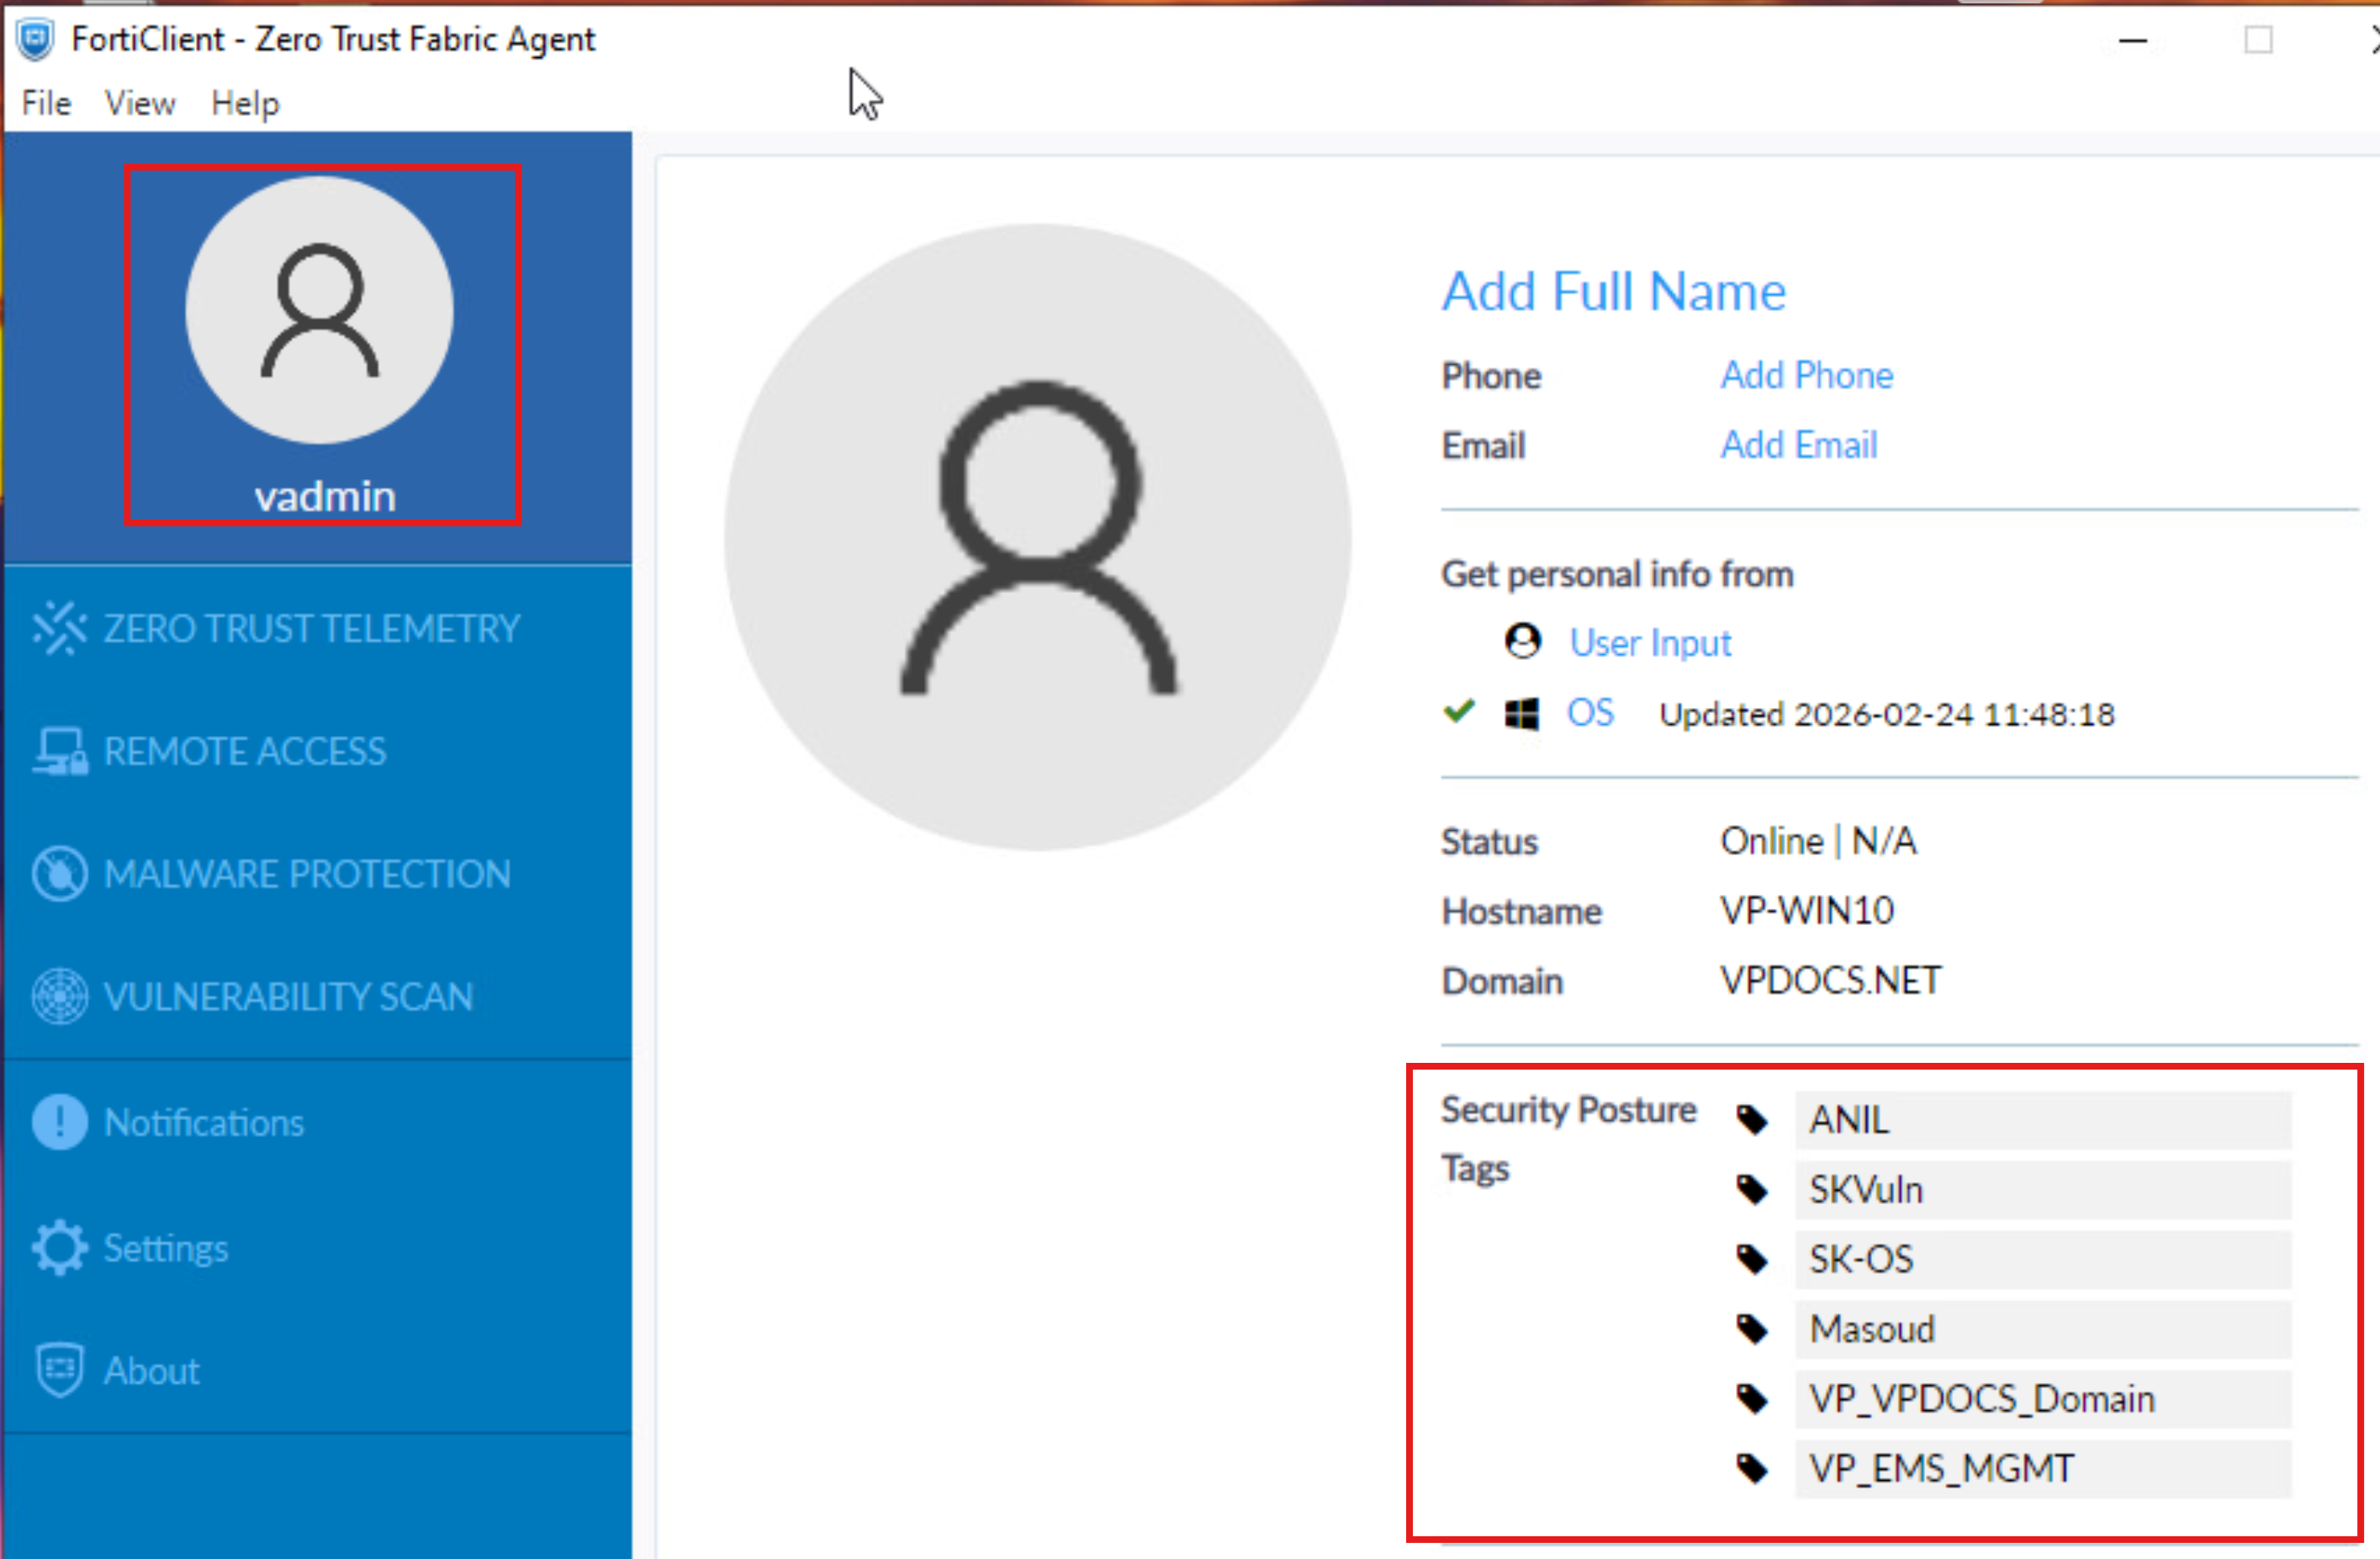
The next step (especially important if access to FortiSASE GUI is unavailable) is to check what tag is required for successful connection and what tags the endpoint has been assigned with.
To check the posture check requirement, use Registry Editor and navigate to Computer\HKEY_LOCAL_MACHINE\SOFTWARE\Fortinet\FortiClient\IPSec\Tunnels\<Tunnel Name> to validate the allowed_tagname registry entry.
To confirm what tags are assigned to the endpoint, select the user's avatar and check the Security Posture Tags section (it may have to be explicitly configured via endpoint profile to be visible).
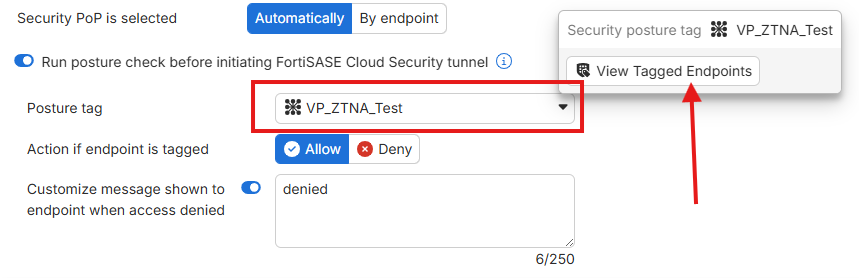
The information above can be confirmed within the FortiSASE GUI console:
For tags enforced for VPN posture, check Endpoint Management -> Endpoint profiles -> profile -> Connection. For tags assigned to an endpoint, see Operations -> Endpoints -> endpoint -> FortiClient -> Tags assigned.
Tip: Hover the mouse over the tag required for the posture check and select the tagged endpoints.
Step 3 - Verify the tagging rules the tag is comprised of.
Once tag requirements for successful VPN connection are validated, check what rules the tag is comprised of and which ones specifically the endpoint is not compliant with.
On FortiSASE, cross-reference a tag enforced in the profile against a tagging rule set the tag is comprised of.
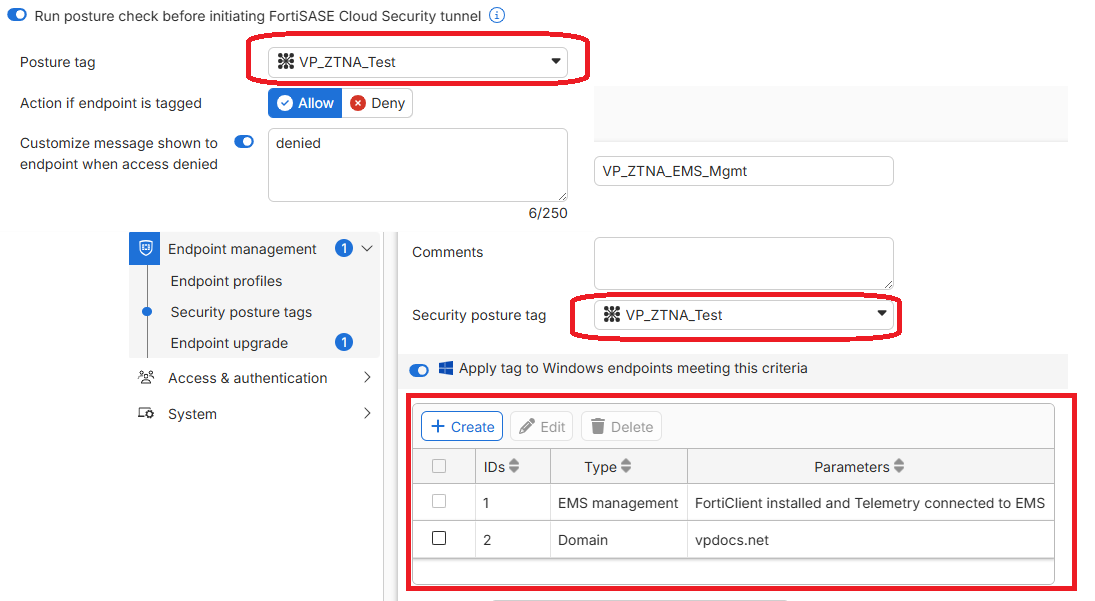 Tip: The steps above can also be performed without access to the FortiSASE console by performing them directly on the endpoint.
To verify the rules, check host_verification.plain located under the C:\Program Files\Fortinet\FortiClient\logs\ec folder.
A complete process is described in Troubleshooting Tip: Identifying Criteria Endpoint Does Not Match When Posture Tag is Comprised of Multiple Tagging Rules.
Step 4 - Evaluate what tagging rules the endpoint is not compliant with.
Next, navigate to C:\Program Files\Fortinet\FortiClient\logs race and open the most recently updated FortiESNAC.log file.
During every KA interval, FortiClient verifies whether the endpoint is compliant with every rule recorded in host_verification.plain. The evaluation process starts with the rules having a higher rule flag number. The following is an example of a FortiESNAC log showcasing evaluation of the tag called VP_Compliant that is comprised of three rules with flags 93, 76, and 15:
[2026-05-21 11:59:59.8306310 UTC-07:00] [1500:4828] [FortiESNAC  1819   debug] checking rule 93
[2026-05-21 11:59:59.8306687 UTC-07:00] [1500:4828] [FortiESNAC  1639   debug] checkrule unsupported feature=fct_version
[2026-05-21 11:59:59.8306699 UTC-07:00] [1500:4828] [FortiESNAC  1895   debug] rule VP_Compliant is not matched
...
[2026-05-21 11:59:59.8322792 UTC-07:00] [1500:4828] [FortiESNAC  1819   debug] checking rule 76
[2026-05-21 11:59:59.8323237 UTC-07:00] [1500:4828] [FortiESNAC  1639   debug] checkrule unsupported feature=ems_management
[2026-05-21 11:59:59.8323252 UTC-07:00] [1500:4828] [FortiESNAC  1895   debug] rule VP_Compliant is not matched
...
[2026-05-21 11:59:59.9003800 UTC-07:00] [1500:4828] [FortiESNAC  1819   debug] checking rule 15
[2026-05-21 11:59:59.9229845 UTC-07:00] [1500:4828] [FortiESNAC  1895   debug] rule VP_Compliant is matched
FortiClient only assigns the last rule of the tag after checking it (the logic dictates all rules must match).
Following the steps above should be sufficient to understand why the endpoint does not quality for connecting to a VPN tunnel protected with a Posture Check verification.
Note: Tagging rules evaluation occurs either on the endpoint side by FortiClient (rule types like Domain or Antivirus) or on the FortiSASE Endpoint Management Server (EMS) - these rules are marked with a checkrule unsupported log in FortiESNAC.
Related article:
Troubleshooting Tip: Identifying Criteria Endpoint Does Not Match When Posture Tag is Comprised of Multiple Tagging Rules |