

ihaidar
Staff
Staff
September 23, 2025

Troubleshooting Tip: FortiSASE endpoints cannot connect to VPN using SAML

  • September 23, 2025
  • 0 replies
  • 451 views
Description This article describes an issue where a FortiClient VPN using SAML authentication fails to connect when the lockdown grace period for endpoints is set to zero.
In this case, FortiClient remains stuck on 'connecting'.
Scope FortiSASE, FortiGate.
Solution

SAML logs show successful authentication followed by an immediate logout.


The lockdown grace period for endpoints was set to zero seconds. This caused FortiClient to fail during the transition phase, as the endpoint did not have sufficient time to complete SAML authentication.


Fix:
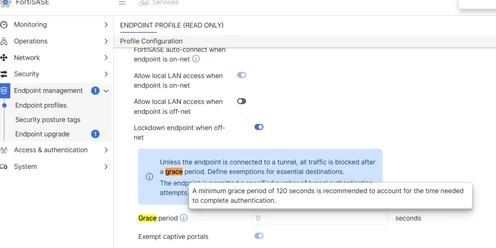

Update the lockdown grace period to 120 seconds. This value provides enough time for the authentication process to complete successfully. After applying this configuration, VPN connections using SAML authentication were established successfully. As shown in the below screenshot, Go to Endpoint profile -> Select the Profile name -> Select 'Connection' and change the value of the Grace period from zero to 120 Seconds.


KB2.png
    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!

