



Troubleshooting Tip: Error: Steering bypass destinations not working in FortiSASE
Description
This article describes the issue where steering bypass destinations fail to work as expected in FortiSASE, along with potential causes and troubleshooting steps to resolve the problem
Scope
FortiSASE.
Solution
Users reported that printing does not work when connected to VPN via FortiSASE. However, once the VPN is disconnected, printing works as expected.
- Environment:
The user is connected to the corporate network (LAN) in the office. - Printers are locally hosted on the LAN and should not route through the FortiSASE tunnel.
Printer IPs:
Xerox: 192.168.1.174.
Canon: 192.168.1.175.
Root Cause.
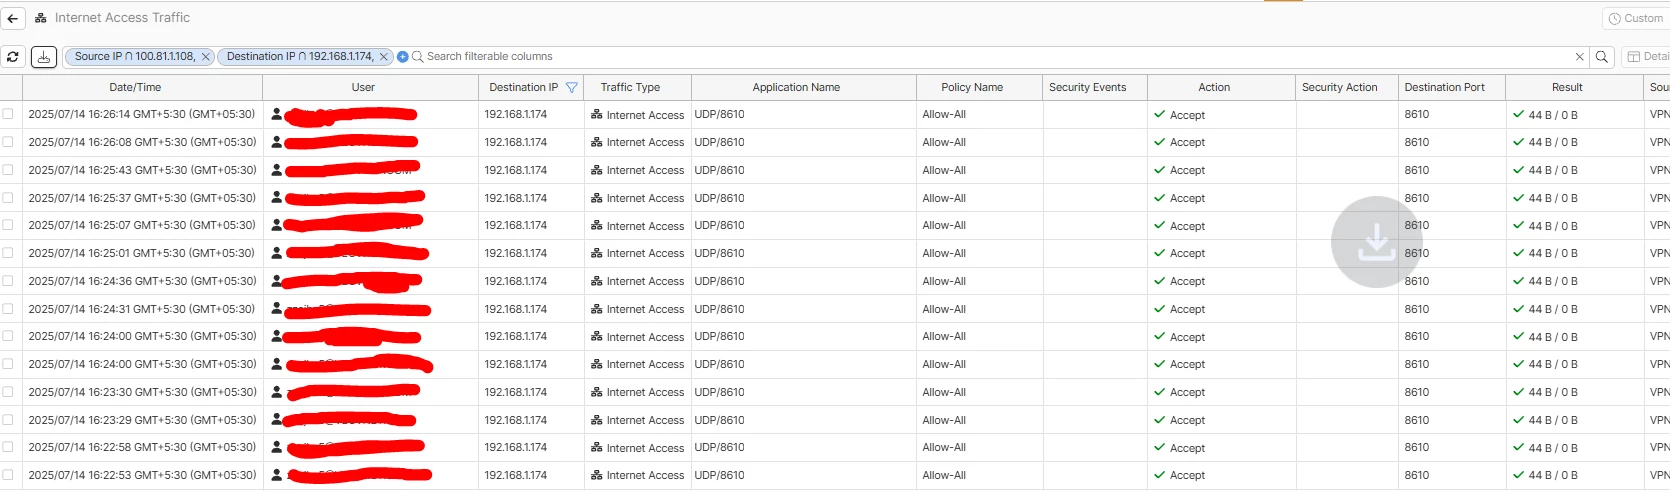
Traffic to the printer IPs was being routed through the FortiSASE tunnel instead of the local LAN.
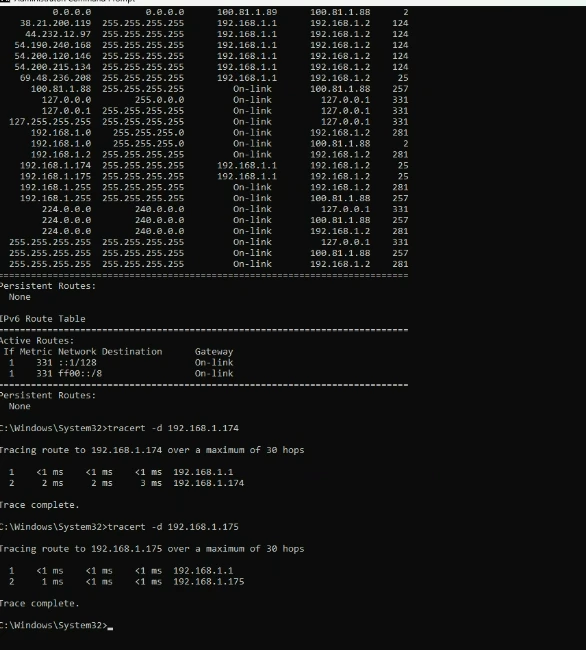
From the session logs and traceroute results, it was confirmed that printer traffic was reaching the FortiSASE infrastructure.
The endpoint matched the default endpoint profile, and bypass destination rules for the printer IPs were not configured.
Resolution Steps.
Bypass destination rules should be added for the printer IPs (192.168.1.174 and 192.168.1.175) in FortiSASE.
FortiSASE VPN needs to be reconnected to allow the endpoint to receive the updated routing configuration.
Post reconnection, a traceroute can be taken to confirm that traffic to the printers is being routed through the local LAN as expected.
Note: If any manual static route was added previously for the printers, it can now be safely removed, as the updated bypass rules handle the routing correctly.


