Errors may occur due to certificate revocation checks when using curl with FortiSASE, as shown below:
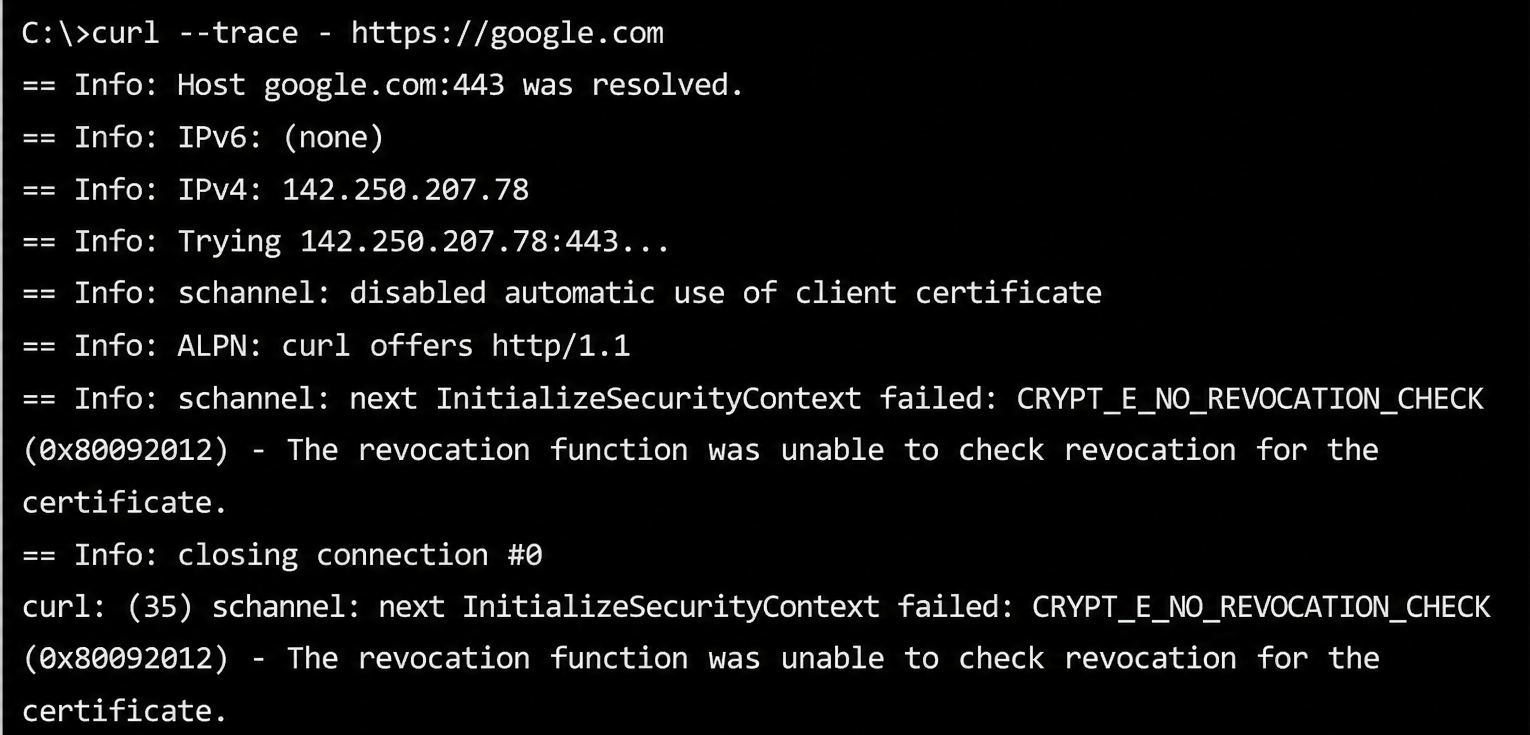
FortiSASE acts as a Man-In-The-Middle (MITM) and presents a self-signed certificate to the client.
Recognize that the self-signed certificate does not have a Certificate Revocation List (CRL) or Online Certificate Status Protocol (OCSP) details, which causes the revocation check to fail.
When client connects to a server over HTTPS, it verifies the server’s certificate chain for validity (revocation validation).
Actual certificate from website, while accessing directly includes the CDP as below against which the revocation check would be carried out.
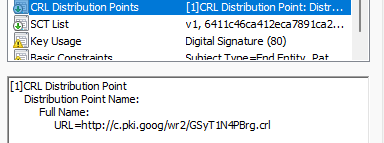
Upon accessing it while connected to FortiSASE, the client will be presented with a Fortinet self-signed CA which does not have CDP. This is expected with a self-signed/enterprise-signed/proxy, which prompts the following error:
* schannel: next InitializeSecurityContext failed: CRYPT_E_NO_REVOCATION_CHECK (0x80092012) - The revocation function was unable to check revocation for the certificate.
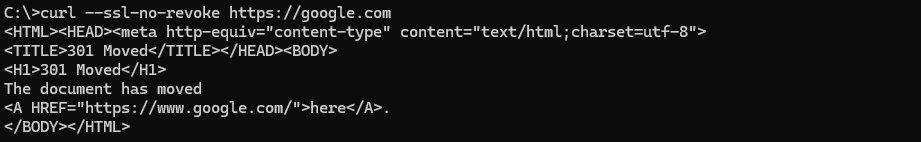
CURL will be successful after skipping the revocation check, as shown below:
Adding CURL.exe under steering bypass with local application path set to 'C:\Windows\System32\curl.exe' will not fix the issue as DNS-related issues will be encountered.
The SSL inspection level can be set to certificate inspection or no inspection.
| 



