Troubleshooting Tip: 'Authentication failed, session timeout' in FortiSASE secure web gateway (SWG)
| Description | This article describes the reason for the firewall authentication failure and session timeout when using FortiSASE SWG. |
| Scope | FortiSASE. |
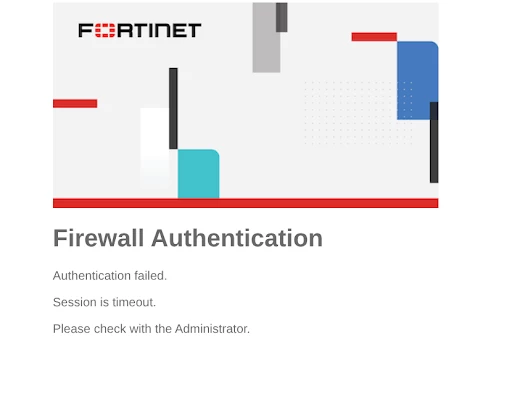
| Solution | When using a CSP_REPORT policy with a security profile configured with no SSL inspection, the following error might occur:
The SAML cookies authentication method relies on several factors, including:
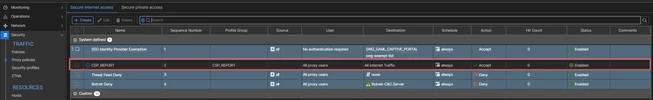
Since these elements are not included in the Content Security Policy (CSP) report, FortiSASE has introduced a new firewall policy above the SAML policy to allow SAML authentication.
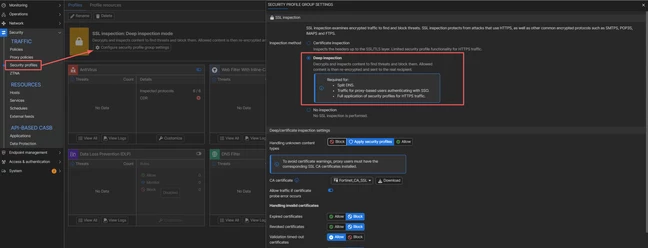
For the policy to function correctly, a security profile with Deep Packet Inspection (DPI) or certificate inspection is required.
Note: Due to a known issue reported under ID 1146409, a certificate inspection profile is required for the CSP_REPORT proxy policy instead of deep inspection when using Remote Browser Isolation (RBI).
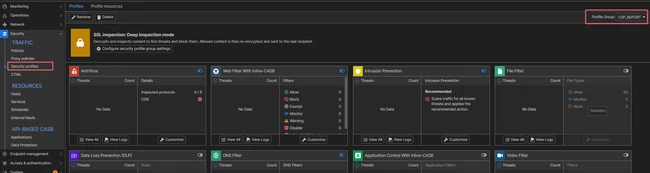
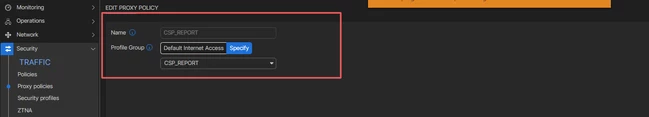
To assign a security profile with the Deep Packet Inspection, follow the steps below:
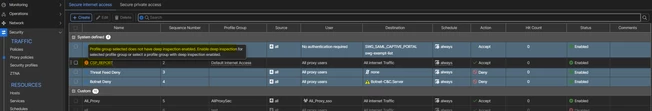
Note: When using a security profile with Deep inspection disabled, this policy show an red warning as illustrated below: |