ChrisTan
Staff
Staff
April 21, 2025

Technical Tip: How to use SNMP monitoring the backup VPN tunnel interface status.

Description This article describes how to use the correct FortiGate OID to monitor the status of the backup VPN tunnel.
Scope FortiGate.
Solution

When a backup VPN tunnel monitors the primary tunnel, the VPN tunnel is down, but the interface is still showing up:


fgt (backup) # show
config vpn ipsec phase1-interface
edit "backup"
set monitor "vpn1" <----- Monitoring the primary VPN tunnel.
end


fgt # get sys interface | grep backup
== [ backup ]
name: backup ip: 10.10.1.3 255.255.255.255 status: up <---- Interface showing up.


fgt # diagnose vpn tunnel list
list all ipsec tunnel in vd 0
------------------------------------------------------
name=backup ver=2 serial=9 10.56.245.147:0->10.56.245.148:0 nexthop=0.0.0.0 tun_id=10.56.245.148 tun_id6=::10.56.245.148 status=down dst_mtu=1500 weight=1  <-----Tunnel is down.
------------------------------------------------------


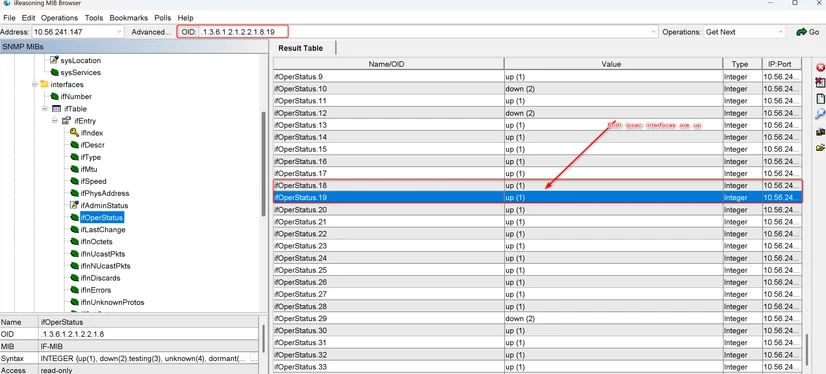
OID: .1.3.6.2.1.2.2.1.8 can only check the interface status so that the backup VPN would show up:


2025-04-21_10h57_54.png


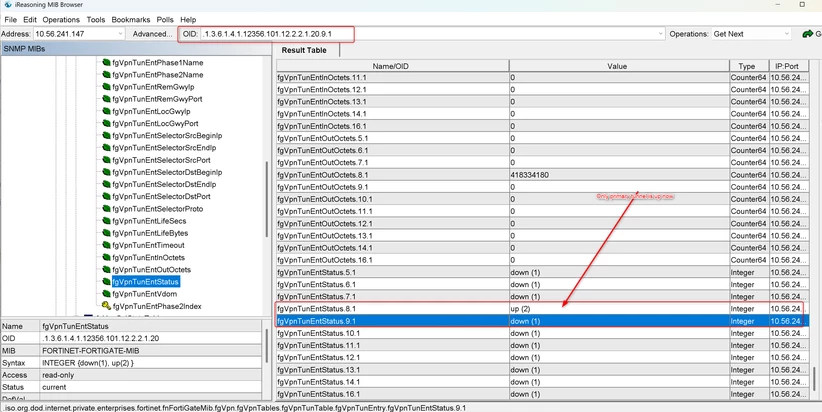
To check the VPN interface status, the FortiGate MIB file and FortiGate Core MIB file need to be loaded into the MIB browser. OID: 1.3.6.1.4.1.12356.101.12.2.2.1.20 would show the correct tunnel status:


2025-04-21_10h59_25.png


Related article:

Technical Tip: How to monitor the individual VPN tunnel by SNMP (OID)

    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.
    Security Operations Summit: Modernize SecOps. Operate AI-Native.AMER: November 4 | 9:00 AM PST. India and SAARC: November 5 | 10:00 AM IST. EMEA: November 5 | 10:30 AM CET. APAC: November 5 | 11:00 AM SGT