Technical Tip: How to apply bypass subnet in the FortiSASE
| Description | This article describes how to add subnets bypass in the FortiSASE. |
| Scope | FortiSASE. |
| Solution | The FortiSASE default route goes to SIA, but in the below situation: The PC IP address is 192.168.1.1/24, while the printer IP address is 192.168.2.1/24. The printer is unreachable once the SIA is connected.
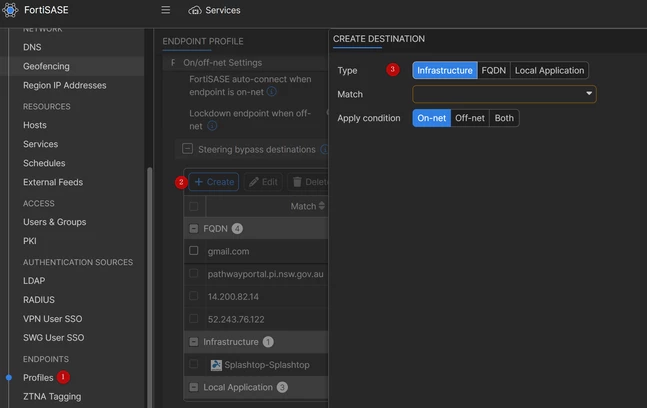
In this case, the subnet 192.168.2.0/24 should be bypassed and routed by the local gateway. In the FortiSASE customized profile, there are only three types of bypass:
Infrastructure, FQDN, Local Application:
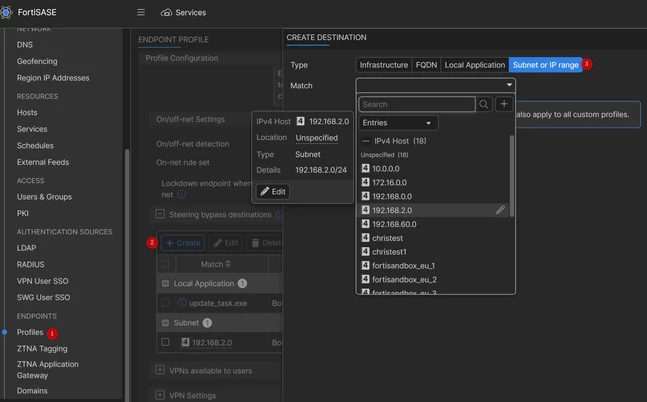
In the FortiSASE SSL Instances, the subnet will only be available in the default profile (refer to the note at the end of this article).
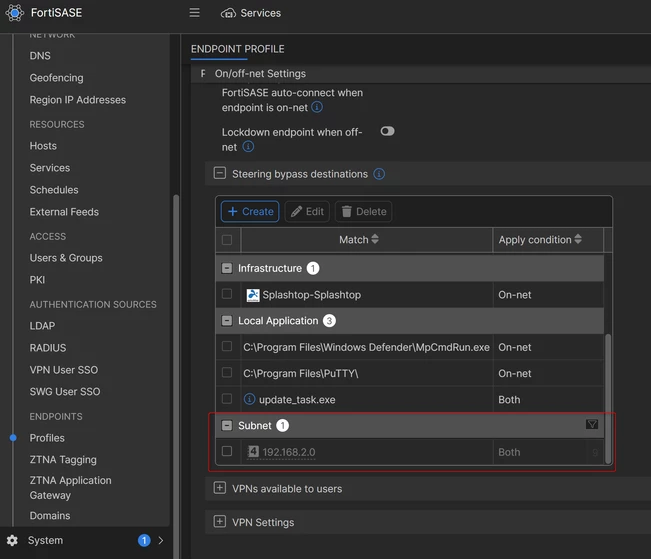
All profiles will apply once the bypass subnets are configured in the default profile, but it is greyed out and read-only:
The PC can reach the printer once the bypass subnet 192.168.2.0/24 is added.
The FortiClient config can be found in:
C:\Users\"username"\AppData\Local\FortiClient\fortisslvpn_xml.txt
It includes the below:
<split-tunnel-info negate='1'><addr ip='192.168.2.0' mask='255.255.255.0' /></split-tunnel-info>
The 192.168.2.0 255.255.255.0 goes to the local gateway and can also be found in the local PC 'route print'. Important Considerations:
FortiSASE with SSL VPN remote user connectivity:
FortiSASE with IPsec VPN remote user connectivity:
|